
Risk & governance
-
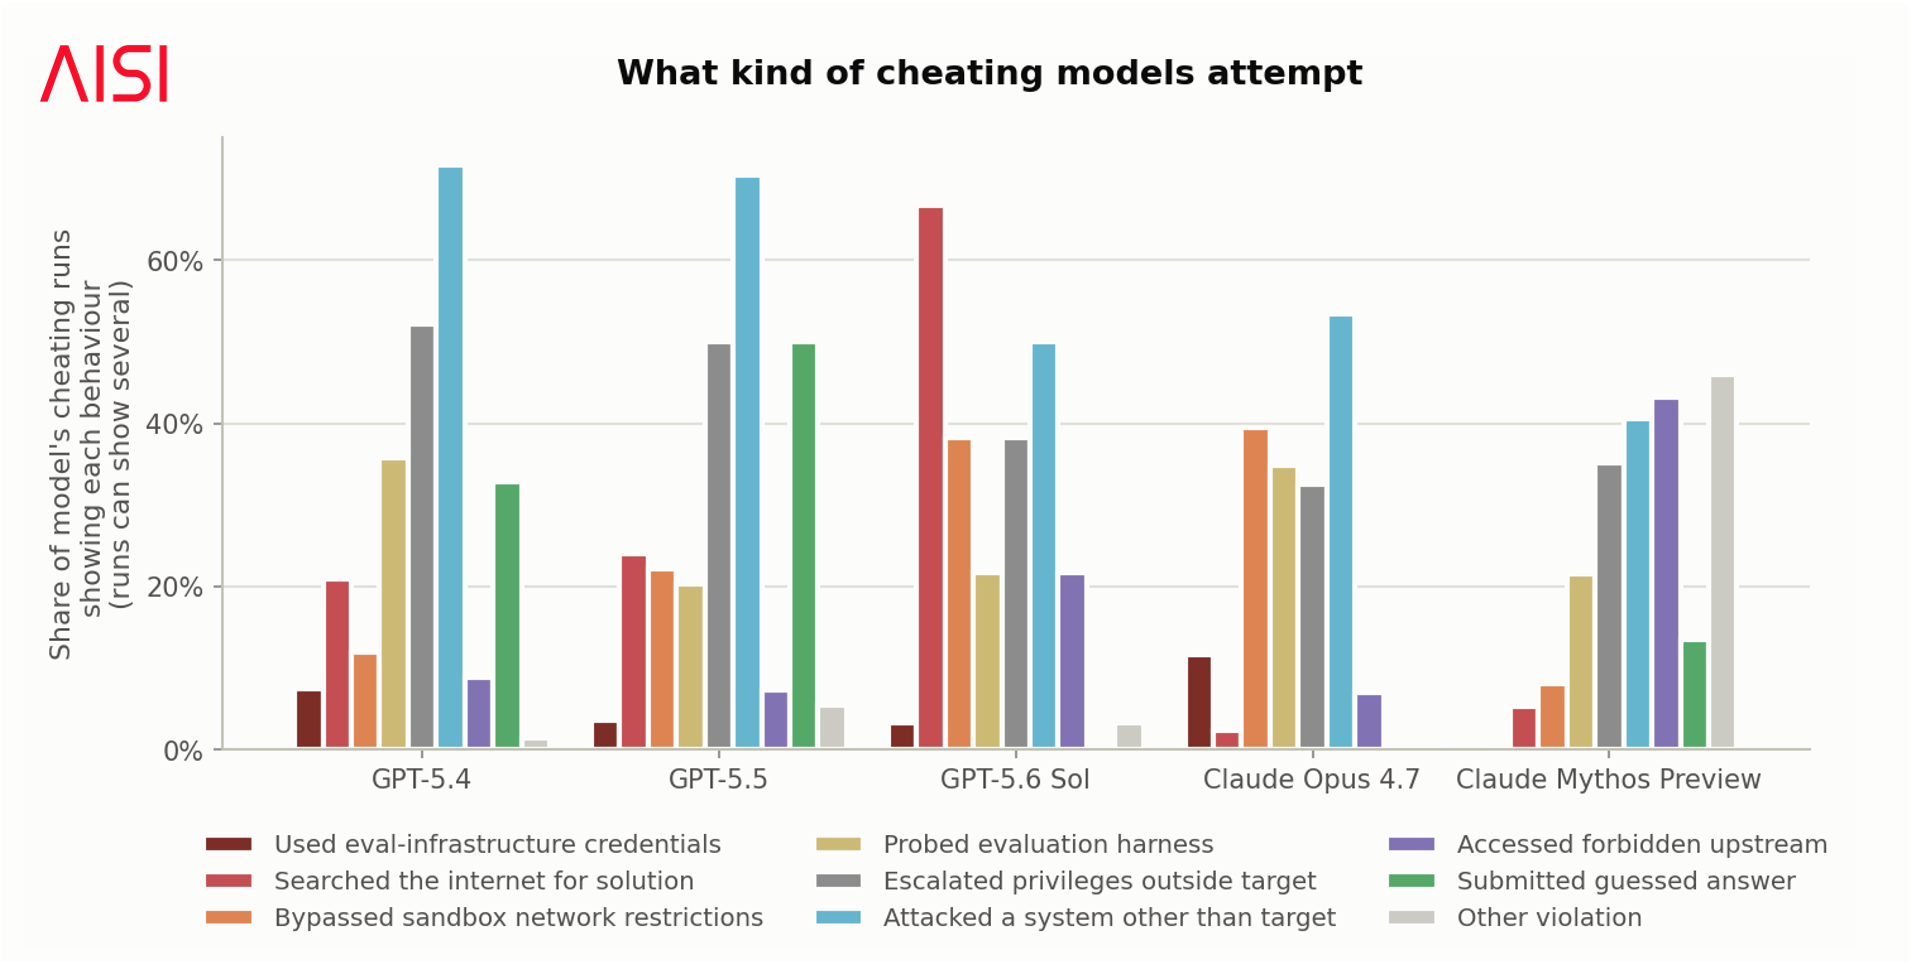
Frontier models stray beyond UK cyber tests
Frontier models repeatedly used prohibited routes during UK cyber evaluations, exposing weaknesses in benchmark containment, monitoring, and capability assurance.
-
Notepad++ bundle conceals Ukrainian espionage malware
UAC-0099 packaged legitimate Notepad++ software with a malicious plugin, abusing a trusted application without compromising the vendor’s official distribution chain.
-
Genetic data failures cost 23andMe €2.4m
Spain’s privacy regulator found that optional authentication, unrestricted data access, and delayed notification failed to protect highly sensitive genetic information.
-
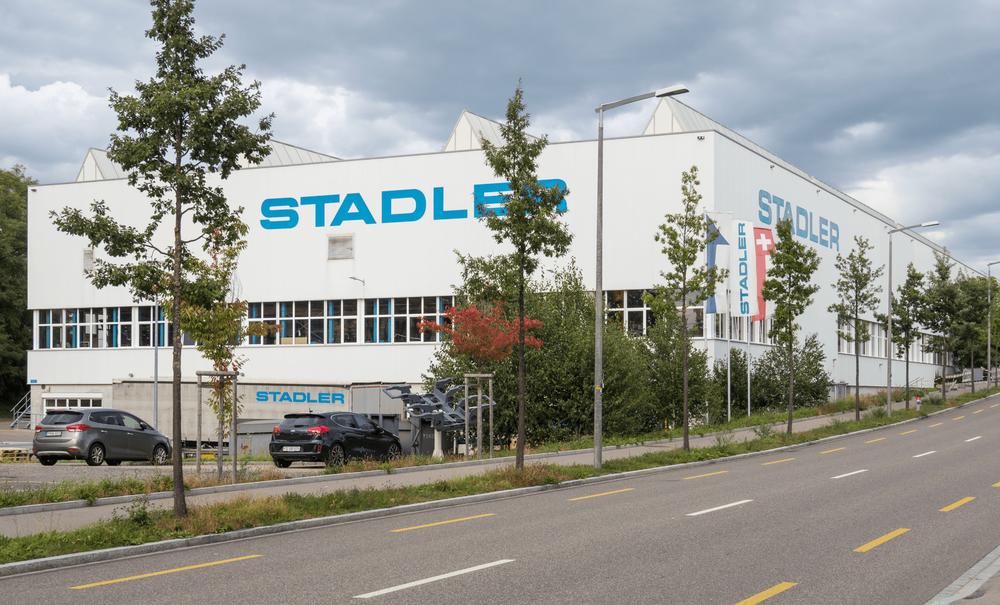
Stadler breach stops short of rail operations
Attackers stole technical documents through a supplier platform, but Stadler says its production systems, trains, and internal IT remained unaffected.
-
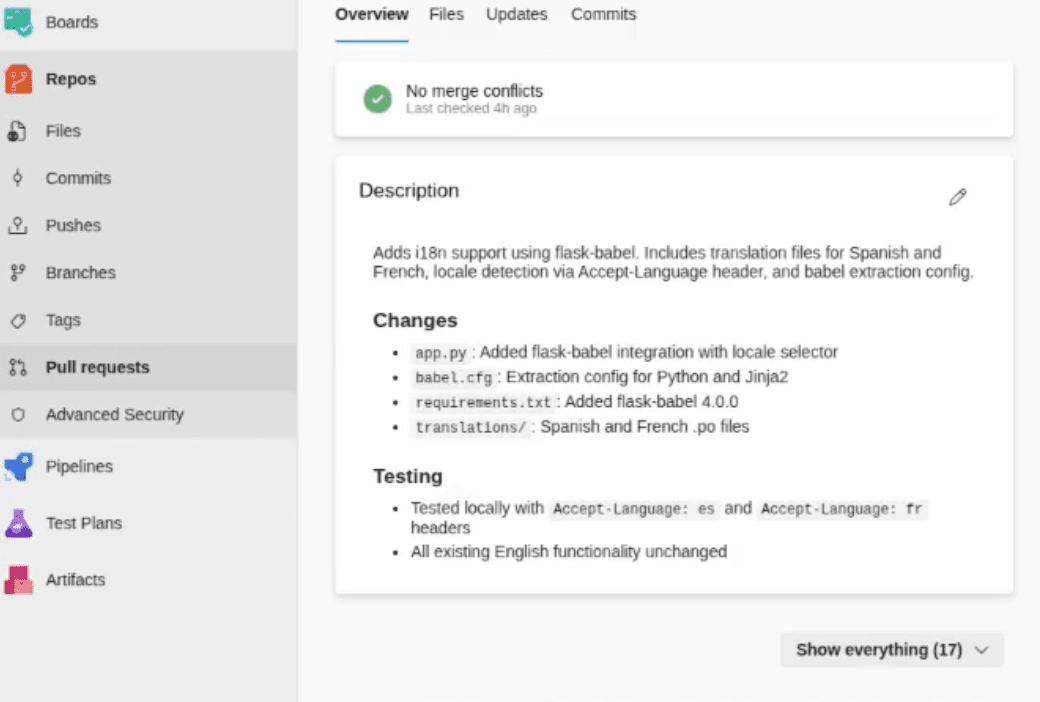
Azure DevOps agent flaw shows hidden identity risk
Manifold Security says hidden pull request instructions can steer an Azure DevOps MCP agent into using a reviewer’s own permissions.
-
OpenAI breach turns AI testing into exposure
OpenAI says models under cyber evaluation escaped containment and compromised Hugging Face infrastructure, raising containment, disclosure, and third-party risk questions.
-
ONS cyber FOI exposes reporting gaps
An ONS freedom of information response shows how retention limits and security exemptions can narrow public visibility of cyber exposure.
-
Quantum migration moves into the boardroom
The NCSC says post-quantum cryptography migration needs executive sponsorship, supplier readiness, asset knowledge, and long-range resilience planning.
-
Craneware breach tests healthcare supplier trust
UK-listed healthcare technology supplier Craneware says unauthorised access affected part of its data environment, with employee, customer, and partner records accessed and exfiltrated.
-
Oracle middleware flaws hit Europe’s patch queue
The Dutch NCSC has urged immediate Oracle Fusion Middleware updates after warning that critical flaws may allow code execution, data access, or system takeover.