
Risk & governance
-
ONS cyber FOI exposes reporting gaps
An ONS freedom of information response shows how retention limits and security exemptions can narrow public visibility of cyber exposure.
-
Quantum migration moves into the boardroom
The NCSC says post-quantum cryptography migration needs executive sponsorship, supplier readiness, asset knowledge, and long-range resilience planning.
-
Craneware breach tests healthcare supplier trust
UK-listed healthcare technology supplier Craneware says unauthorised access affected part of its data environment, with employee, customer, and partner records accessed and exfiltrated.
-
Oracle middleware flaws hit Europe’s patch queue
The Dutch NCSC has urged immediate Oracle Fusion Middleware updates after warning that critical flaws may allow code execution, data access, or system takeover.
-
Kratos takedown exposes the limits of MFA
German and US authorities have disrupted Kratos, a phishing-as-a-service kit used to steal Microsoft 365 credentials and session cookies.
-
Germany builds a federal cyber control layer
CyberGovSecure will centralise cyber governance across Germany’s federal administration, with workstreams covering configuration, vulnerability management, logging, detection, and mobile device control.
-
Hospitals get new EU cyber buying guide
ENISA’s first health action plan deliverable pushes hospital cybersecurity into procurement, supplier selection, contracts, and lifecycle management.
-
Four terabytes in an encrypted USB drive
Apricorn has launched a 4TB hardware-encrypted USB device for moving large sensitive datasets where network transfer is impractical, with FIPS 140-3 validation still in progress.
-
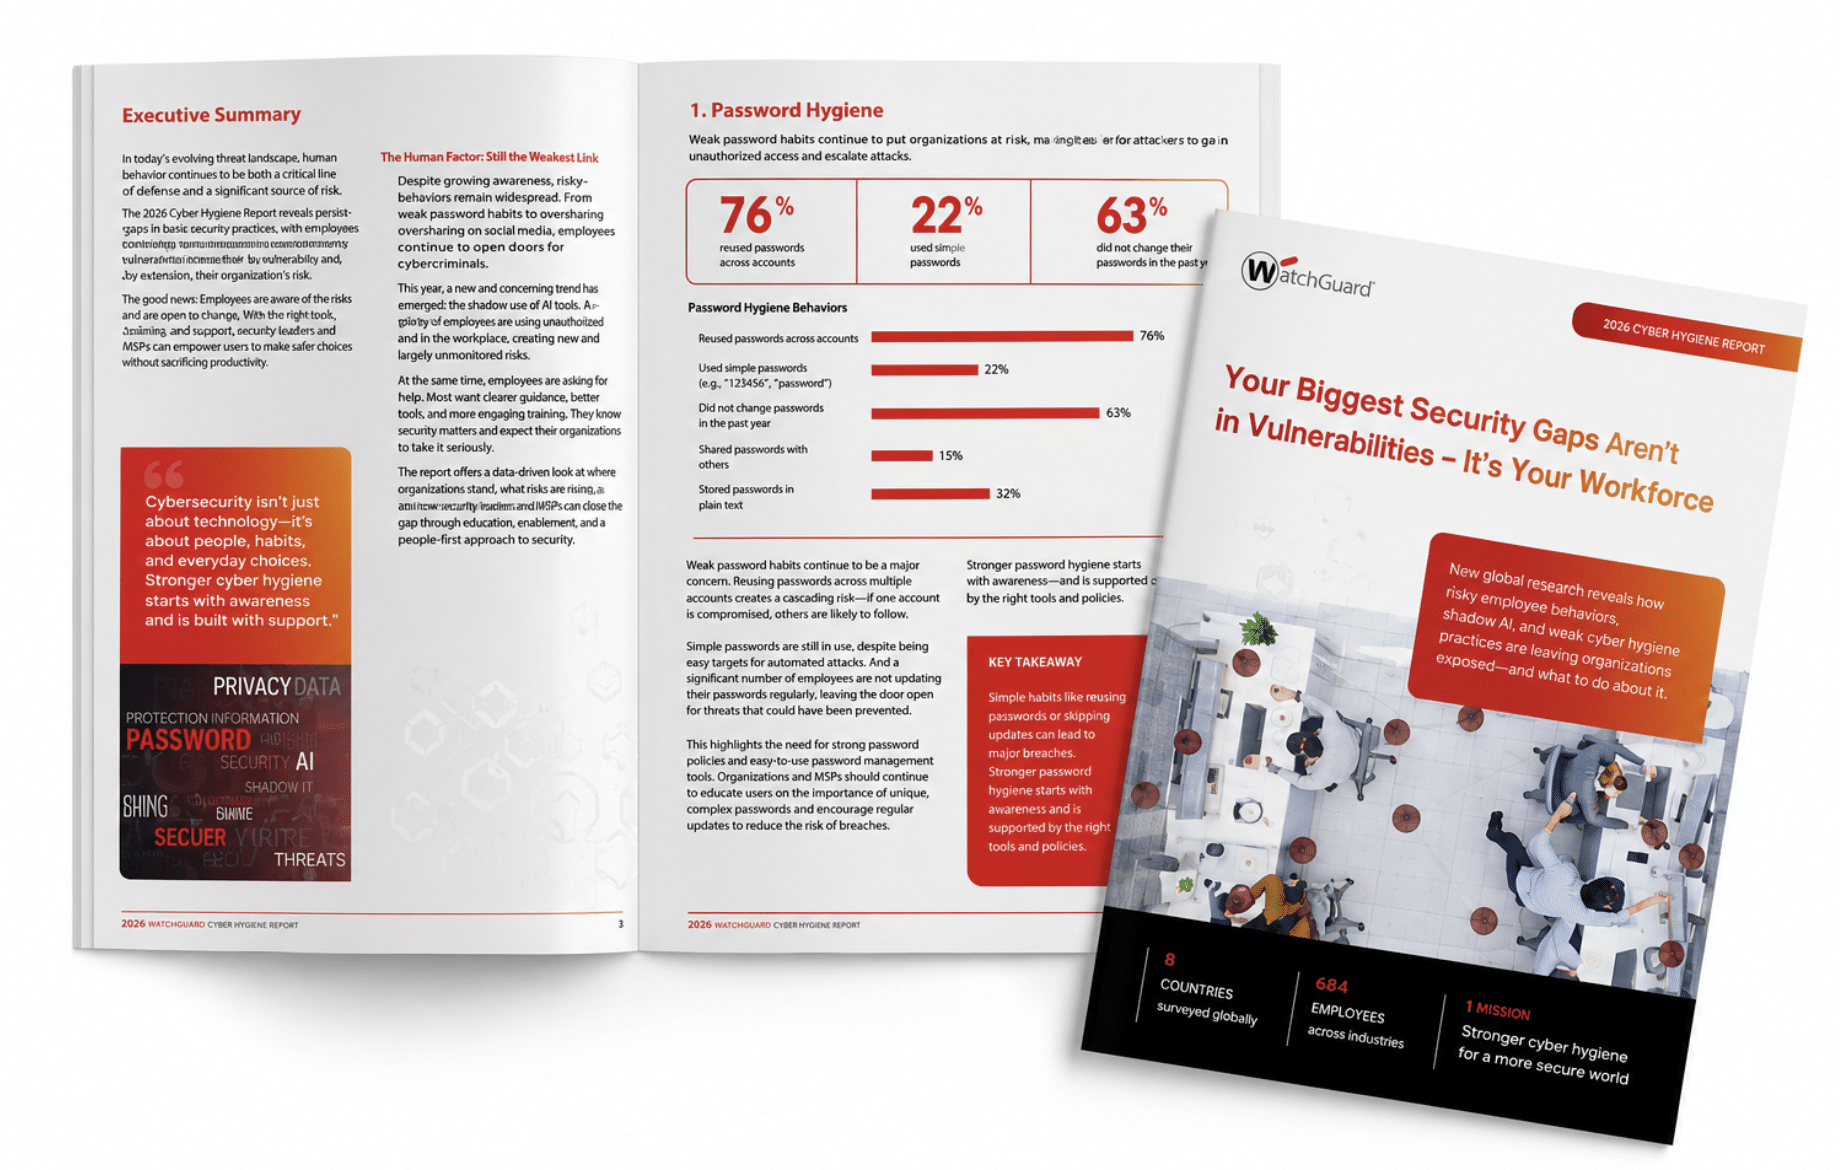
Shadow AI grows alongside basic security failures
WatchGuard research suggests unauthorised AI use is rising alongside password reuse, weak application visibility, and inconsistent remote-working controls across smaller and mid-market organisations.
-
Treasury report prices financial cyber disruption
HM Treasury research places cyber among the financial system’s leading risks and models extreme annual ransomware losses of hundreds of millions of pounds for larger organisations.