
Risk & governance
-
Palo Alto launches continuous AI testing
Palo Alto Networks is turning frontier-model offensive testing into a continuous subscription service spanning applications, APIs, cloud infrastructure, source repositories, and networks.
-
Gartner survey finds deepfakes in enterprise calls
A Gartner survey of 297 senior cybersecurity leaders found 41% had encountered at least one deepfake-related social-engineering incident involving an employee audio call during the previous year.
-
NCSC says AI currently favours attackers
The NCSC says offensive cyber tasks are easier to automate safely than defensive actions, where an incorrect autonomous change can disrupt the live business systems it was intended to protect.
-
EDPB standardises approach to GDPR fines
European data protection authorities have been given a common five-step methodology for deciding whether GDPR infringements should attract fines alongside other corrective measures.
-
Banks set principles for agentic commerce
NatWest, ING, and four other banks have proposed common principles for AI agents that shop and pay on customers’ behalf, focusing on transparency, security, privacy, choice, and interoperability.
-
European cyber teams face widening resource gap
ISACA research finds European cyber teams reporting rising attacks while more than half say they are understaffed and underfunded, adding operational strain as regulatory and technical demands continue to expand.
-
RNLI warns supporters after supplier breach
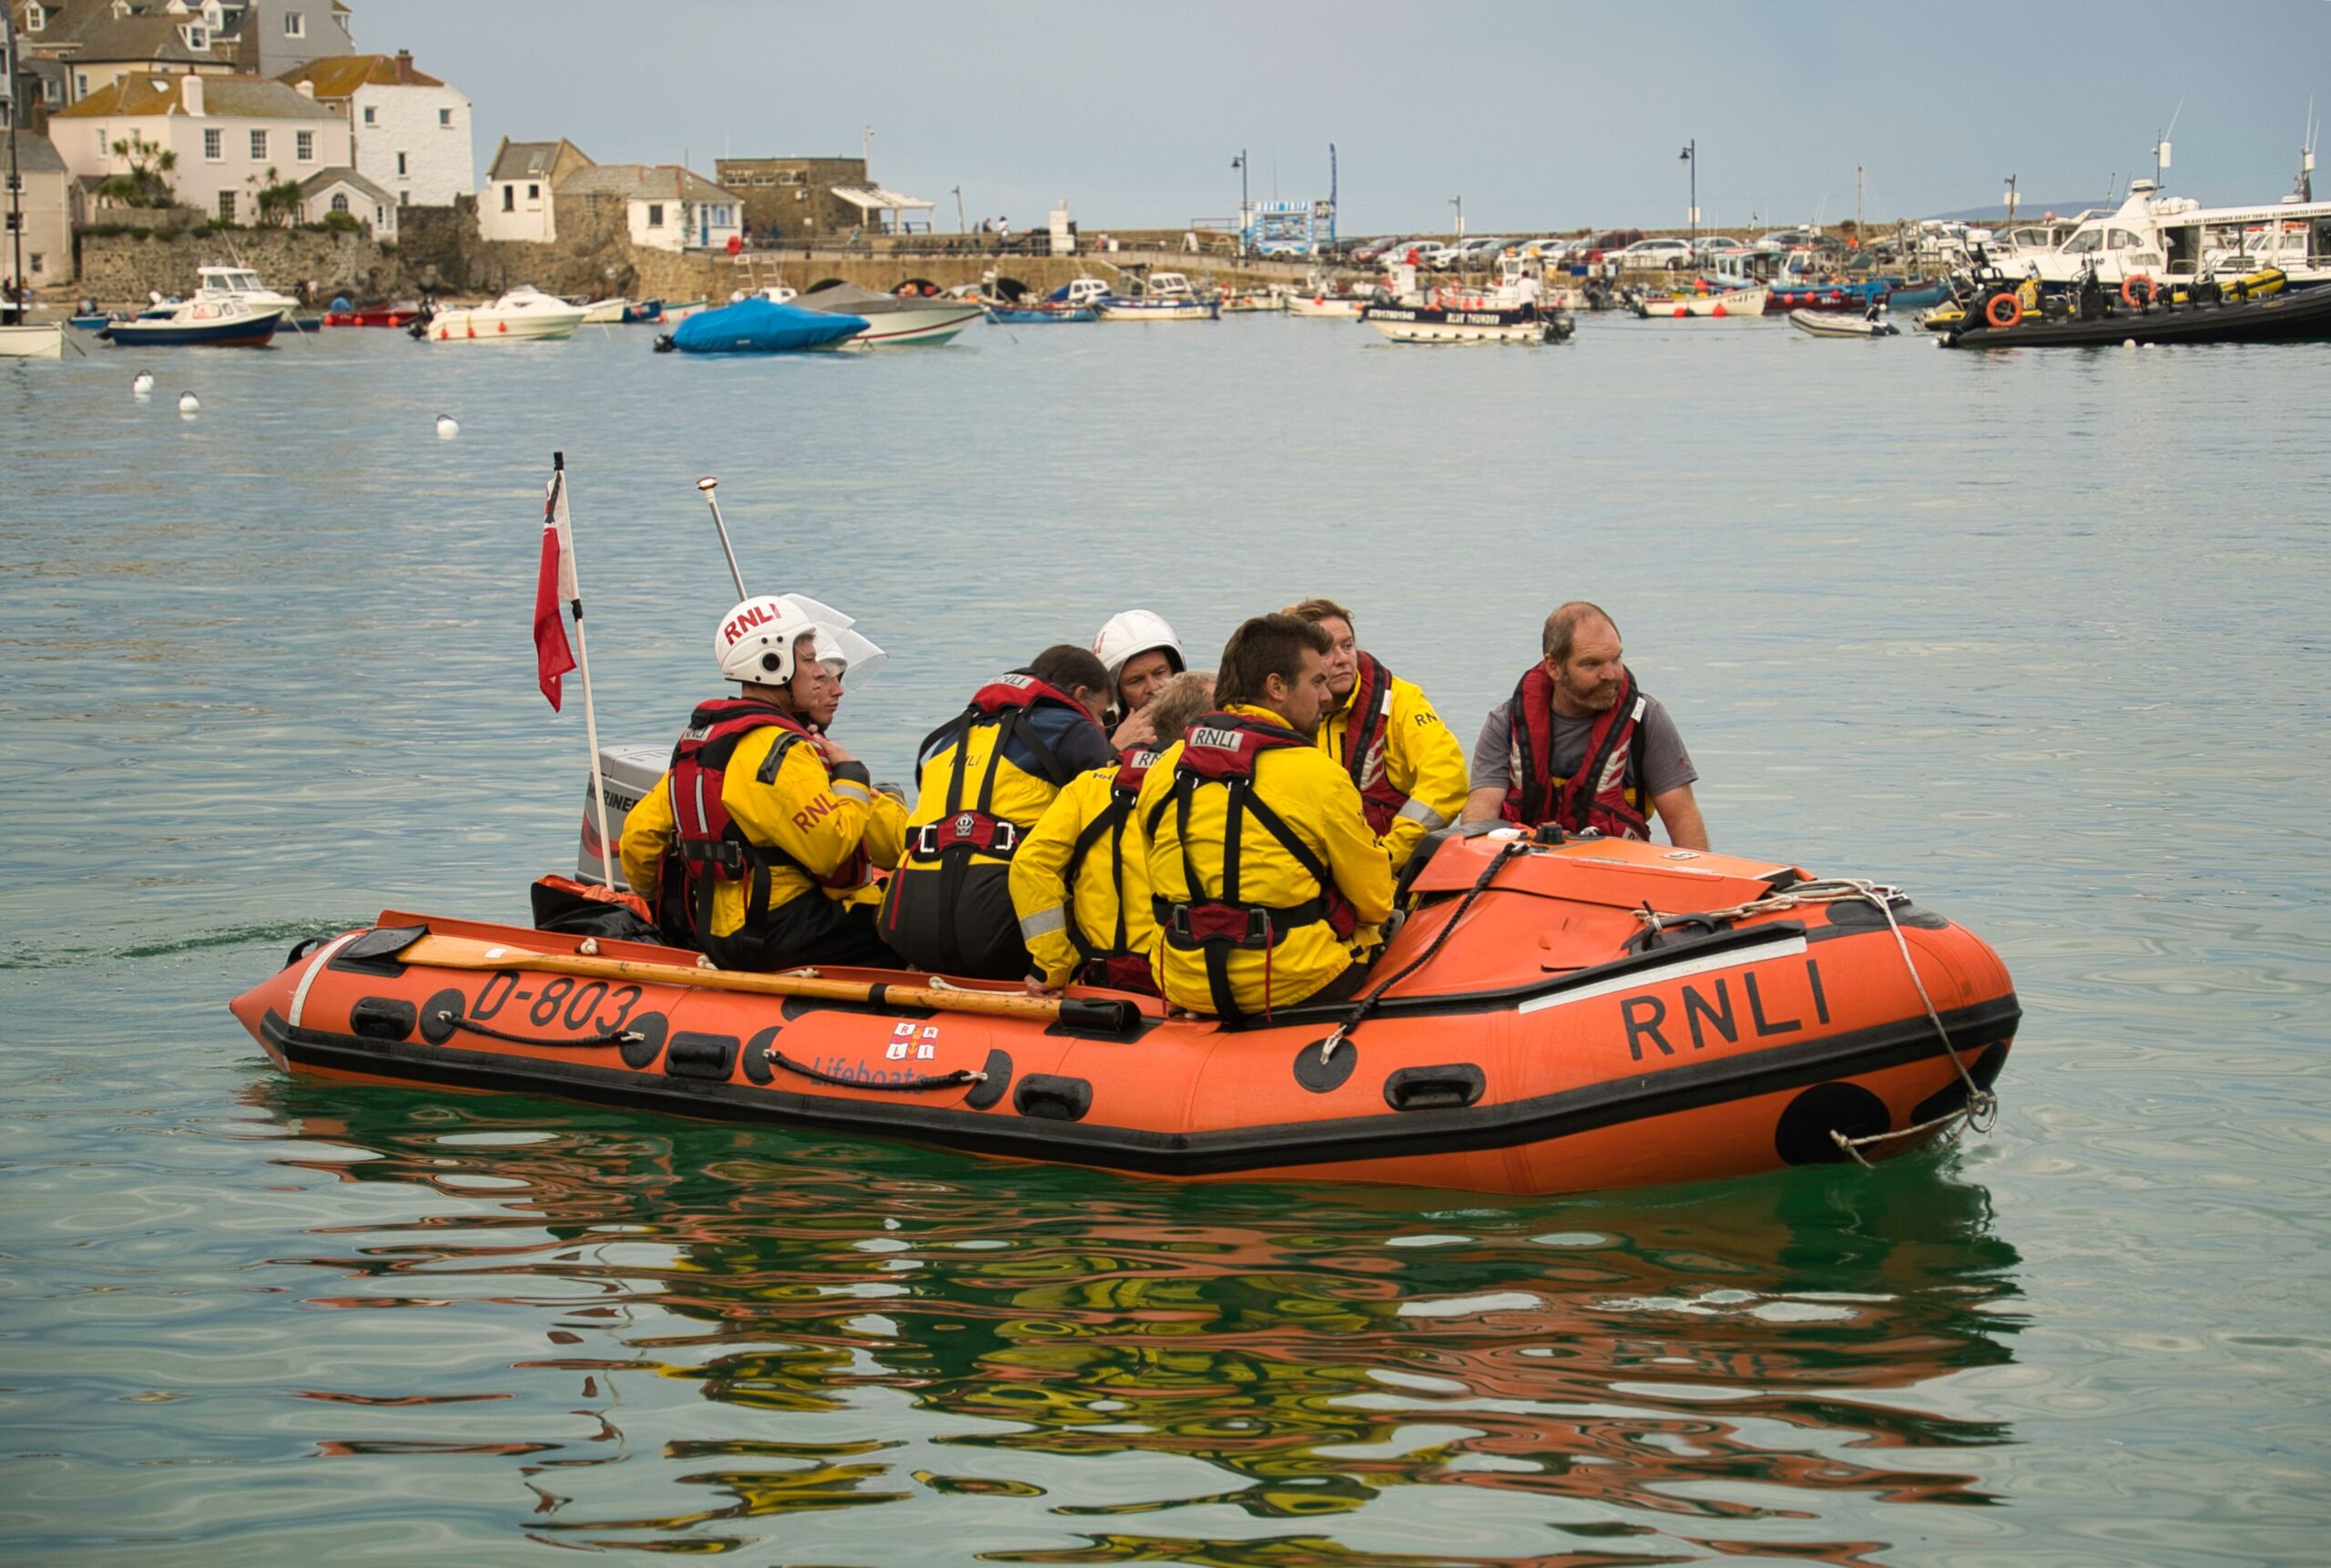
The RNLI has written to supporters warning that information held by Beacon CRM may have been taken during the supplier’s July cyber incident.
-
Craneware resets outlook after cyber incident
Craneware has reset FY27 revenue expectations to about $185 million while remediation, customer notification, and regulatory work continue after July’s data breach.
-

UK defence sets continuous software assurance model
UK defence has published a methodology for replacing static software approval evidence with continuous, traceable assurance based on the current state of systems.
-
Swiss cyber-unit inquiry leaves criminal questions open
A Swiss inquiry says earlier intelligence cyber-unit recommendations have largely been implemented, while unresolved questions about historic network-data sharing remain with federal prosecutors.