
Risk & governance
-
Dutch public bodies get threat-sharing mandate
The Dutch NCSC says STIX and TAXII 2.1 are now mandatory for government bodies, putting machine-readable threat intelligence into public-sector procurement and operations.
-
EDPB tightens AI scraping rules
The European Data Protection Board has adopted guidance on anonymisation, generative AI web scraping, and blockchain data processing, sharpening compliance expectations for data-intensive systems.
-
ENISA warns on frontier AI cyber pressure
ENISA says frontier AI could compress vulnerability and patch cycles, forcing European authorities, providers, and defenders to adapt cyber resilience to machine-speed threats.
-
ECB gives banks AI cyber deadline
Eurozone banks have until 31 October to submit AI cyber action plans, with supervisors tying frontier AI risk to DORA, patching, exposed assets, suppliers, and board accountability.
-
Ransomware groups target software supply chains
Sophos researchers say Vect and TeamPCP have linked supply chain credential theft with ransomware deployment, putting developer ecosystems in the extortion path.
-
MPs warn UK risks AI dependency
The Science, Innovation and Technology Committee says the UK lacks a coherent strategy for technology sovereignty as AI becomes central to global competition.
-
FCA warns AI could amplify cyber risk
The Mills Review says AI could reshape retail financial services by 2030 while increasing fraud, cyber security, consumer harm, and concentration risks.
-
France readies food sector for cyber crisis
ANSSI has published a cyber crisis exercise kit for the agri-food sector, pushing preparation beyond IT teams and into operational continuity planning.
-
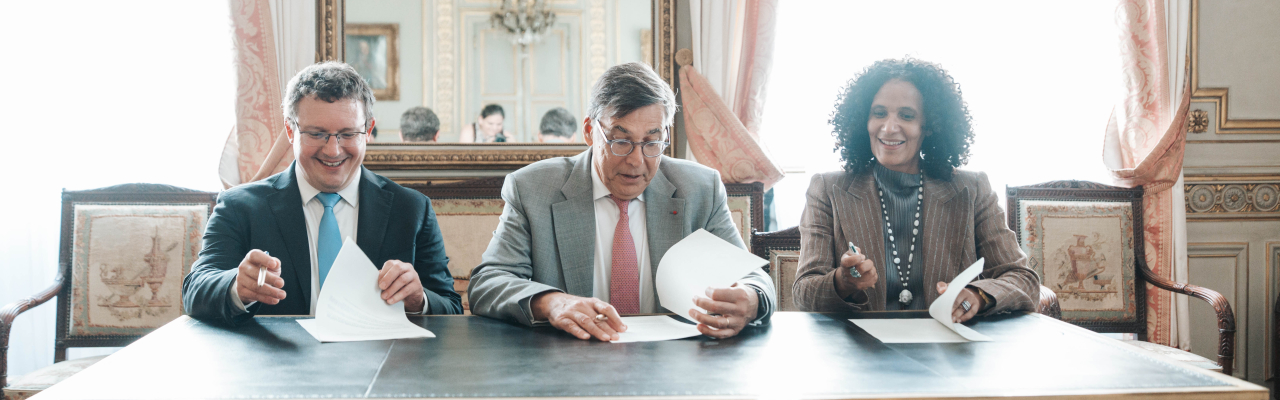
French regulators tighten finance cyber coordination
ANSSI, ACPR, and the Banque de France have signed a new agreement covering cyber incidents, crisis management, controls, and threat led penetration testing.
-
EU weighs AI cyber strategy
MEPs are pressing the Commission on AI and cybersecurity proposals as Brussels considers how NIS2, ENISA powers, certification, and ICT supply chain rules should evolve.