
Risk & governance
-
Cyber resilience Bill advances in Lords
The UK Cyber Security and Resilience Bill has reached Lords second reading, extending debate around essential services, suppliers, reporting, and resilience.
-
UK regulators begin cloud provider oversight
AWS, Google Cloud, Microsoft, and Oracle are the first critical third parties brought under direct UK financial-sector resilience oversight.
-
Lidl breach exposes supplier data risk
Lidl customer notices in Belgium and the Netherlands say attackers stole online shop customer data from a separately stored file at an IT service provider.
-
Odido breach probe turns to Dutch suspects
Dutch police say their investigation into the Odido breach has found indications of local involvement, including a Dutch-speaking caller posing as IT staff.
-
ENISA turns CRA readiness towards SMEs
ENISA has published a Cyber Resilience Act maturity model for smaller organisations that manufacture, integrate, or support products with digital elements.
-
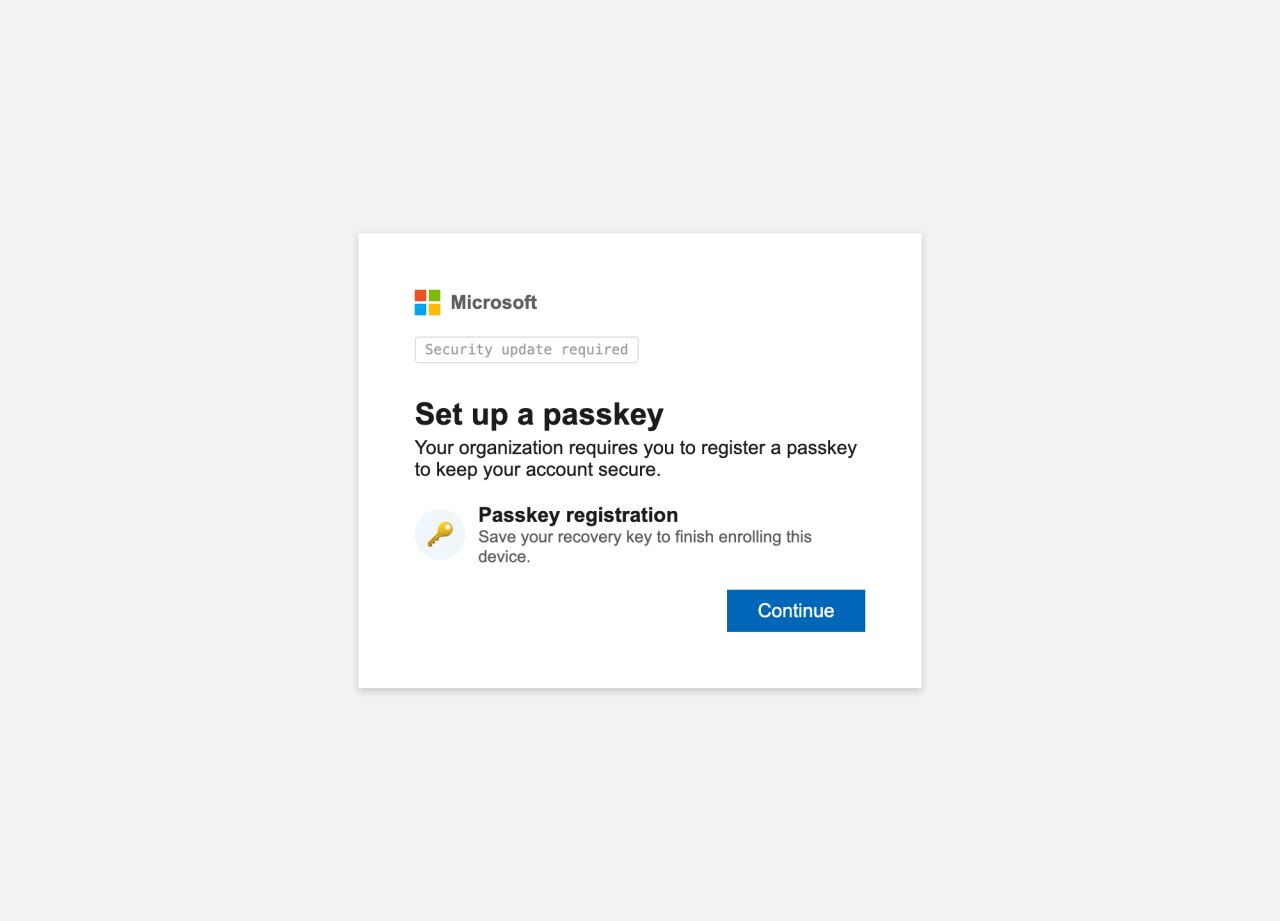
Passkey vishing targets Entra users
Okta says vishing actors are using fake Microsoft Entra passkey enrolment flows, showing how attackers are adapting to passwordless authentication.
-
Databarracks expands resilience services
Databarracks’ acquisition of Acumen extends its business continuity capabilities as cyber recovery, crisis planning, and operational resilience continue to converge.
-
NCSC opens Cyber Essentials Pathways
The NCSC is widening Cyber Essentials Pathways, giving complex organisations a managed route to show equivalent security outcomes without weakening certification trust.
-
Microsoft pushes faster Windows patching
Microsoft says AI will increase the pace and volume of Windows security updates, forcing organisations to revisit patch windows, deferrals, and change risk.
-
Dialogflow flaw exposes AI isolation risk
A patched Dialogflow CX flaw shows how AI chatbot infrastructure can turn a single agent permission into conversation exposure and cross-agent risk.