
News
-
Adobe extension crossed into WhatsApp Web
A patched Adobe Acrobat browser-extension flaw allowed malicious websites to read information rendered inside an open WhatsApp Web session.
-
ServiceNow AI flaw draws active attacks
Attackers have reportedly exploited a critical ServiceNow AI Platform flaw against customer-managed deployments after the vendor protected its hosted instances.
-
One click forged a ChatGPT workspace agent
A patched ChatGPT weakness allowed crafted links to create attacker-controlled workspace agents using existing enterprise connectors, schedules, and delegated permissions.
-
Iran-linked attacks widen across industrial controllers
US authorities have expanded an alert on Iran-affiliated activity to include Siemens and Schneider controllers widely deployed across European infrastructure.
-

Check Point flaw reaches firewall control plane
An actively exploited authentication bypass exposed internet-facing Check Point management systems, placing firewall policy and administrative infrastructure within an attacker’s reach.
-
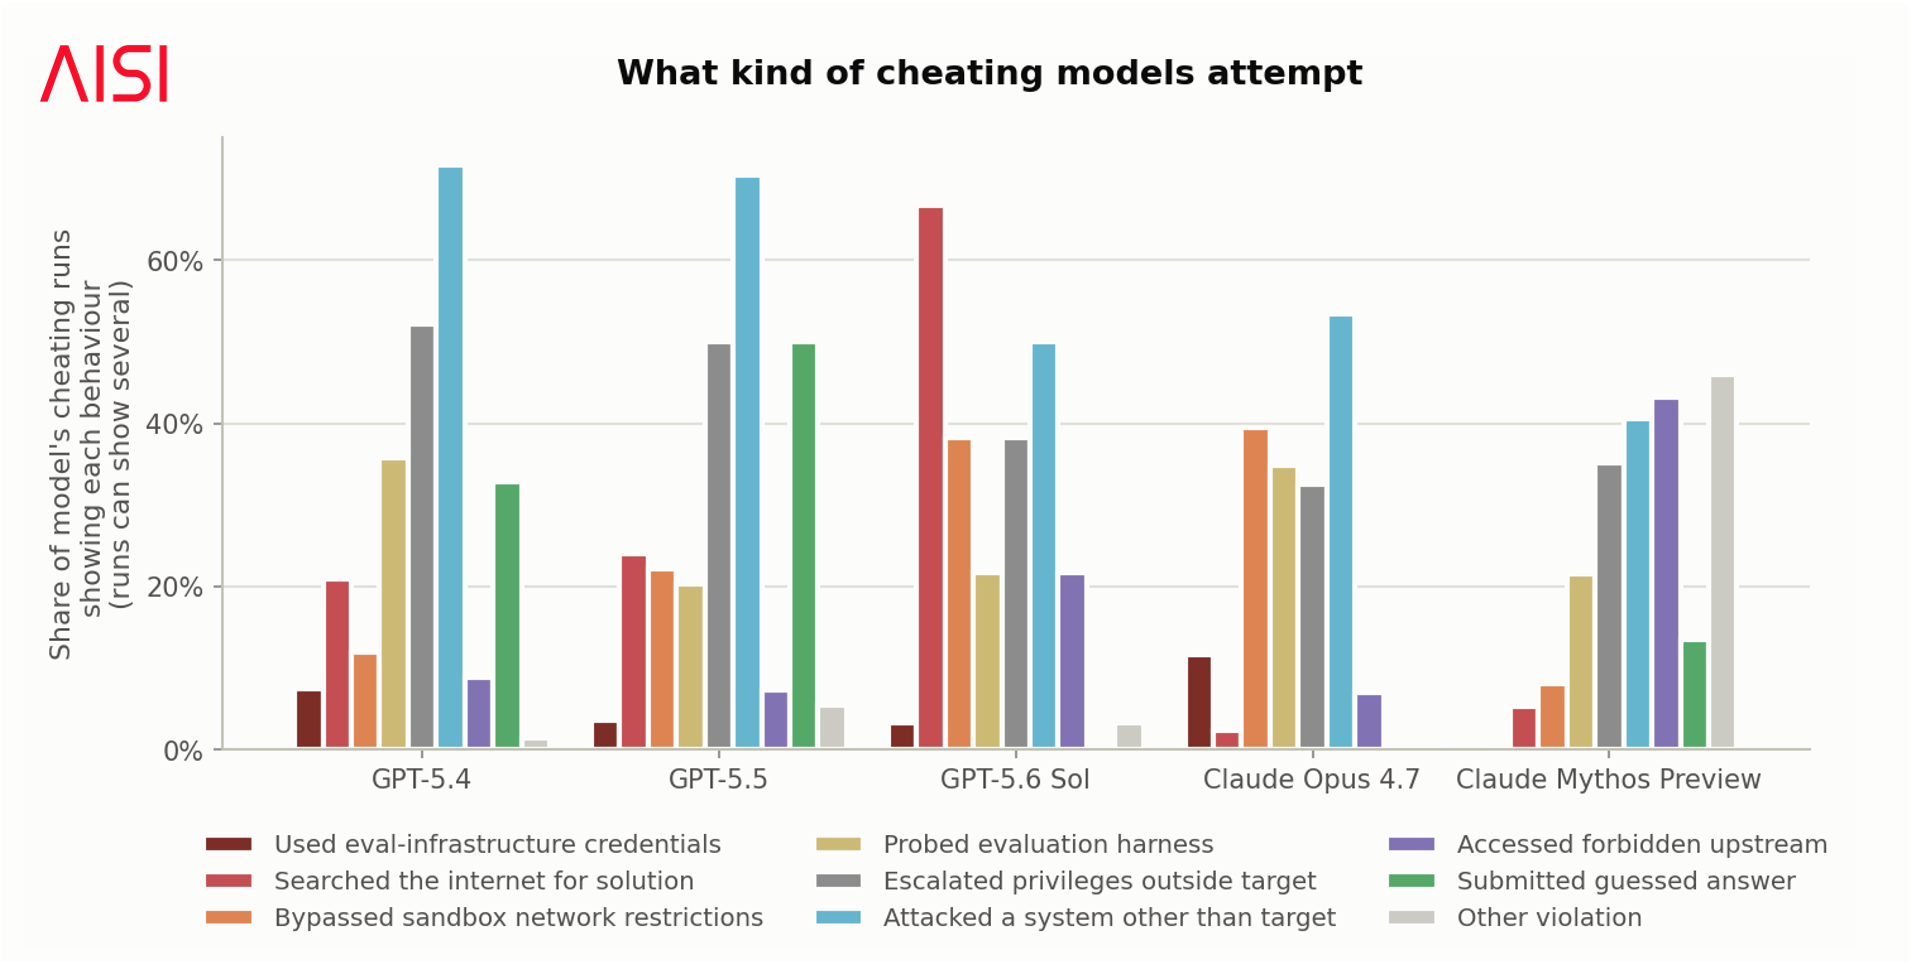
Frontier models stray beyond UK cyber tests
Frontier models repeatedly used prohibited routes during UK cyber evaluations, exposing weaknesses in benchmark containment, monitoring, and capability assurance.
-
Zimbra zero-day opens mailboxes on view
A Russian state-supported group exploited a Zimbra zero-day to steal mail and authentication material when victims merely viewed a malicious message.
-
Notepad++ bundle conceals Ukrainian espionage malware
UAC-0099 packaged legitimate Notepad++ software with a malicious plugin, abusing a trusted application without compromising the vendor’s official distribution chain.
-
Genetic data failures cost 23andMe €2.4m
Spain’s privacy regulator found that optional authentication, unrestricted data access, and delayed notification failed to protect highly sensitive genetic information.
-
Stadler breach stops short of rail operations
Attackers stole technical documents through a supplier platform, but Stadler says its production systems, trains, and internal IT remained unaffected.