
News
-
Malicious models threaten Rockwell simulation users
Four memory-corruption flaws in Arena Simulation can execute code when a user opens a malicious file, placing trusted engineering exchanges under scrutiny.
-

Hostile hotel Wi-Fi reroutes Microsoft logins
Attackers are compromising hospitality gateways and poisoning DNS responses to redirect connected users towards counterfeit Microsoft 365 authentication pages.
-
Azure Automation flaw crossed tenant boundary
Microsoft researchers chained an exposed service configuration with two Azure Automation flaws to assume an identity belonging to another cloud tenant.
-
Automation error takes Azure routes offline
A Microsoft maintenance-system defect removed more network routes than intended, disrupting Azure services and testing cloud-resilience arrangements across dependent organisations.
-

Europe accounts for 31% of exposed ICS
Censys has counted about 138,000 internet-exposed industrial hosts, with Europe representing 31.1%, while publicly reachable AI infrastructure continues to expand.
-
UK cyber brief survives Whitehall restructure
Baroness Liz Lloyd has received joint appointments across two reorganised departments, preserving ministerial continuity as the UK expands cyber regulation and infrastructure oversight.
-
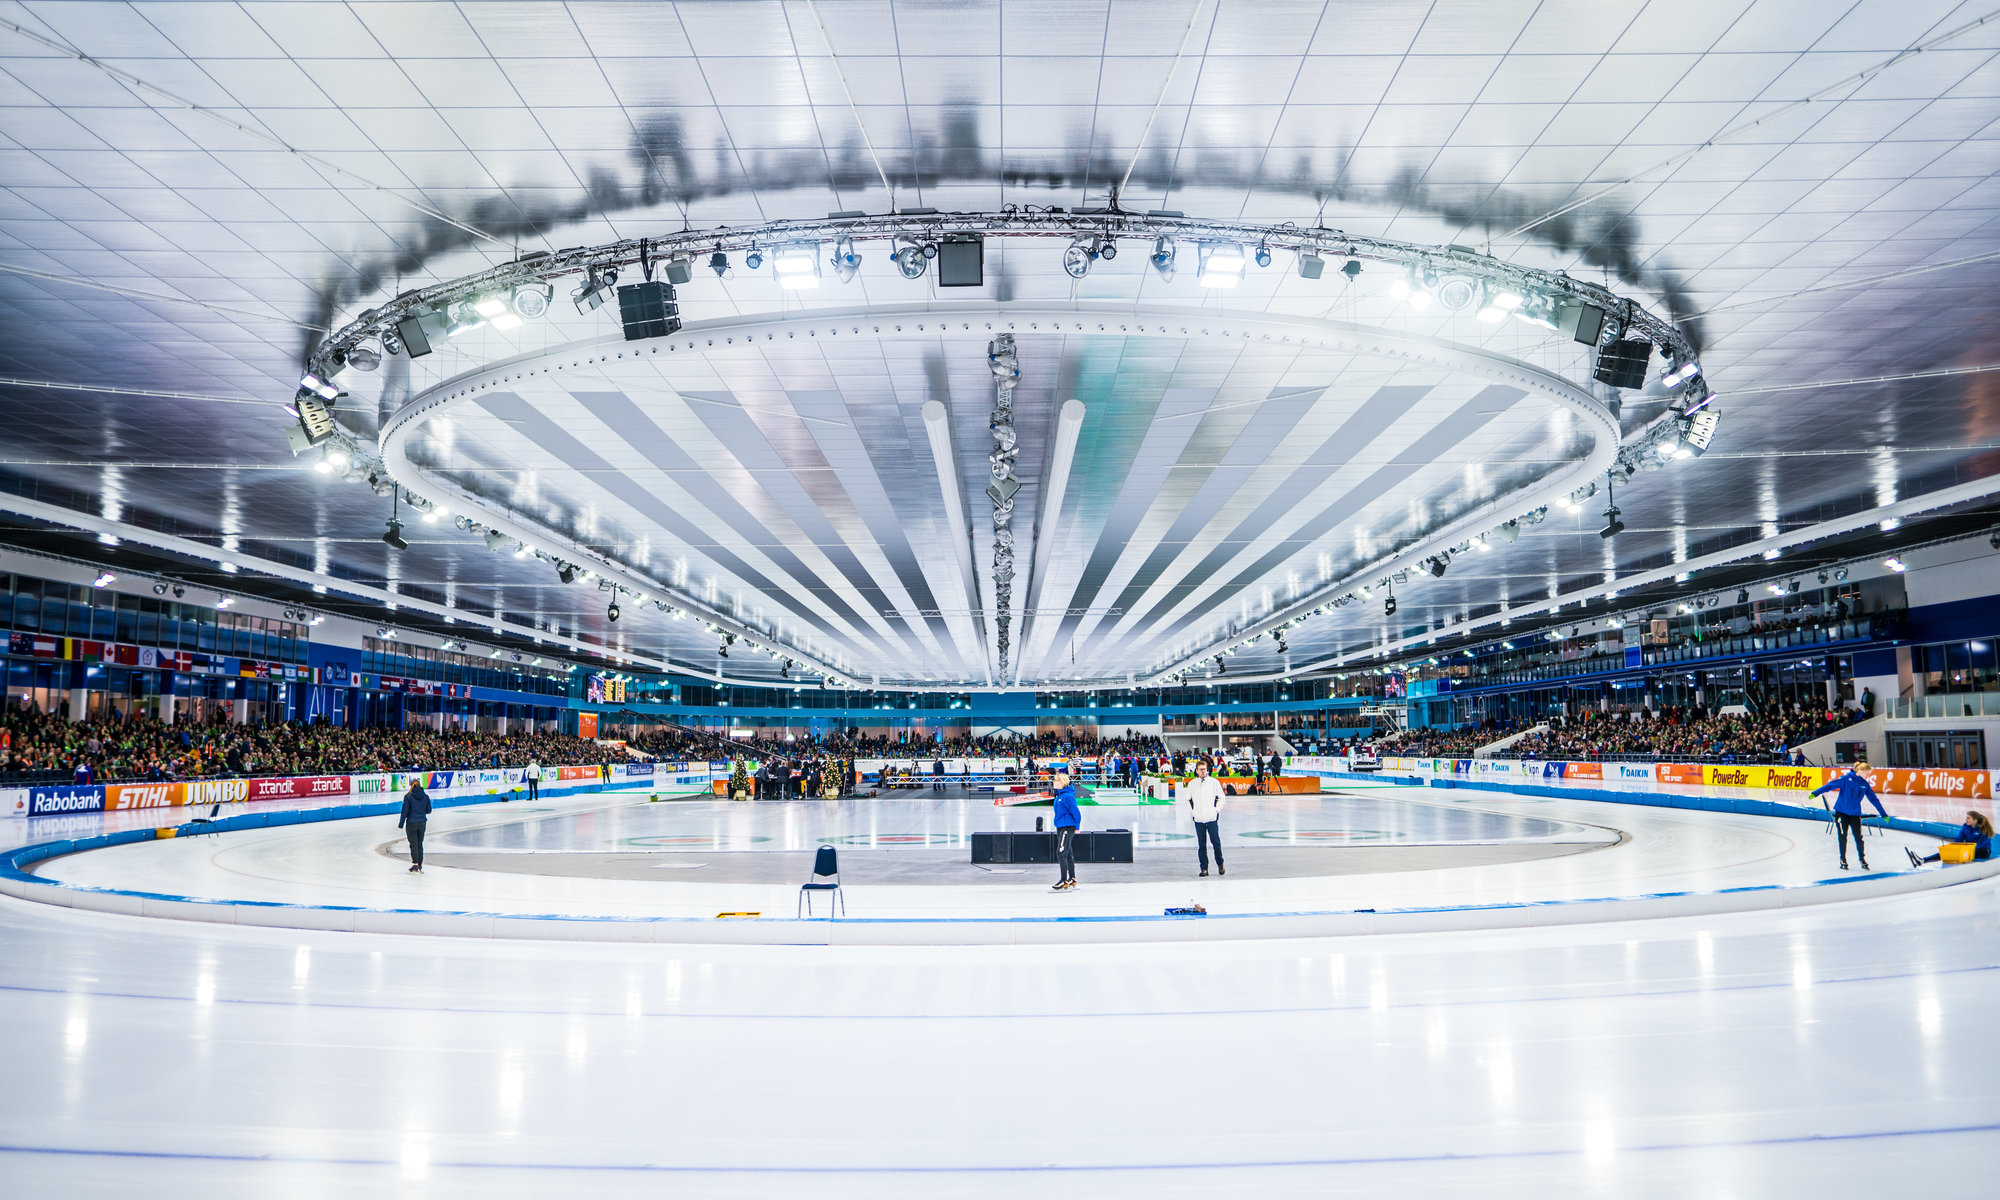
Thialf disputes ransomware claims after cyberattack
The Dutch arena has confirmed a cyberattack but says neither its data nor its operations were affected, contradicting separate claims of theft and extortion.
-
Root access chain reaches Siemens industrial switches
Three vulnerabilities affecting Siemens RUGGEDCOM ROX II switches can be chained to expose sensitive files, obtain root privileges, and establish persistence across a reboot.
-
TeamViewer disclosure delay draws €240,000 fine
Germany’s financial regulator has fined TeamViewer after finding that its 2024 cyberattack should have been disclosed to the market without delay.
-
Europe sets assurance baseline for cyber providers
ENISA’s proposed certification scheme would establish common assurance requirements for managed security services, beginning with incident response and providers supporting the EU Cybersecurity Reserve.