Summary
- Revolut says a very limited number of customers were affected after fraudulent requests arrived through a legitimate government-agency email domain.
- The company says its systems and customer funds were unaffected and affected customers have been notified.
- The incident exposes the authentication problem inside processes used to respond to apparently lawful demands for sensitive customer information.
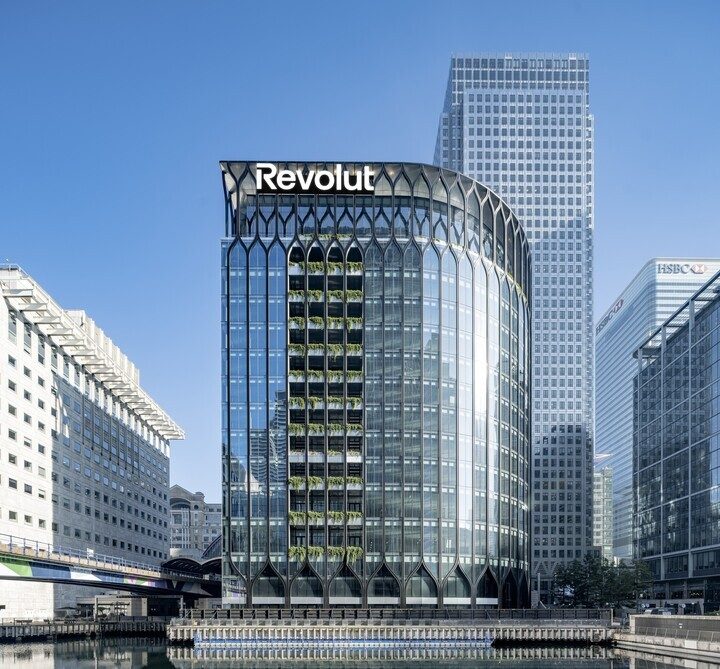
Revolut has disclosed sensitive customer information to an unauthorised party after fraudulent requests arrived through an email domain associated with a legitimate government agency, exposing a security weakness inside trusted information-disclosure processes rather than the company’s core banking systems.
The London-headquartered financial company said the number of affected customers was very limited and that those individuals had been notified. It has not publicly disclosed a precise figure.
Revolut said its systems and customer funds were unaffected. After detecting the fraudulent requests, it blocked the address involved and alerted the relevant government agency, law-enforcement bodies, data-protection authorities, and financial regulators.
Reuters reported, citing TechCrunch, that the information disclosed included dates of birth, postal and email addresses, telephone numbers, and copies of identity documents including passports and driving licences. Revolut has not publicly provided a complete inventory of the affected data in its own statement.
The attack path distinguishes the incident from a conventional breach in which an attacker compromises an account or exploits a technical vulnerability to enter a company’s systems. In this case, the apparent route to the information was a business process designed to release data when a sufficiently authoritative request is received.
Banks and other financial institutions routinely handle demands from law enforcement, courts, regulators, and government agencies. Those requests can carry legal deadlines and may involve sensitive investigations, which creates pressure for a process that is both efficient and difficult to impersonate.
Email identity is a weak foundation for that decision on its own. A message can originate from infrastructure associated with a legitimate organisation while the individual request remains fraudulent, unauthorised, or sent through a compromised account.
The control problem therefore extends beyond verifying the visible sender domain. Organisations handling sensitive disclosures need confidence in the requesting authority, the individual making the request, its legal basis, the scope of information sought, and the channel through which the data is eventually returned.
That shifts part of the security boundary away from system access and towards authorisation of an otherwise legitimate workflow. Strong controls around databases do not prevent information leaving when an authorised employee is persuaded that disclosure has been properly requested.
The consequences can also persist after the immediate incident is contained. Passwords can be reset and cards replaced, but copies of passports, driving licences, dates of birth, addresses, and other identity information can remain useful for impersonation and fraud for much longer.
Revolut’s regulatory position adds another layer of scrutiny. Revolut Bank UK became a fully licensed UK bank earlier in 2026 and is regulated by the Prudential Regulation Authority and Financial Conduct Authority. The company also notified data-protection and financial regulators after discovering the disclosure.
The eventual scale of the incident remains unclear because the exact number of customers and complete data set have not been made public. There is also no evidence in the available disclosure that Revolut’s underlying systems were penetrated.
The confirmed failure is more specific: a fraudulent request was able to move sensitive customer information through a process intended for legitimate institutional access. That makes the integrity of the request itself as important as the technical security of the system holding the data.