Summary
- JAL and Japan Transocean Air were notified by Amadeus about external access to passenger-service records.
- About 90,000 records contained basic booking information; about 2,000 also contained more detailed identifiers.
- The airline reports no exposure of credit-card numbers or passwords and no disruption to flights.
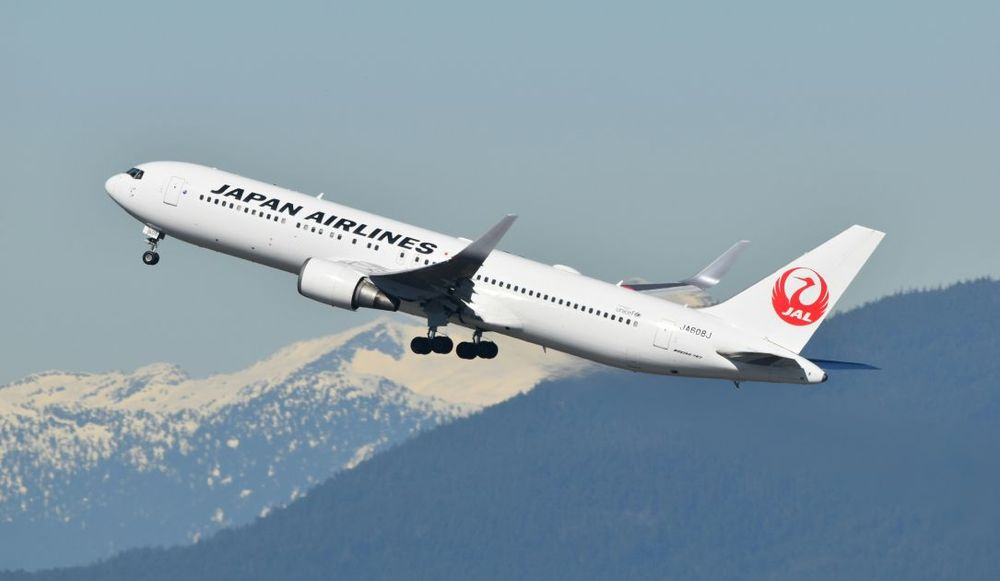
Japan Airlines has disclosed that traces of unauthorised external access to passenger reservation information were found in a system provided by Spanish travel technology company Amadeus. The airline and Japan Transocean Air were notified on 23 October, and the company estimates that information relating to approximately 92,000 customers was affected. It says the incident has not disrupted flight operations and that credit-card numbers and passwords were not compromised.
The affected service is a passenger service system used for flight reservations, ticketing and check-in. That makes it part of an airline’s operational data infrastructure even where the technology is provided by an external specialist. The company reports evidence of external access associated with a period extending from 10 August 2023 to 23 September 2026. That range describes the identified access traces and should not automatically be treated as proof that attackers continuously controlled the platform for the entire period.
Japan Airlines divides the affected customers into two groups. About 90,000 had reservation codes, names, flight dates, routes and service classes potentially accessed. A further approximately 2,000 had those fields alongside additional information that could include email addresses, telephone numbers, passport numbers, nationality, frequent-flyer numbers, airline and flight identifiers, ticket numbers and seat details.
Basic booking information can still have security value. A reservation reference and itinerary may help someone construct a convincing message claiming to concern a flight change, payment request or booking issue. The smaller group with passport and contact information faces a more detailed exposure profile, although the airline’s disclosure does not establish that every additional field was present for all 2,000 affected people or that criminal misuse has followed.
Reservation data has a distinct security character from payment-card information. A person with a booking reference, date, flight route and traveller name may be able to make a fraudulent communication appear relevant even without knowing a bank-card number. Conversely, the disclosure does not show that an attacker can modify a reservation or enter a passenger’s airline account. Those activities depend on separate authentication and application controls. The airline’s statement identifies records apparently accessed, while the evidence required to prove subsequent misuse would involve different systems and observations.
Investigators found traces spanning more than three years, but Japan Airlines has not stated that attackers continuously controlled the affected system throughout that period. The airline does not describe how much activity occurred at different points in the interval. A discovery made in 2026 may relate to historical access that was not recognised immediately, or to a series of accesses that became visible through later investigation. Japan Airlines has given a range associated with detected access traces, not a definitive start date for a continuously operating intruder. As the Spanish supplier supports multiple international carriers, any broader scope requires confirmation from Amadeus or other affected organisations rather than extrapolation from JAL’s customer count.
Amadeus provides infrastructure to airlines and other travel businesses across international markets, so the incident raises questions about supplier access and the separation of customer records within shared technology. The disclosure concerns the systems and customer records identified by Japan Airlines; it does not establish a breach affecting every airline using Amadeus. According to JAL, Amadeus has completed the necessary security measures, but neither the access mechanism nor the full set of affected supplier systems is established in the airline’s statement.
JAL plans to contact affected customers individually and has established a dedicated enquiry route. It also warns of phishing emails, fraudulent calls and counterfeit websites claiming to represent the group. The confirmed European dimension is a third-party reservation-system compromise involving a Spain-headquartered supplier. Any additional obligations for other operators depend on whether their data was actually affected, which has not been established by this customer disclosure.