Summary
- Italian parliamentary email systems were targeted, including an address assigned to Giorgia Meloni as an MP.
- The targeted parliamentary address is separate from the prime minister’s government communications.
- Authorities reported protective measures but did not confirm mailbox access or data theft.
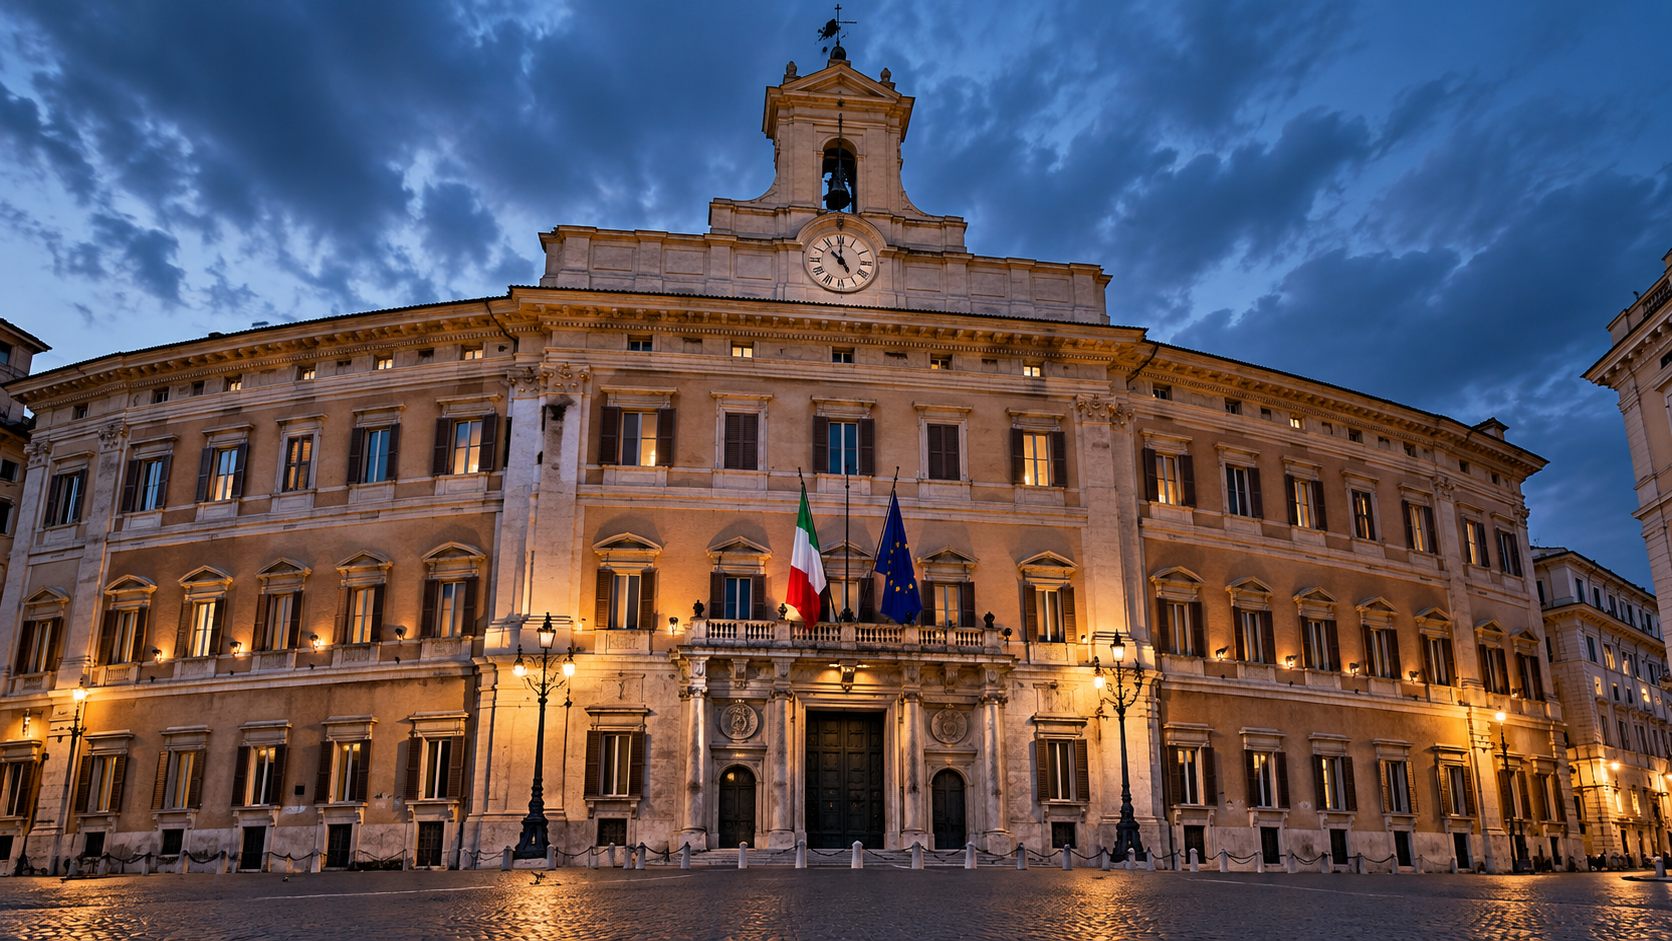
Italy’s Chamber of Deputies has reported cyberattacks targeting parliamentary IT and email systems, including an address assigned to Prime Minister Giorgia Meloni in her capacity as a member of parliament. Officials have not confirmed that an attacker accessed her mailbox, read correspondence or extracted data.
The disclosure on 27 October followed several days of increased pressure on the lower house’s digital infrastructure. Parliamentary sources told Italian news agency ANSA that technical staff had the situation under control and that protective measures were in place through cooperation with Italy’s National Cybersecurity Agency (ACN). Chamber sources characterised the activity as a recurring security problem rather than a declared emergency.
Meloni’s office separately clarified that the parliamentary address was not used for government communications. That distinction limits what can reasonably be inferred about the exposure of government business. The fact that an account was targeted does not prove successful authentication, mailbox access, or the theft of correspondence. Nor does the public account establish how many parliamentary users were affected.
Parliament as a target
National legislatures operate complex communications environments that link elected members, their staff, parliamentary administrations, committees and external correspondents. A mailbox is not simply a store of messages: compromise could allow an attacker to impersonate an office, obtain documents, follow conversations or send apparently authentic requests to colleagues. Those outcomes are possible attack consequences, not confirmed findings in the Italian incident.
Parliamentary email also sits at the boundary between several security domains. Members use official accounts for legislative work, but some handle party business or maintain separate executive-government arrangements. Separating the relevant accounts therefore matters when assessing an incident’s possible effect on parliamentary operations and on ministerial communications.
Accounts belonging to senior public figures are particularly attractive to attackers because messages appearing to come from them may carry additional credibility. Yet indiscriminate attempts against an organisation’s mail infrastructure can look similar to targeted attacks before forensic analysis establishes which accounts were actually reached and what authentication attempts succeeded.
The Chamber’s reported response included coordinated defensive measures with ACN under an existing protocol. Italian reporting also raised the possibility of temporarily disabling some functions where necessary. Such restrictions can reduce exposure while technical teams inspect account activity, although the authorities have not specified which functions, if any, were disabled during this response.
Questions the public account leaves open
There is no verified public figure for successful account compromises, no identified attack group, and no confirmed method of entry. That rules out describing the episode as an established data breach. It also prevents reliable attribution to a foreign government, criminal organisation or particular cyber campaign, even if the broader political environment makes such explanations tempting.
Investigators would ordinarily distinguish between attempted sign-ins, mailbox rules changed by an intruder, authenticated sessions and evidence that messages were read or exported. The public statements available on 27 October do not establish those stages. Attack volume is another separate measure: high traffic or repeated attempts against an institution does not necessarily mean an attacker gained a foothold.
The institution said similar attempts and pressure on IT systems had recently intensified against other Italian, European and international organisations. That description offers context for the defensive posture, but it does not substantiate a coordinated operation against all those bodies or a shared attacker.
National legislatures must also weigh disclosure against ongoing investigations. Revealing specific controls or account details may give adversaries useful information, whereas limited initial reporting can leave the public unsure how far an incident progressed. Both constraints are visible in the Chamber’s cautious statements.
By 27 October, the Chamber had described heightened attacks and defensive coordination with ACN. It had released no evidence of successful access to Meloni’s parliamentary inbox, the contents of other lawmakers’ messages or a common attacker behind the reported activity.