Summary
- Quantum Systems identified malicious activity involving its QBase update infrastructure.
- The Bundeswehr reportedly grounded affected drones as a precaution.
- The manufacturer says its fleet remains operational and denies risk to end users.
Germany’s armed forces reportedly grounded Quantum Systems drones after malicious activity affected the manufacturer’s QBase software update infrastructure.
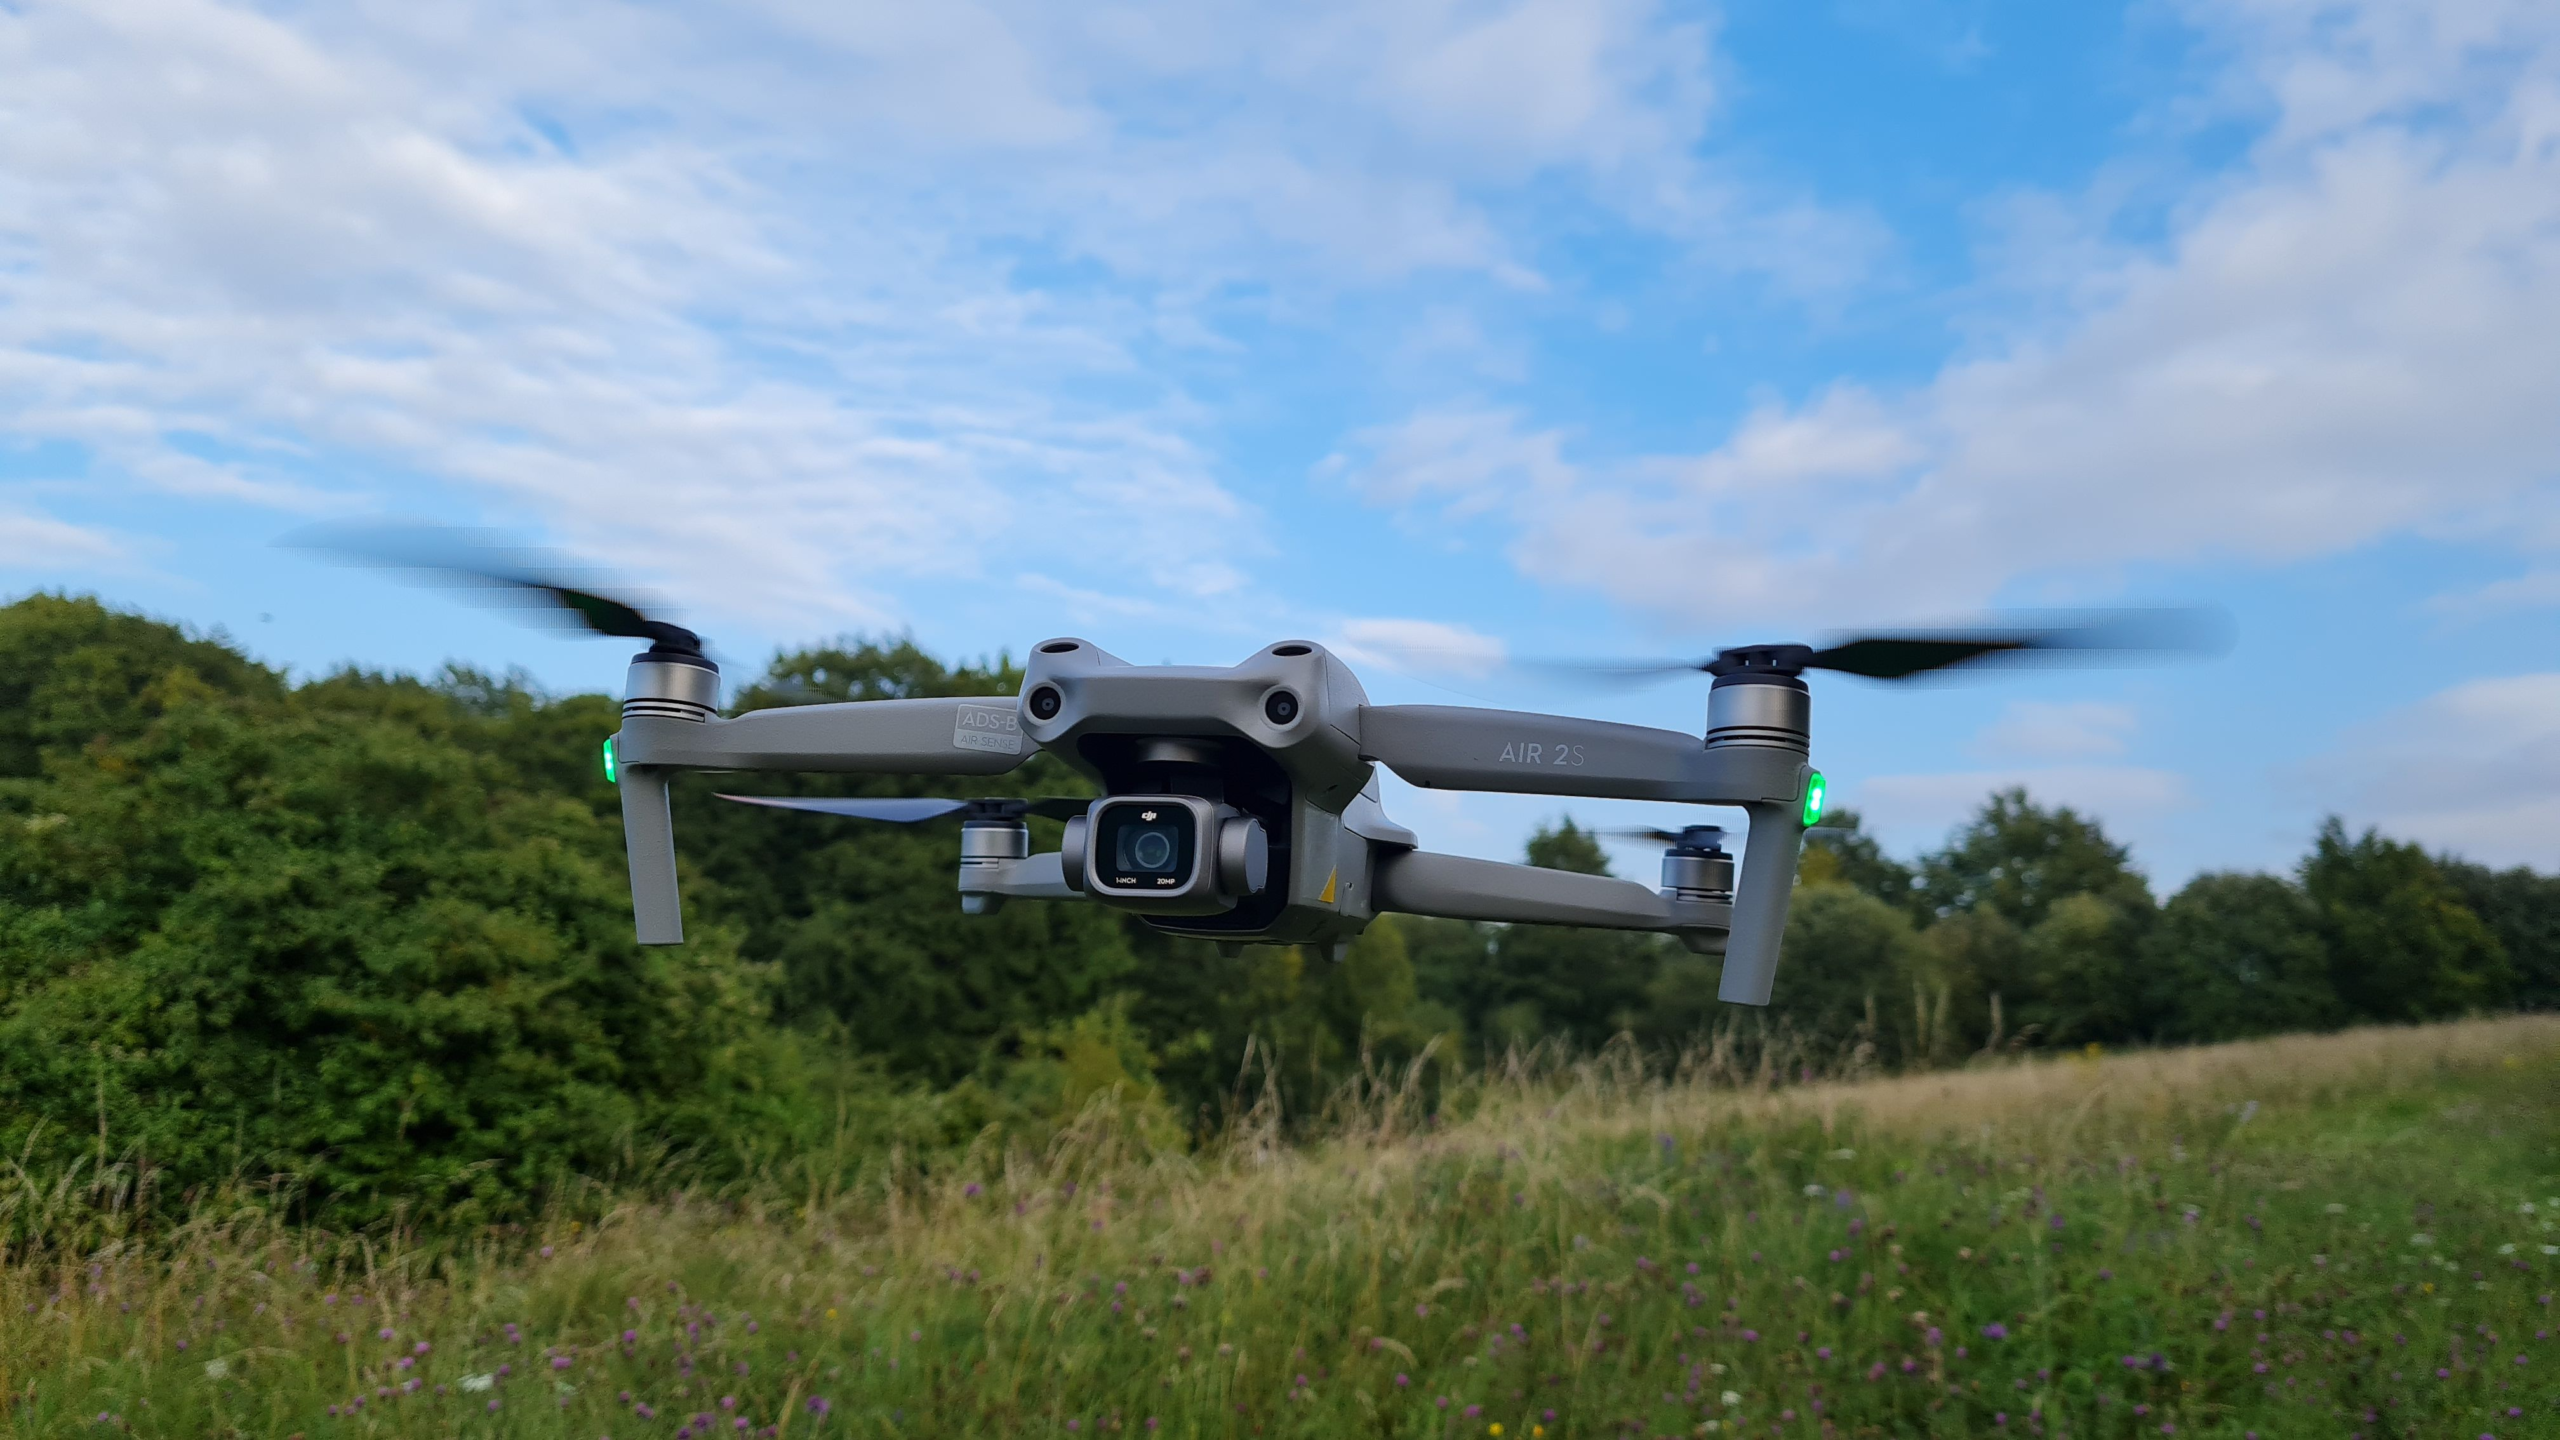
The Bundeswehr took the precautionary measure after malicious activity affected an update server associated with QBase, the ground-control and mission-planning system used with the company’s unmanned aircraft. The incident reportedly prevented the equipment from participating in a recent military exercise.
Quantum Systems, a German defence technology company based in Bavaria, identified the incident in late October. It said a malicious update file had been distributed through infrastructure used to update QBase, and that its security teams contained the threat in cooperation with relevant authorities.
The company maintains that its drone fleet remains operational and that there is no risk to end users or operators. The German defence ministry declined to discuss the readiness of military equipment, leaving the full operational scope of the precautionary grounding unclear.
Software distribution becomes a defence dependency
The attack concerns a particularly sensitive part of the technology supply chain. Software update systems provide a mechanism for distributing fixes, features and configuration changes to equipment already deployed by customers. Their credibility depends on the integrity of the infrastructure that prepares, signs, stores and distributes the software.
Where an attacker can place an unauthorised file within that distribution process, the issue extends beyond conventional access to a supplier’s corporate network. Operators must determine whether affected software was received, whether it was executed and whether assurances about the equipment’s operational state remain reliable.
There is no confirmed public evidence that the Quantum Systems incident resulted in malicious software running across the German military’s drone fleet. The reported grounding is better understood as a precaution while the integrity of the update process and associated systems is established.
A compromised update server does not necessarily mean every connected device has been compromised. However, the uncertainty can still affect the availability of equipment whose operators must maintain a higher level of confidence in its configuration and behaviour.
European defence suppliers face increasing scrutiny
Quantum Systems has expanded its activities supporting Ukraine and operates in a market where unmanned aircraft are increasingly integral to surveillance, reconnaissance and other military operations. Its presence in
Ukraine and its relationship with European defence customers increase the potential significance of any disruption affecting software assurance or equipment readiness.
The company has not identified the attacker publicly, and available information does not establish whether the intrusion was conducted by a state-backed group, a criminal actor or another party. Nor has the company confirmed that its Ukrainian operations were affected.
Defence procurement has traditionally placed considerable emphasis on hardware performance, reliability and supplier capacity. Software-dependent systems introduce additional obligations around update provenance, vulnerability management, secure maintenance and the ability to verify that equipment has not been altered outside authorised processes.
Such obligations extend across suppliers and subcontractors. Software may be developed by one organisation, distributed through another infrastructure provider and installed by a separate maintenance team. Each relationship can affect the evidence available during an incident and the speed with which a customer can restore confidence in an affected system.
The temporary withdrawal of equipment from an exercise also demonstrates that operational consequences do not require a successful destructive attack. A credible concern about update integrity may be sufficient to suspend use until relevant technical checks have been completed.
Quantum Systems says its security teams contained the incident and are cooperating with authorities. The investigation must now establish the extent of the compromised distribution process, whether customer systems received affected material and what technical assurances support the restoration of normal military use.