
Critical systems
-

INC linked to SonicWall exploitation campaign
Researchers have linked INC ransomware activity to attacks exploiting two SonicWall SMA 1000 vulnerabilities, although the vendor has not publicly attributed the campaign.
-

UKGI file exposed officials’ work details
A UK Government Investments file containing management information and the work details of 51 officials remained publicly accessible for around 40 hours after a policy failure.
-
PNLD confirms police contact data breach
PNLD has confirmed that police and criminal-justice contact information was compromised and published on the dark web, while ruling out exposure of passwords and crime records.
-
5G core flaws expose inherited trust
Researchers found 84 previously unknown vulnerabilities across seven open-source cellular cores, including weaknesses capable of denial of service and session hijacking.
-
ECB stress test finds cyber modelling gaps
The ECB found weaknesses in how eurozone banks connect severe geopolitical and cyber scenarios to capital, liquidity, and credible management action.
-
The energy sector cyber security strategy: why leadership must act now
Rafael Narezzi, CEO of Centrii, argues that the UK’s energy cyber strategy makes resilience a leadership and operational priority, not a deferred compliance task.
-
Russian zero-click campaign targets Zimbra mail
The NCSC and international partners say Russian state-supported actors used a Zimbra zero-click exploit to steal email data from Western organisations.
-
UK education and police support data stolen
Hackers have claimed data from Department for Education and Police National Legal Database-linked systems, exposing public-sector contact records and staff details.
-
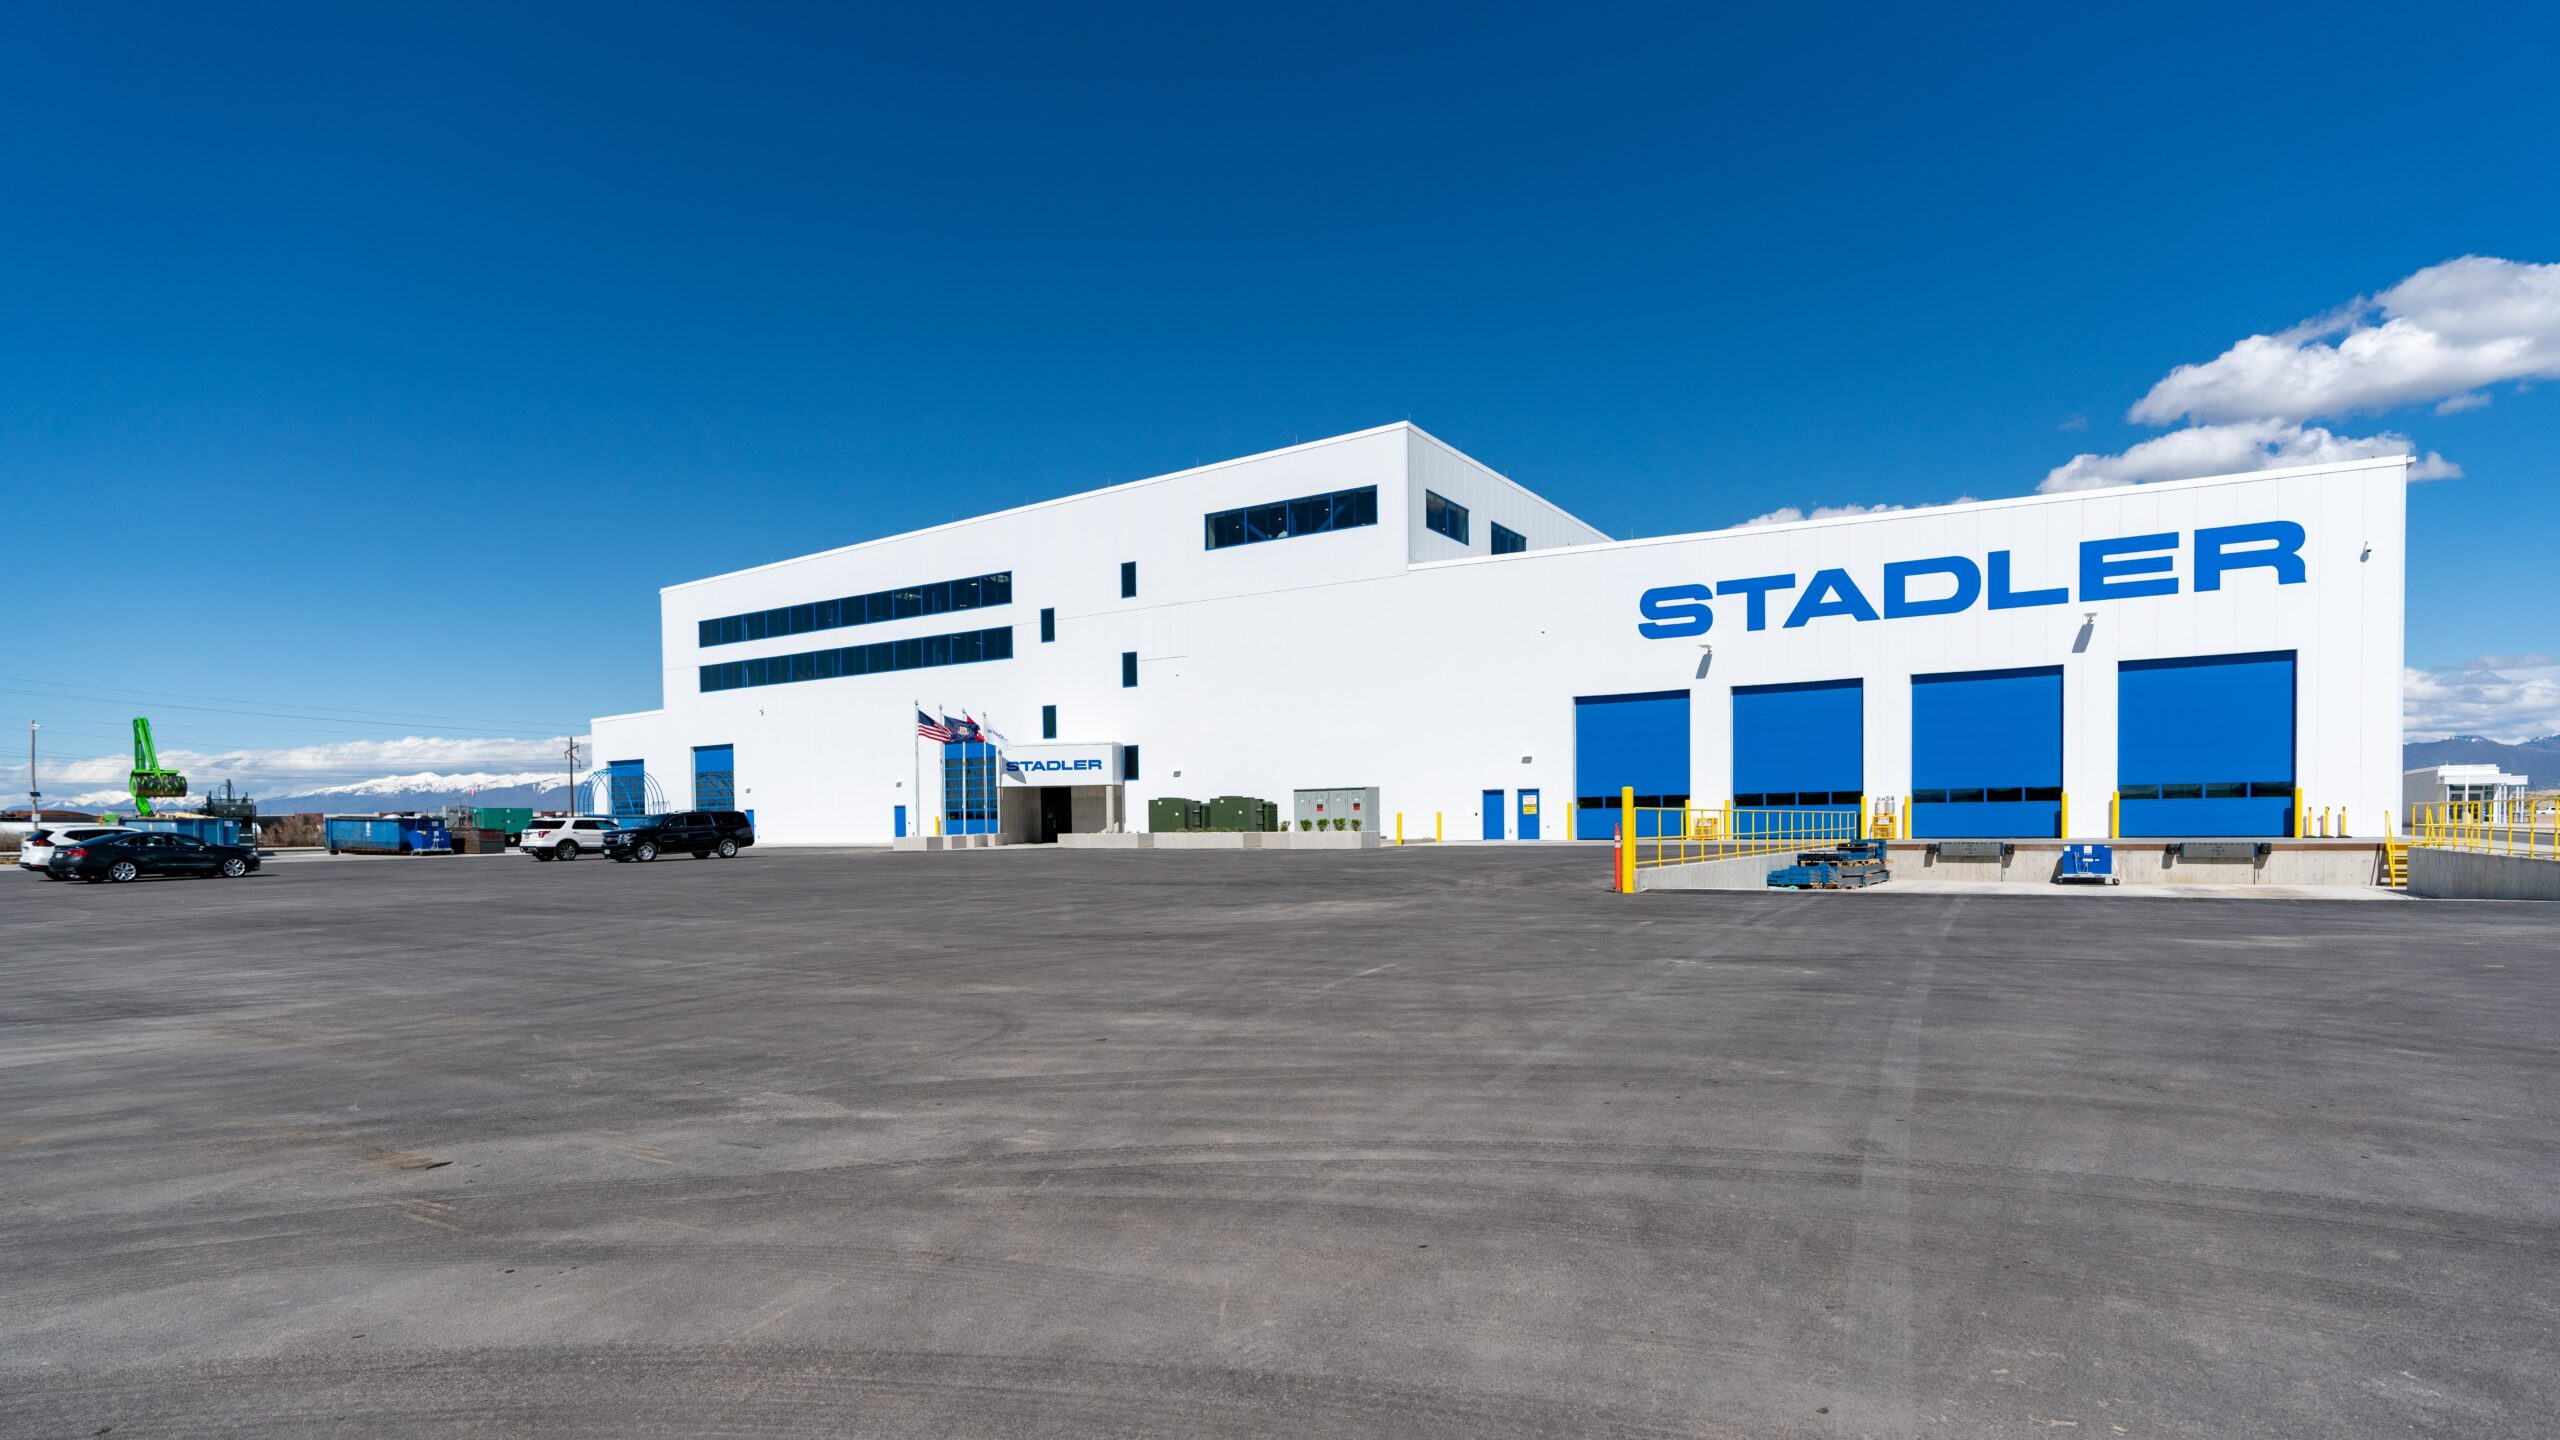
Rail supplier portal breach reaches Stadler
A supplier platform incident at Stadler exposed technical data without affecting rail vehicles, production, personal data, or operational systems.
-
CNI supplier access emerges as repeated attack route
e2e-assure research says CNI organisations are experiencing repeated supplier compromise and credential theft, while many only review third party access after incidents.