
Data & infrastructure
-
Codex sandbox flaws crossed host boundary
Two OpenAI Codex sandbox weaknesses allowed researchers to cross intended containment boundaries, including one route from read-only mode to unsandboxed commands on a developer host. Both were fixed before disclosure.
-
Arista says VeloCloud flaw actively exploited
Arista has disclosed active exploitation of a critical VeloCloud Orchestrator vulnerability that can expose privileged internal functionality and compromise the management system and data it controls.
-
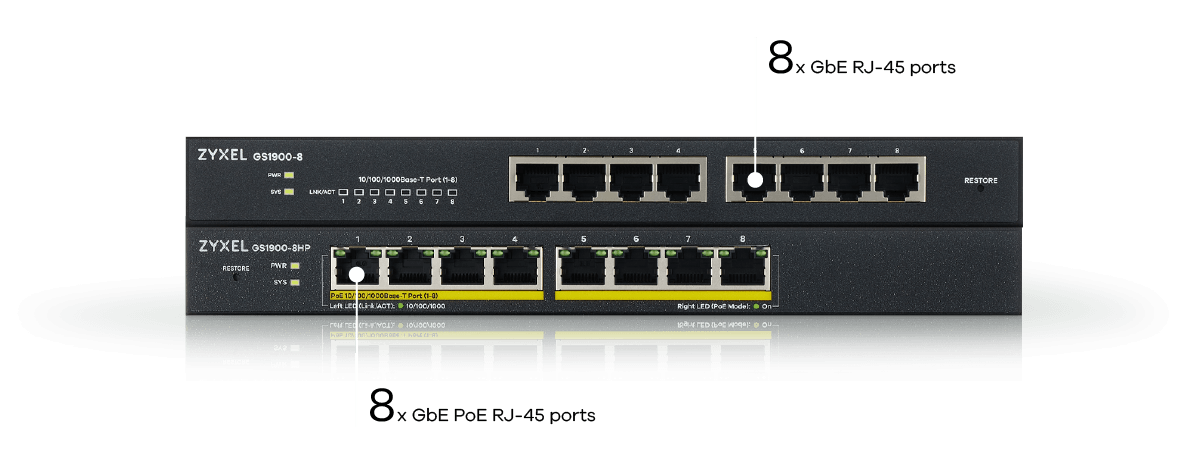
Attackers compromise 996 Zyxel switches
GreyNoise says an attacker compromised 996 Zyxel GS1900 switches across 48 countries through CVE-2026-7273, a vulnerability Zyxel patched in June.
-
Ribon compromise exposes BigCommerce customer data
Compromised credentials belonging to third-party BigCommerce applications were used to access merchant data and inject malicious scripts, exposing the dependency risk created by privileged ecommerce integrations.
-
Ransomware disrupts Windows through Group Policy
Kaspersky has documented an attack that used Active Directory Group Policy to disrupt an entire Windows domain without encrypting files on its workstations.
-
Dragos closes runZero and NetRise acquisitions
Dragos has completed its runZero and NetRise acquisitions after Accenture’s majority investment, expanding from OT security into asset discovery and software supply-chain visibility.
-
Belgian federation disputes cyber breach claims
Belgium’s AFTT says current checks do not support claims that its results infrastructure or private contact data were compromised, while a separate gymnastics breach remains confirmed.
-
Google fined €403m over location data
Ireland’s Data Protection Commission has fined Google €403 million after finding GDPR failures across three services that processed users’ location information.
-
LMU Munich breach exposes student records
LMU Munich says an attacker retrieved student enrolment data that may include identity, banking, health-insurance, academic-history, and other personal information.
-
WordPress fixes Click2Shell theme-install flaw
WordPress 7.1.1 fixes a flaw allowing crafted links to trigger theme installation, while researchers showed how it can be chained with a second weakness to reach code execution.