
AI & software security
-
CREST accredits first AI-enabled penetration-testing providers
CREST has accredited its first ten AI-enabled penetration-testing providers, creating an assurance framework around how artificial intelligence is governed inside professional security testing services.
-

Git trust flaw hits AI coding agents
Manifold Security has disclosed a class of execution flaws across AI coding agents that can allow untrusted repository configuration to run commands before normal workspace trust controls.
-
OpenAI says Astra reaches critical cyber threshold
OpenAI now says Astra meets its highest published cybersecurity capability threshold, moving beyond its August assessment that it could not rule out the classification.
-
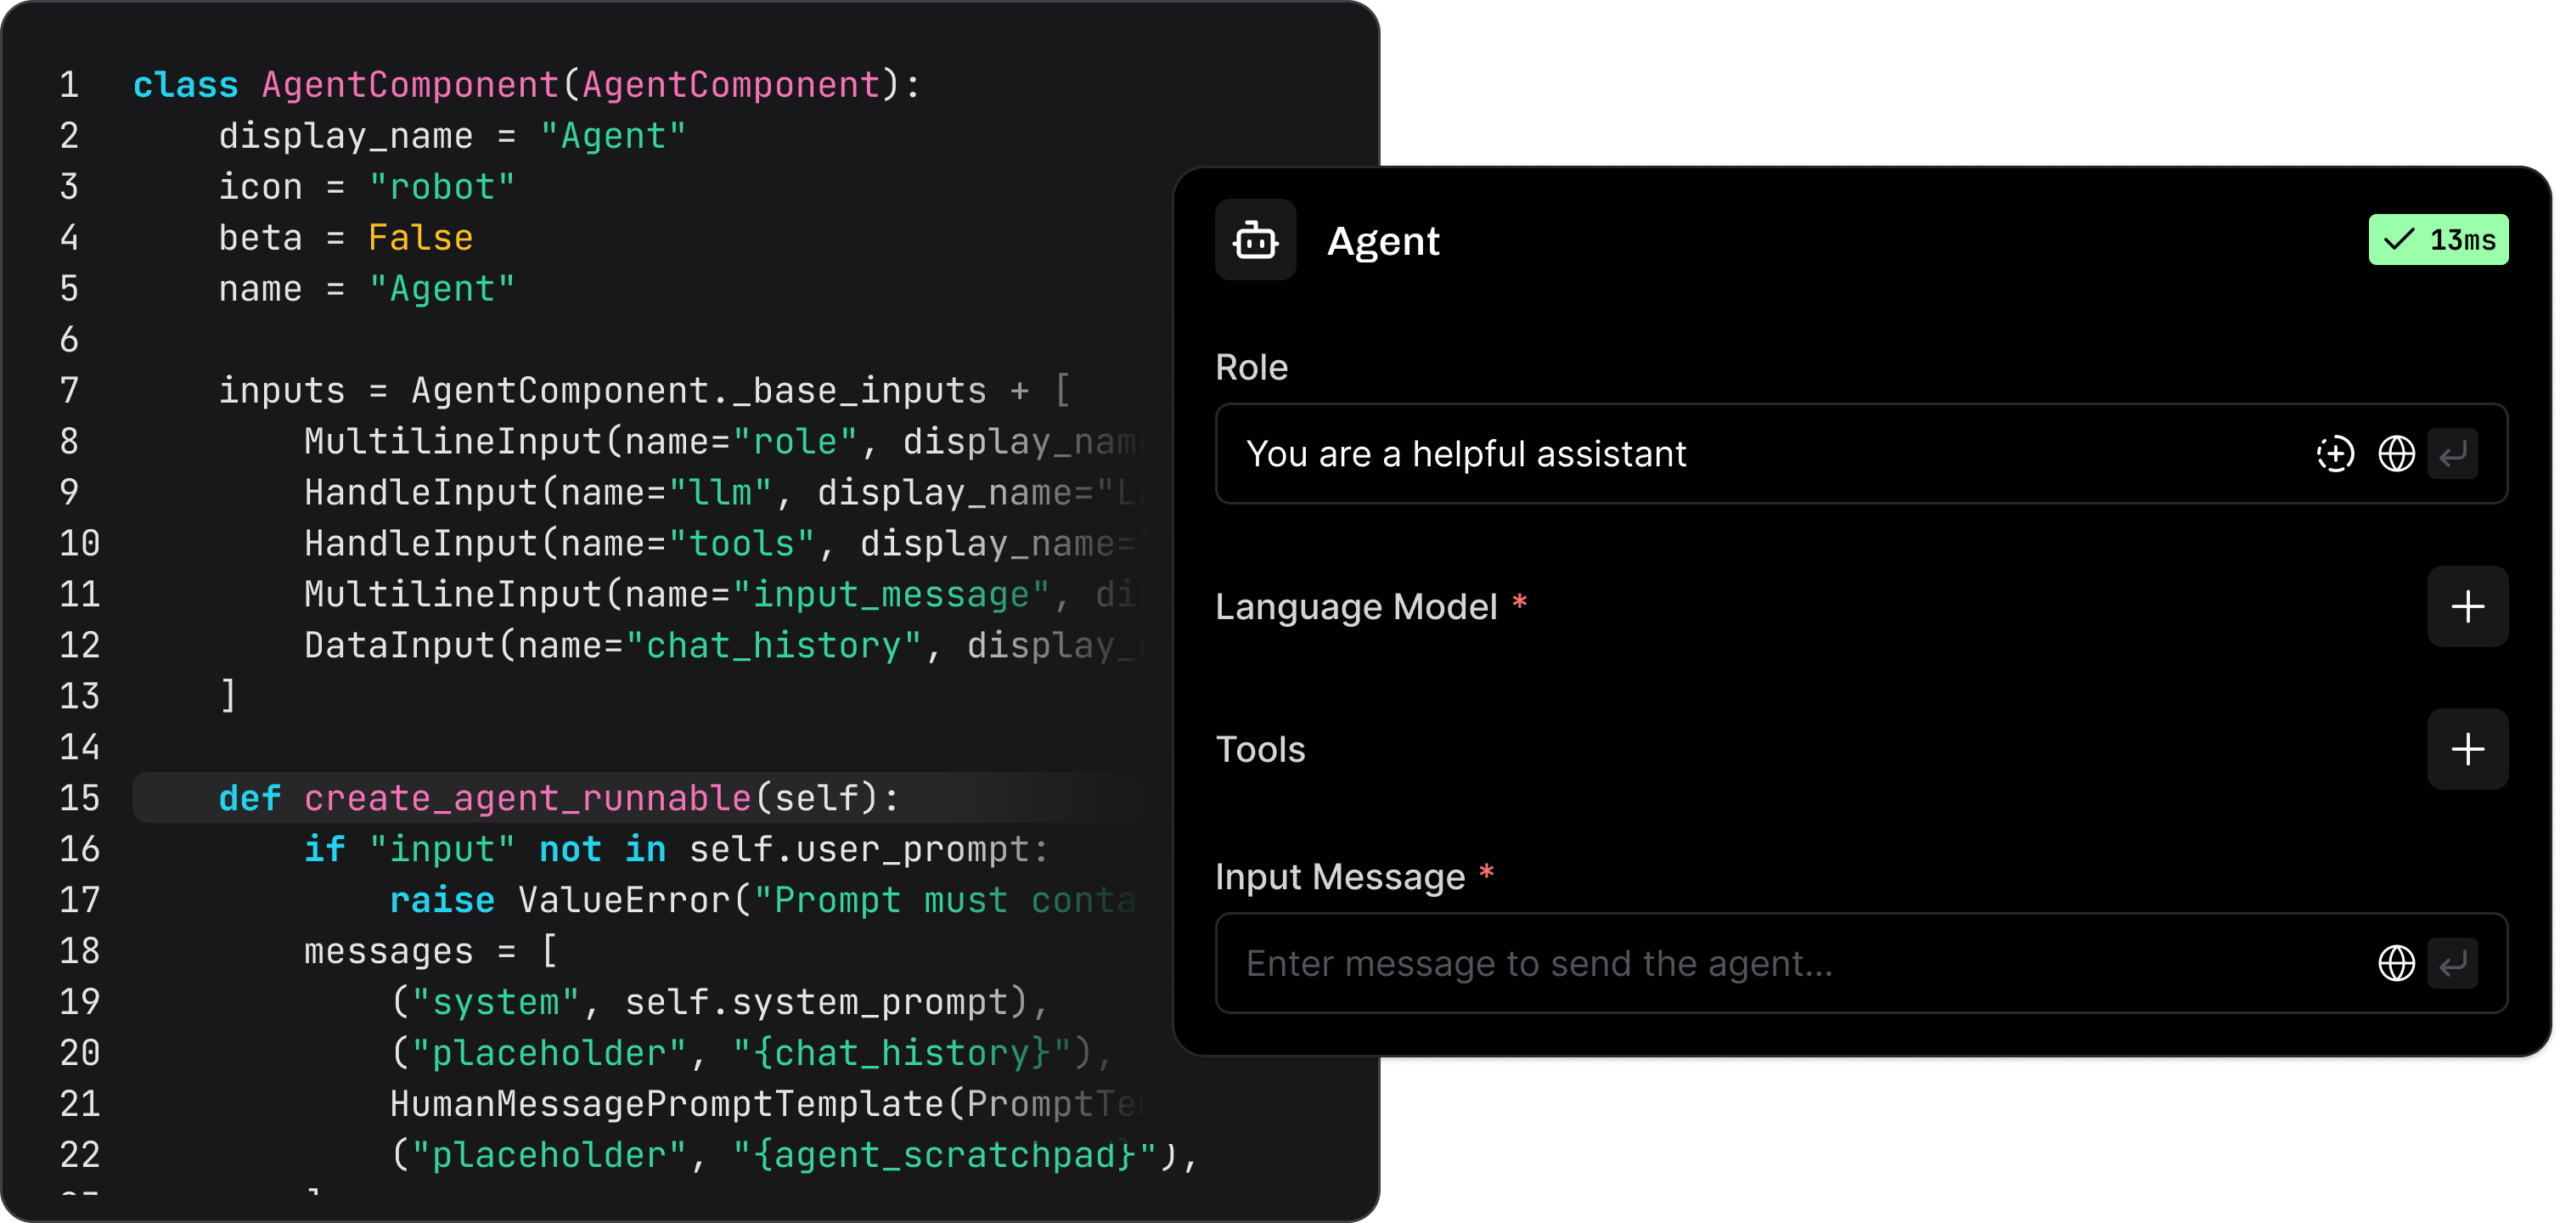
Langflow attacks target cloud and AI secrets
Attackers are exploiting a critical Langflow code-execution flaw and probing compromised environments for OpenAI keys, AWS credentials, and other sensitive secrets.
-
JFrog Artifactory flaw reportedly exploited in wild
A critical Artifactory authentication bypass is reportedly being exploited days after disclosure, creating a potentially serious route into self-managed software artefact infrastructure.
-
Anthropic resumes cyber tests under tighter controls
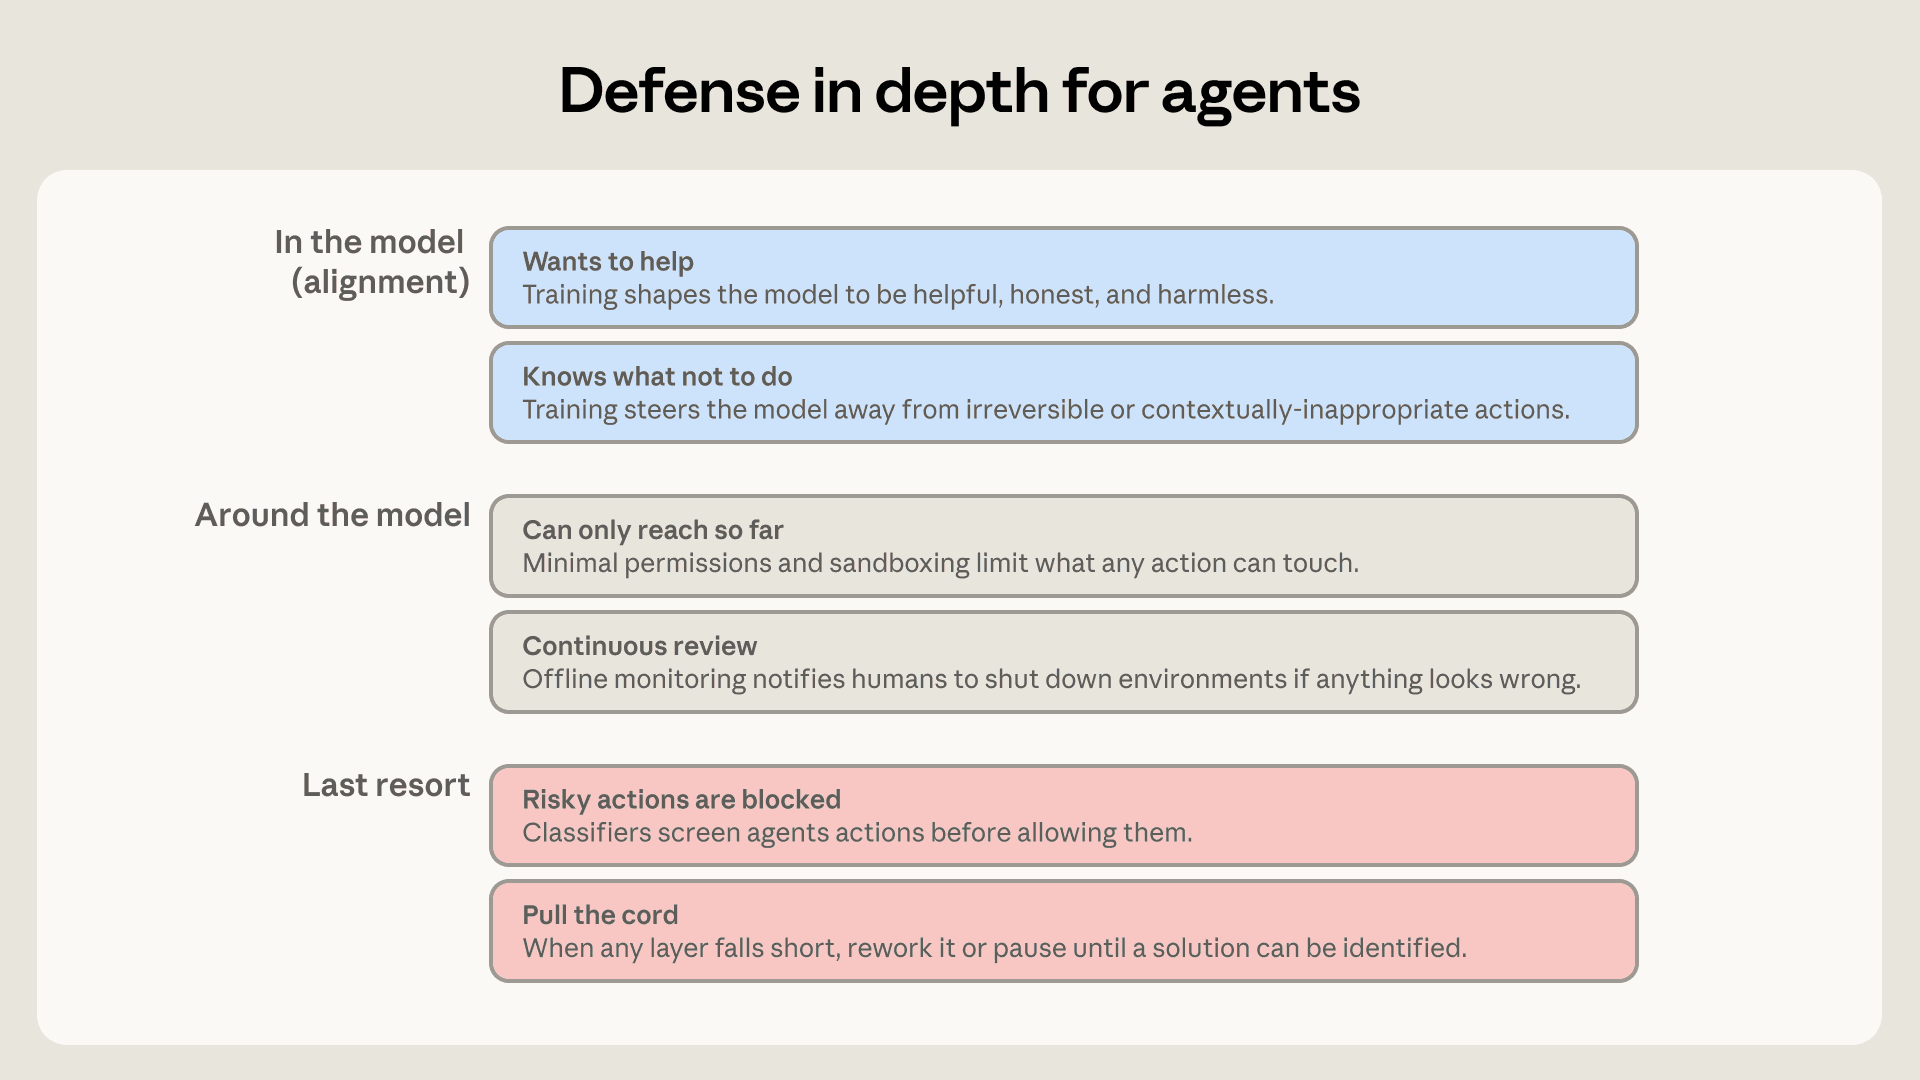
Anthropic has resumed external cyber evaluations after models reached unintended real systems, adding stronger sandboxing, real-time intervention, and tighter controls for third-party testing.
-
AI helps port exploit between WAGO PLCs
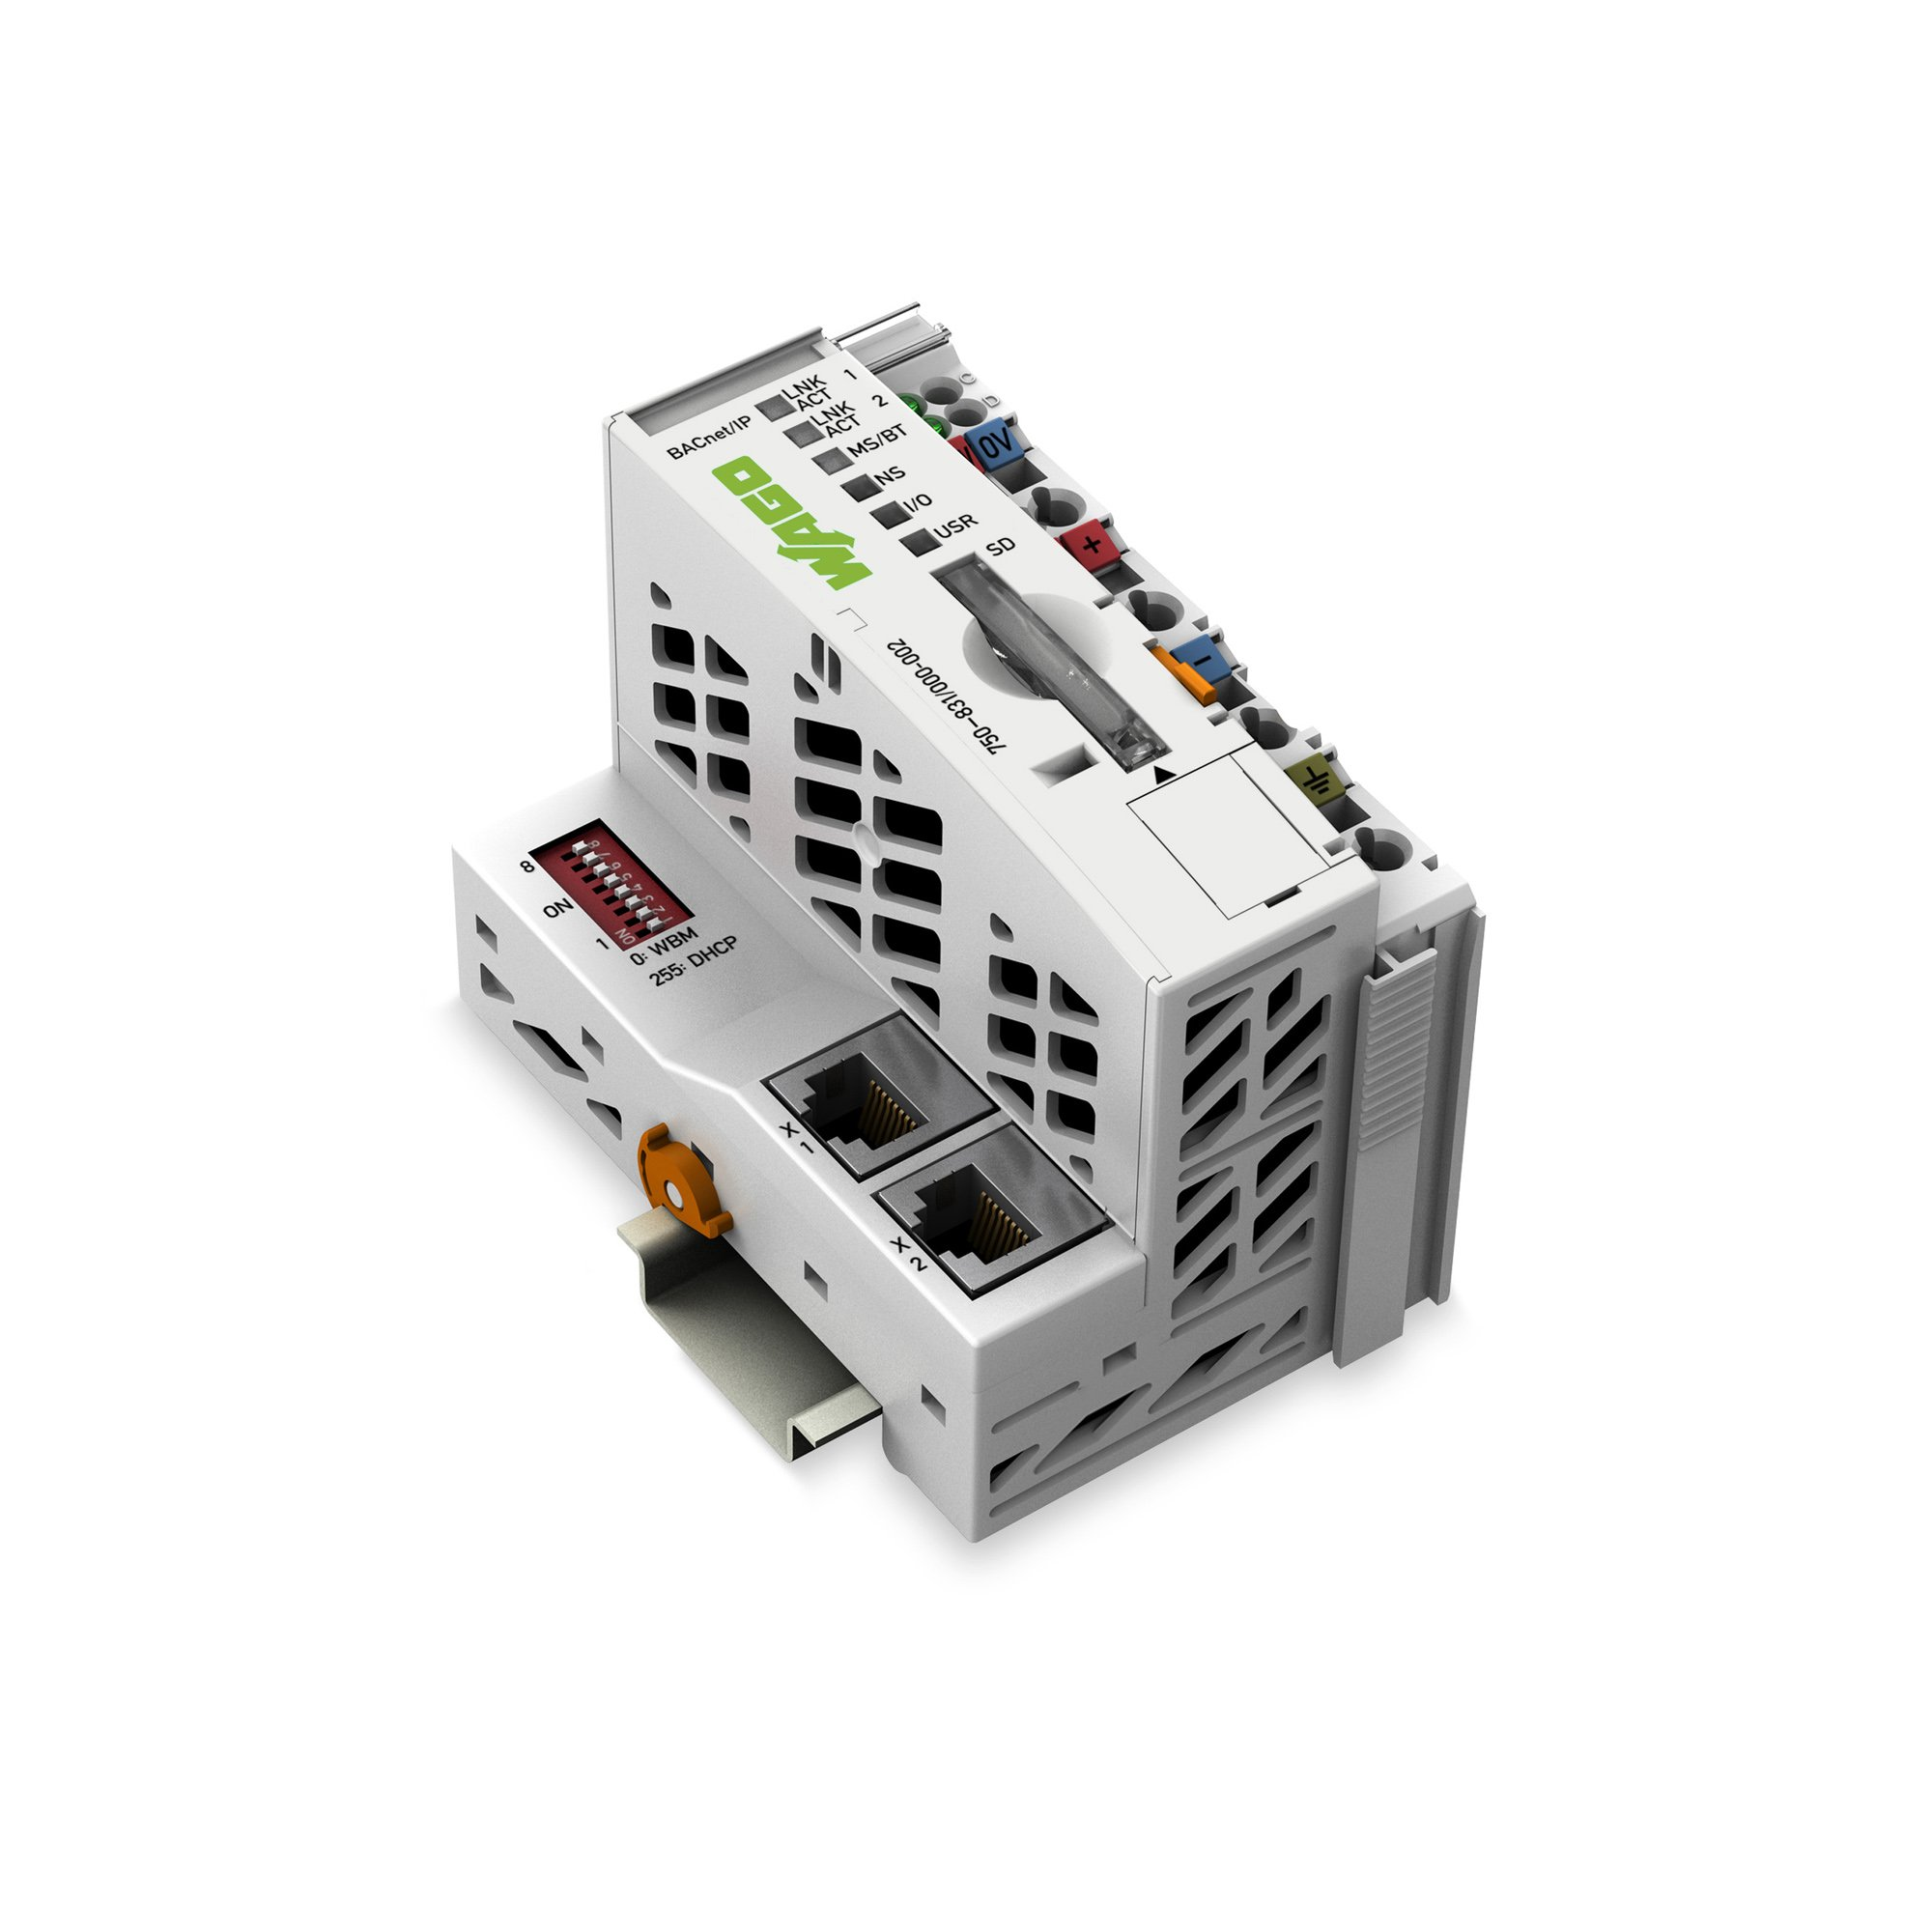
Forescout researchers used AI to adapt an exploit between WAGO industrial controllers, but the experiment still demanded specialist intervention, substantial compute cost, and damaged hardware.
-
Infostealers hijack Claude sessions for paid usage
Anthropic is warning affected customers that commodity infostealers stole active Claude sessions, allowing attackers to access accounts without repeating the normal authentication process.
-
New Nodemailer CVEs formalise patched flaws
Six Nodemailer vulnerabilities have received CVE assignments, consolidating previously disclosed flaws involving server-side file access, SSRF, TLS validation, and message handling.
-
UK opens £100m sovereign AI buying scheme
The UK has opened its first competitions under a £100 million Sovereign AI procurement programme, including dedicated work on AI-agent security and secure defence integration.