
Threats & incidents
-

VPN bypass opens path to Qilin ransomware
A configuration-dependent GlobalProtect authentication bypass has become an initial-access route for intrusions involving credential theft, data exfiltration, encryption, and Qilin ransomware.
-

VeloCloud zero-day reaches the network control plane
Attackers are exploiting a maximum-severity vulnerability in on-premises VeloCloud Orchestrator systems, exposing the management layer above distributed branch, retail, industrial, and remote-site networks.
-
Remote hiring campaign reaches UK bank
Hundreds of suspicious applications for remote jobs at an unnamed British bank have placed recruitment controls alongside identity governance, insider risk, and sanctions compliance.
-
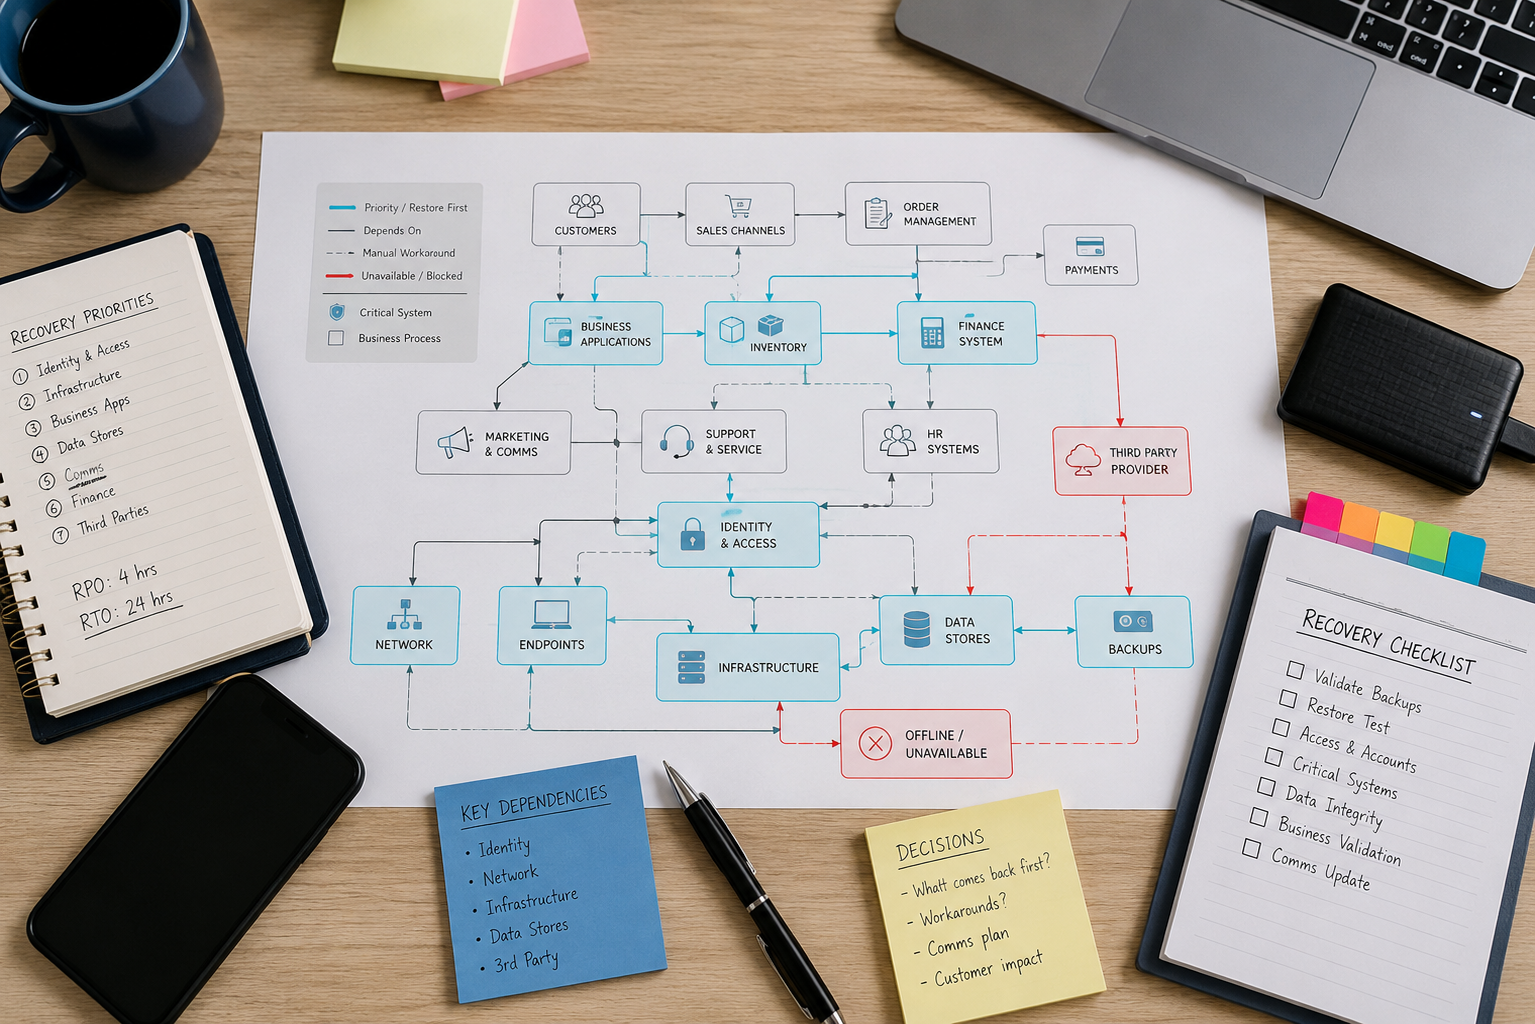
The backup myth: why copied data won’t save your business
William Thackray, Operations Director of AGT Computer Services, argues that backups alone cannot prove ransomware resilience unless restoration is tested against operational reality.
-
Open Tribeca databases exposed contact network
Four publicly accessible databases reportedly contained hundreds of thousands of Tribeca-related records, including contact details, account information, IP addresses, and hashed passwords.
-
Hostile hotel Wi-Fi reroutes Microsoft logins
Attackers are compromising hospitality gateways and poisoning DNS responses to redirect connected users towards counterfeit Microsoft 365 authentication pages.
-
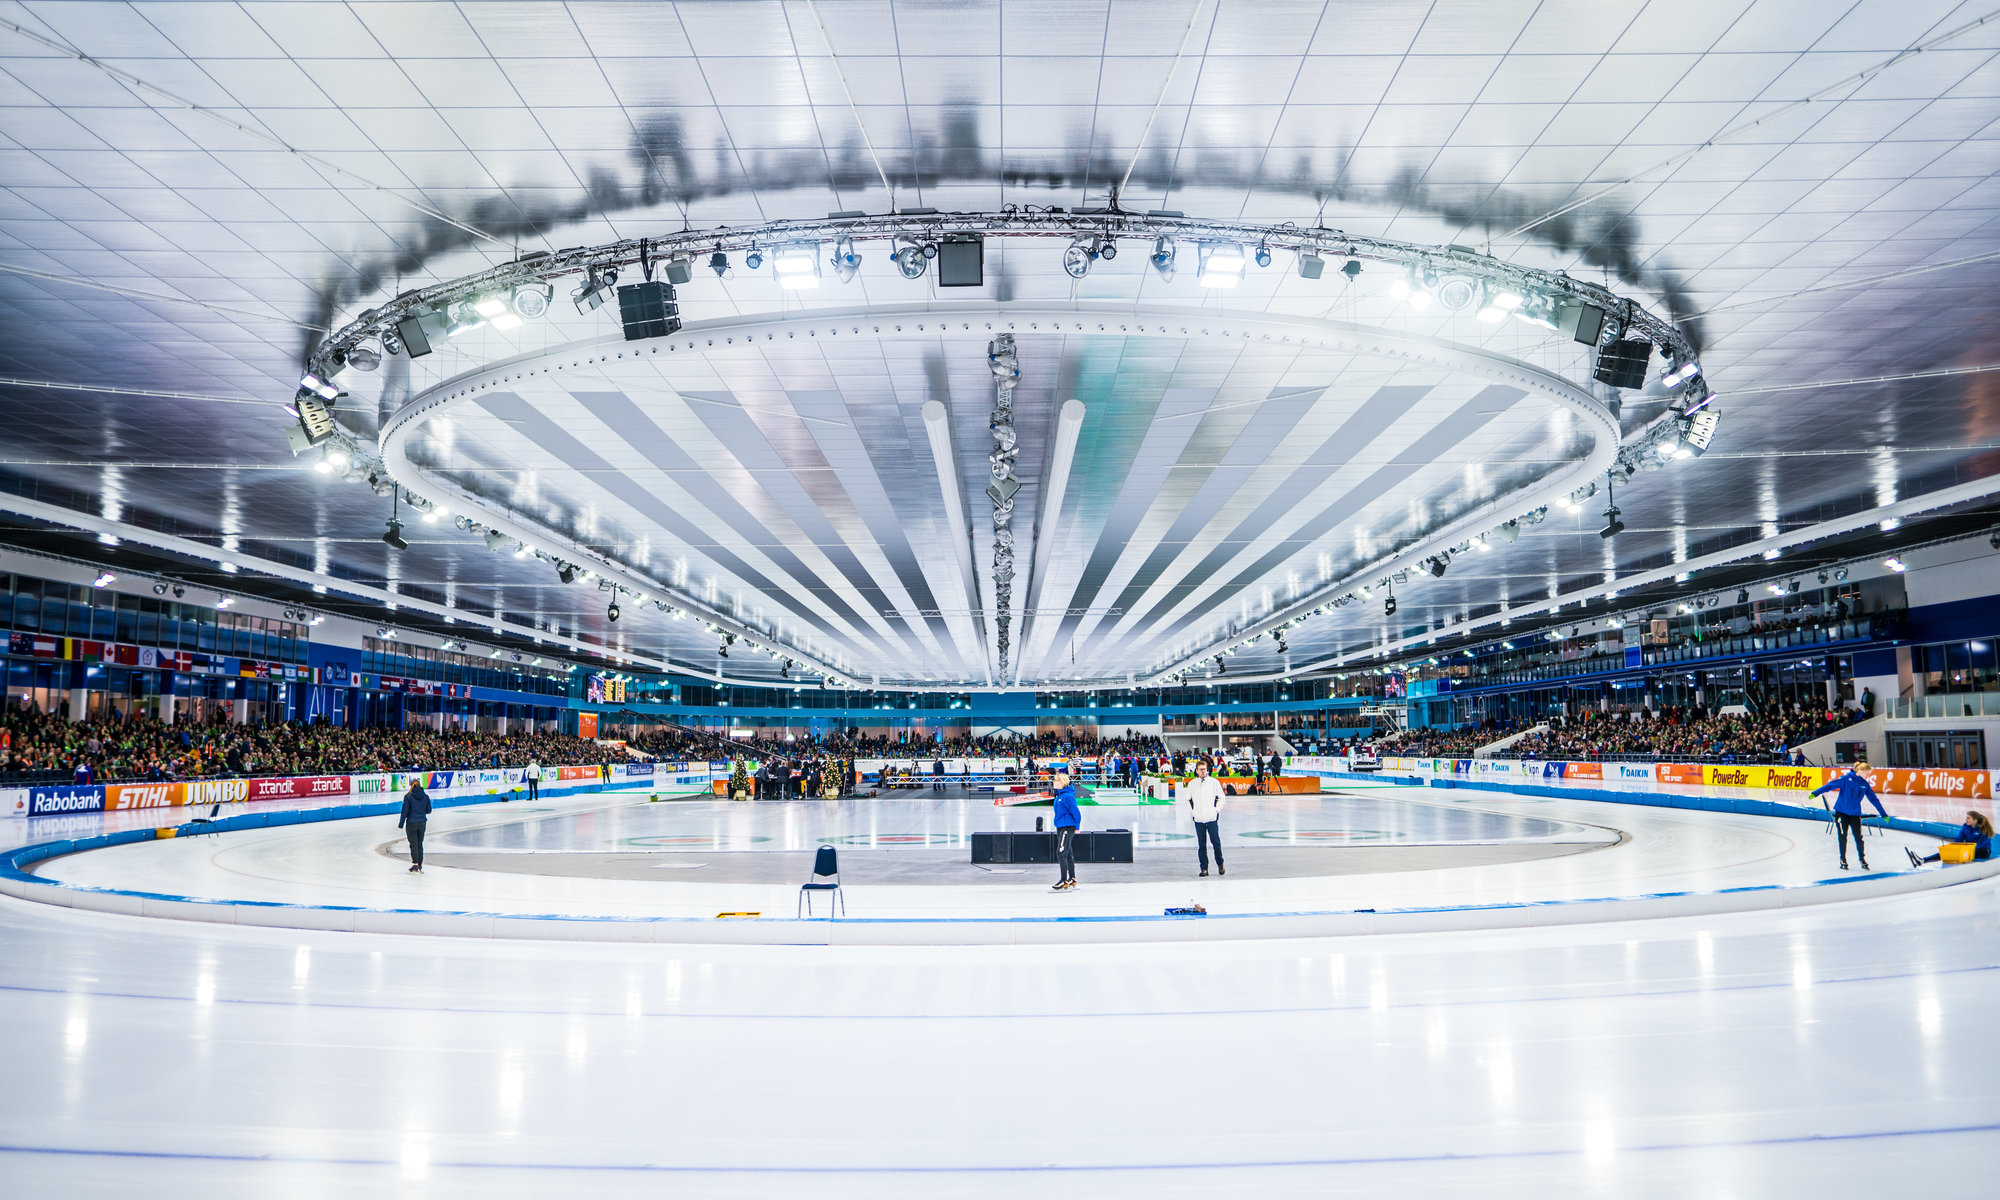
Thialf disputes ransomware claims after cyberattack
The Dutch arena has confirmed a cyberattack but says neither its data nor its operations were affected, contradicting separate claims of theft and extortion.
-
ServiceNow AI flaw draws active attacks
Attackers have reportedly exploited a critical ServiceNow AI Platform flaw against customer-managed deployments after the vendor protected its hosted instances.
-
Iran-linked attacks widen across industrial controllers
US authorities have expanded an alert on Iran-affiliated activity to include Siemens and Schneider controllers widely deployed across European infrastructure.
-
Check Point flaw reaches firewall control plane
An actively exploited authentication bypass exposed internet-facing Check Point management systems, placing firewall policy and administrative infrastructure within an attacker’s reach.