
Summary
- The 13 October ProductCERT notice concerns the TM MFP GNU/Linux subsystem.
- Some vulnerability scores reach 10.0 under CVSS v3.1, but impact depends on configuration.
- Siemens says fixes are being prepared and specifies mitigations in the interim.
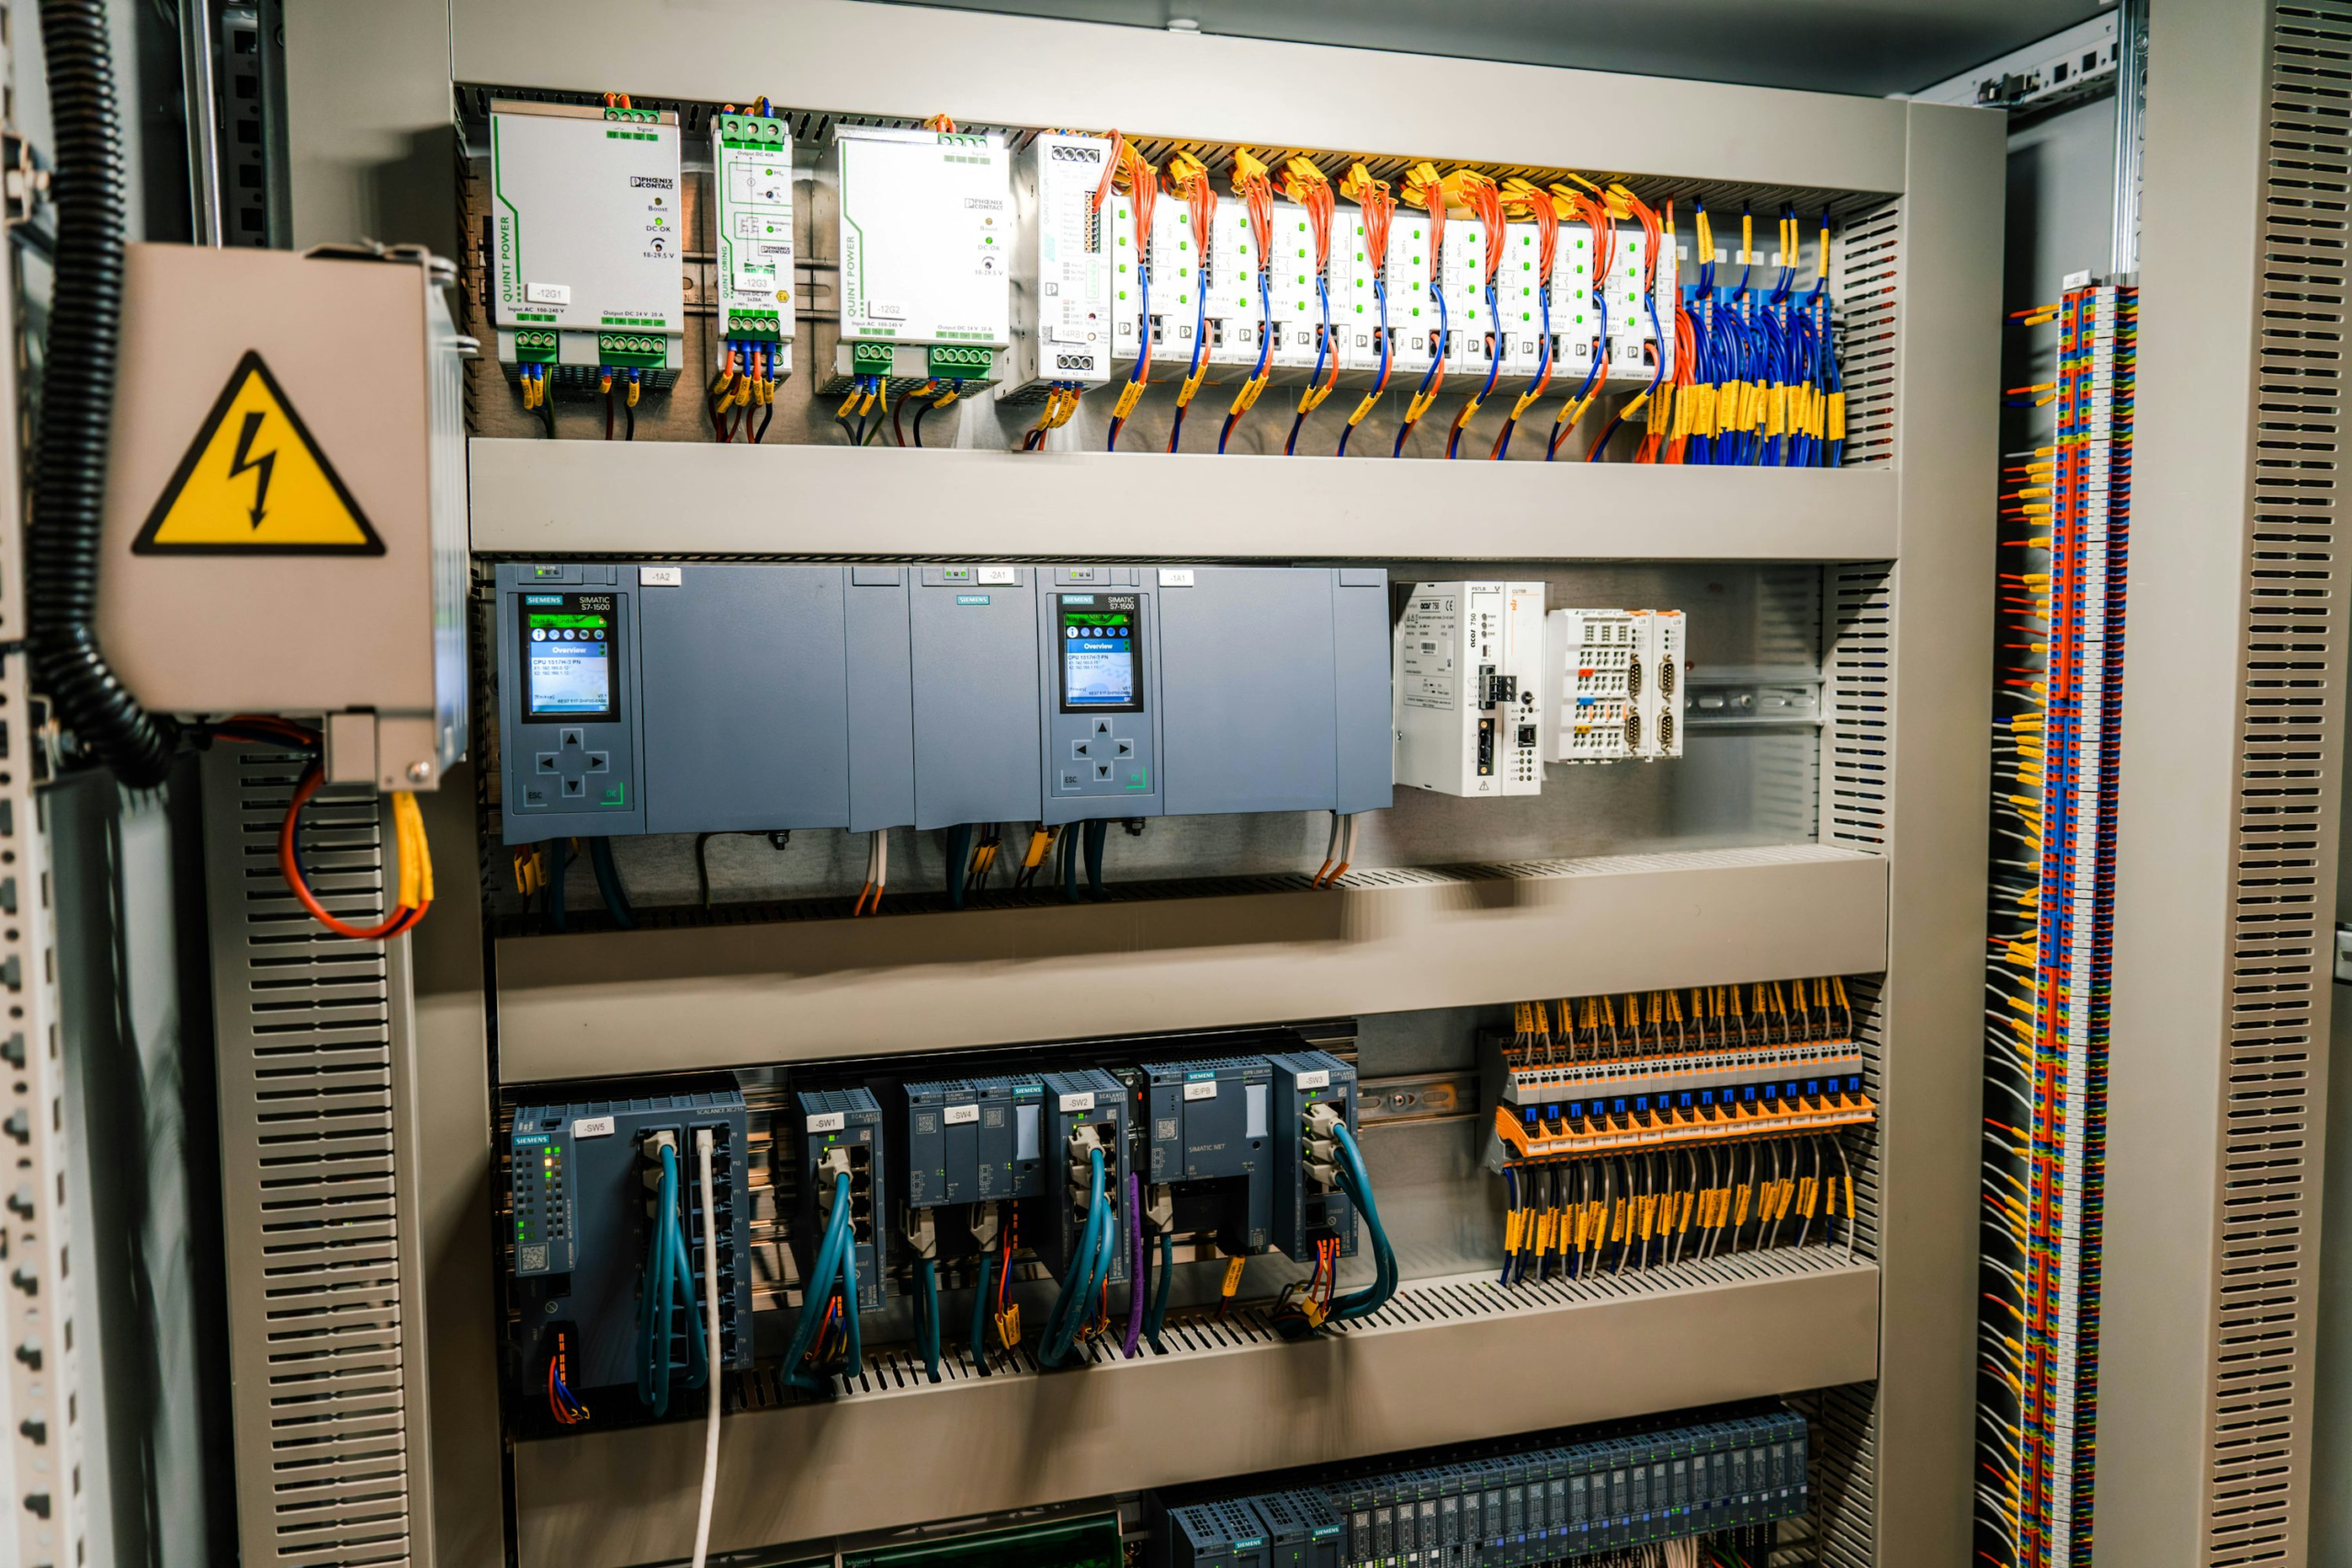
Siemens ProductCERT has published an advisory covering multiple vulnerabilities in the additional GNU/Linux subsystem of its SIMATIC S7-1500 TM MFP industrial automation module. The 13 October notice, SSA-784472, concerns the multifunctional platform’s software environment, rather than every S7-1500 controller or all products in the wider Siemens automation portfolio.
The advisory assigns a maximum CVSS v3.1 base score of 10.0 among the issues it covers. That severity is an indication of the potential effect under the scoring assumptions, not proof of exploitation or an automatic measure of every installation’s real-world exposure. Siemens says it is preparing fixes and that no fix is currently available for at least some affected versions or vulnerabilities.
Industrial multifunctional modules can execute additional software alongside automation tasks, making their configuration and application components a separate security boundary from the core controller function. The use of a GNU/Linux subsystem introduces dependencies familiar to conventional IT teams into an environment where changes may be constrained by production needs and equipment certification.
According to the published product description, the advisory specifically identifies the additional GNU/Linux subsystem associated with SIMATIC S7-1500 TM MFP V1.1.1. Its affected-products table identifies instances where versions remain vulnerable and points users to mitigations rather than a simple universal upgrade. Organisations should therefore match the exact module variant, software build and deployment conditions against the vendor’s live notice.
Siemens recommends running only applications from trusted sources among its interim measures. Restricting what can execute inside a module is particularly relevant when optional software adds flexibility but also creates a path through which a compromised application could affect the host environment. Additional network boundaries and access controls may limit the number of actors able to interact with affected services.
Manufacturing lines and other industrial assets often operate within change windows that are less flexible than those used for office endpoints. Some industrial components support processes that are difficult to interrupt, and testing an update can take longer where a controller interacts with drives, sensors or safety functions. Where an immediate patch is unavailable, the distinction between exposure reduction and vulnerability elimination should remain explicit in risk records.
The ProductCERT advisory does not, by itself, demonstrate compromise of factories using the equipment. Nor does the highest severity score establish that arbitrary internet users can reach an affected module. Exposure depends on installation design, the software present, privileges and the paths available across industrial networks. A meaningful assessment would distinguish modules installed but not using the affected subsystem from those that execute supplementary workloads.
Responsibility for the Linux subsystem may sit across different engineering and software teams. A control engineer may manage the PLC programme and input/output configuration, while a separate software team maintains applications running on an attached Linux environment. If the manufacturer later provides a corrected component, the update may have to pass through both groups before reaching production. Meanwhile, the advisory's recommendation to run trusted applications helps reduce one route of exposure but does not change the vulnerability's underlying existence. The manufacturer explicitly distinguishes mitigations from a fix and records the CVEs against affected versions. Security records should preserve the distinction rather than recording the product as patched solely because supplementary restrictions are in place.
With remedies still being prepared for some affected components, the publication date and the availability of corrected software are separate milestones. A future update to the advisory may change the available fixes without changing when the issue was first disclosed. That is why the version of the advisory and its last-update date are useful elements of an industrial maintenance record, alongside the physical location of each affected module.
For European manufacturers operating Siemens automation equipment, the disclosure adds a software maintenance task that may sit between control engineering and enterprise security. Siemens’ advisory currently provides the authoritative list of affected versions, available remedies and interim recommendations, and will need to be revisited as the manufacturer releases fixes.



