
Regulation & Policy
-
Grok safeguards face a High Court test
A claim against xAI seeks permanent technical controls preventing Grok from generating sexualised manipulated images of an identified person, extending the requested remedy beyond removal after publication.
-
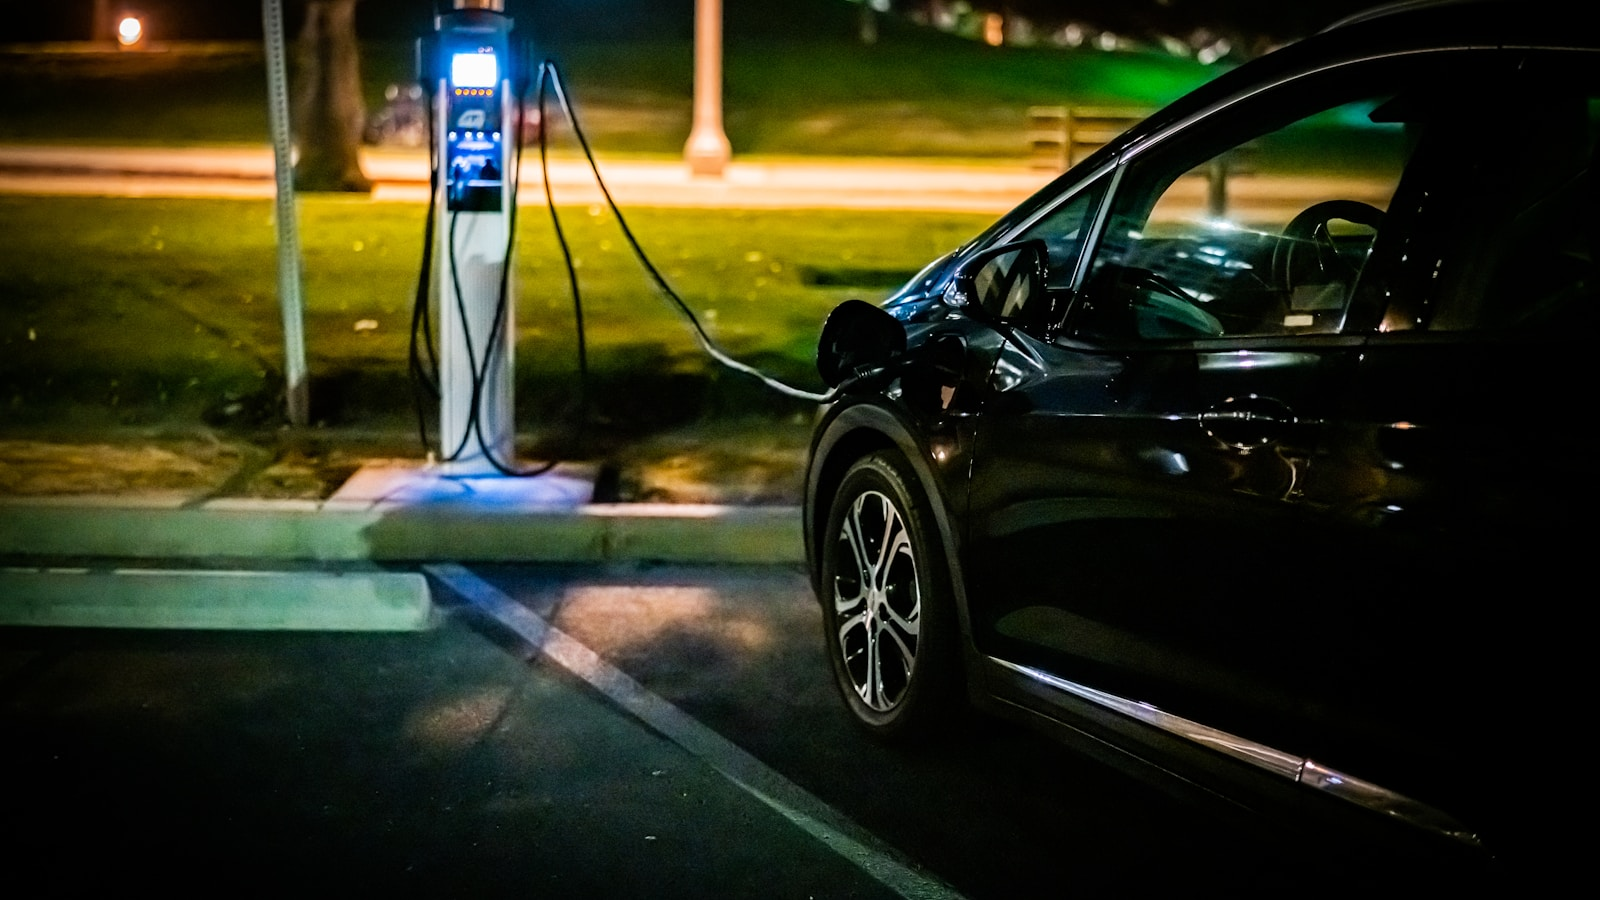
EV charging enters Germany’s cyber security programme
Germany’s BSI is developing requirements for connected charging infrastructure, where backend services, remote maintenance, payments, and grid integration turn product weaknesses into operational risk.
-
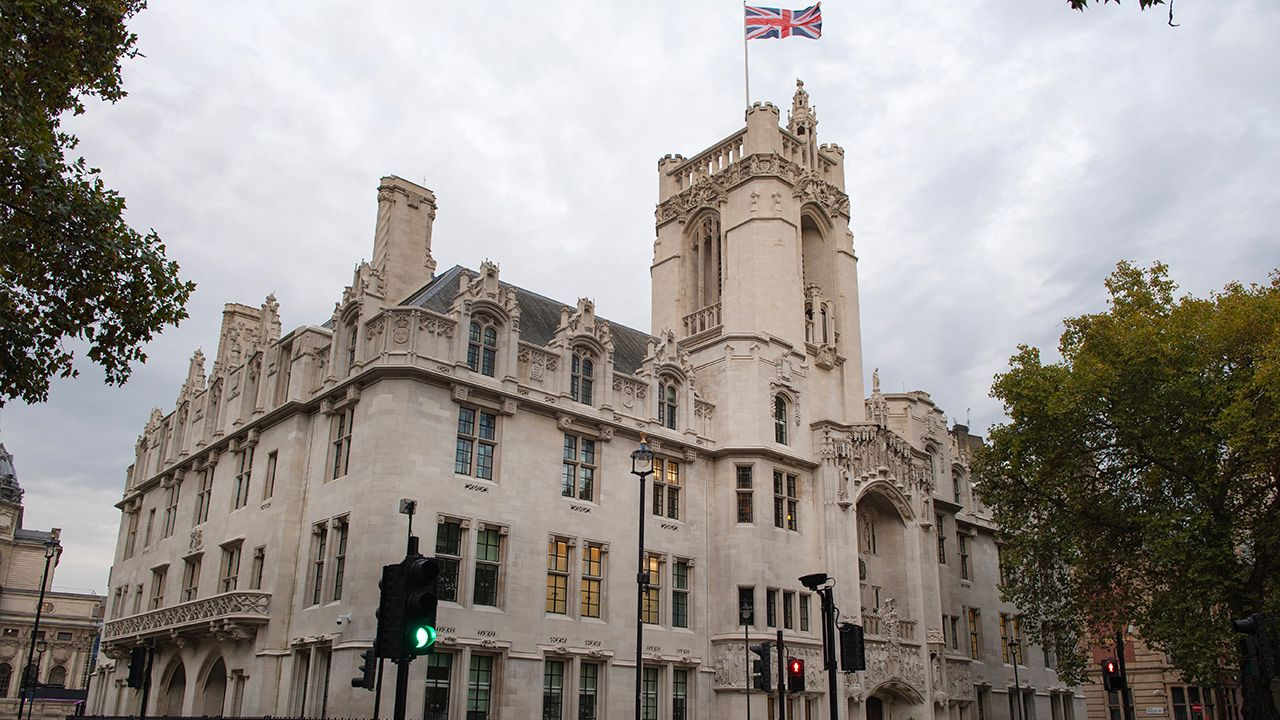
Spyware claim clears UK immunity hurdle
A divided Supreme Court has ruled that foreign-state hacking of a computer in Britain can constitute an act in the UK, allowing a civil spyware claim against Bahrain to proceed.
-

September reporting deadline comes into focus under CRA guidance
European Commission guidance clarifies product scope, support periods, open source treatment, risk assessments, and reporting duties before the Cyber Resilience Act’s first operational deadline.
-
UK cyber brief survives Whitehall restructure
Baroness Liz Lloyd has received joint appointments across two reorganised departments, preserving ministerial continuity as the UK expands cyber regulation and infrastructure oversight.
-
TeamViewer disclosure delay draws €240,000 fine
Germany’s financial regulator has fined TeamViewer after finding that its 2024 cyberattack should have been disclosed to the market without delay.
-
Europe sets assurance baseline for cyber providers
ENISA’s proposed certification scheme would establish common assurance requirements for managed security services, beginning with incident response and providers supporting the EU Cybersecurity Reserve.
-
Genetic data failures cost 23andMe €2.4m
Spain’s privacy regulator found that optional authentication, unrestricted data access, and delayed notification failed to protect highly sensitive genetic information.
-
Quantum migration moves into the boardroom
The NCSC says post-quantum cryptography migration needs executive sponsorship, supplier readiness, asset knowledge, and long-range resilience planning.
-
Germany builds a federal cyber control layer
CyberGovSecure will centralise cyber governance across Germany’s federal administration, with workstreams covering configuration, vulnerability management, logging, detection, and mobile device control.