
News
-
Jisc reports 16,000 cyber incidents in education and research during 2025
Jisc says it identified 16,000 cyber incidents across UK education and research in 2025 and found more than 144,000 exposed credential combinations in early 2026.
-
Legal Aid Agency finds older case and probation records in stolen data
The Legal Aid Agency says forensic work on its 2025 cyberattack has identified about 250,000 pre-2007 records and some probation data among exfiltrated material.
-
ICO orders Metropolitan Police to improve controls over unapproved intelligence platform
The UK information regulator has reprimanded the Metropolitan Police and issued an enforcement notice after staff used an unauthorised retail crime intelligence platform to process personal information.
-
Censys finds exposed AI services growing while industrial systems remain reachable
A new internet-wide survey from Censys records a 63% increase in exposed AI infrastructure over nine months and around 134,000 reachable industrial control hosts.
-
French cyber authority flags Citrix vulnerabilities across three product lines
CERT-FR has warned of newly documented vulnerabilities affecting Citrix XenServer, Workspace for Windows and UniconOS, covering code execution, privilege escalation and other risks.
-
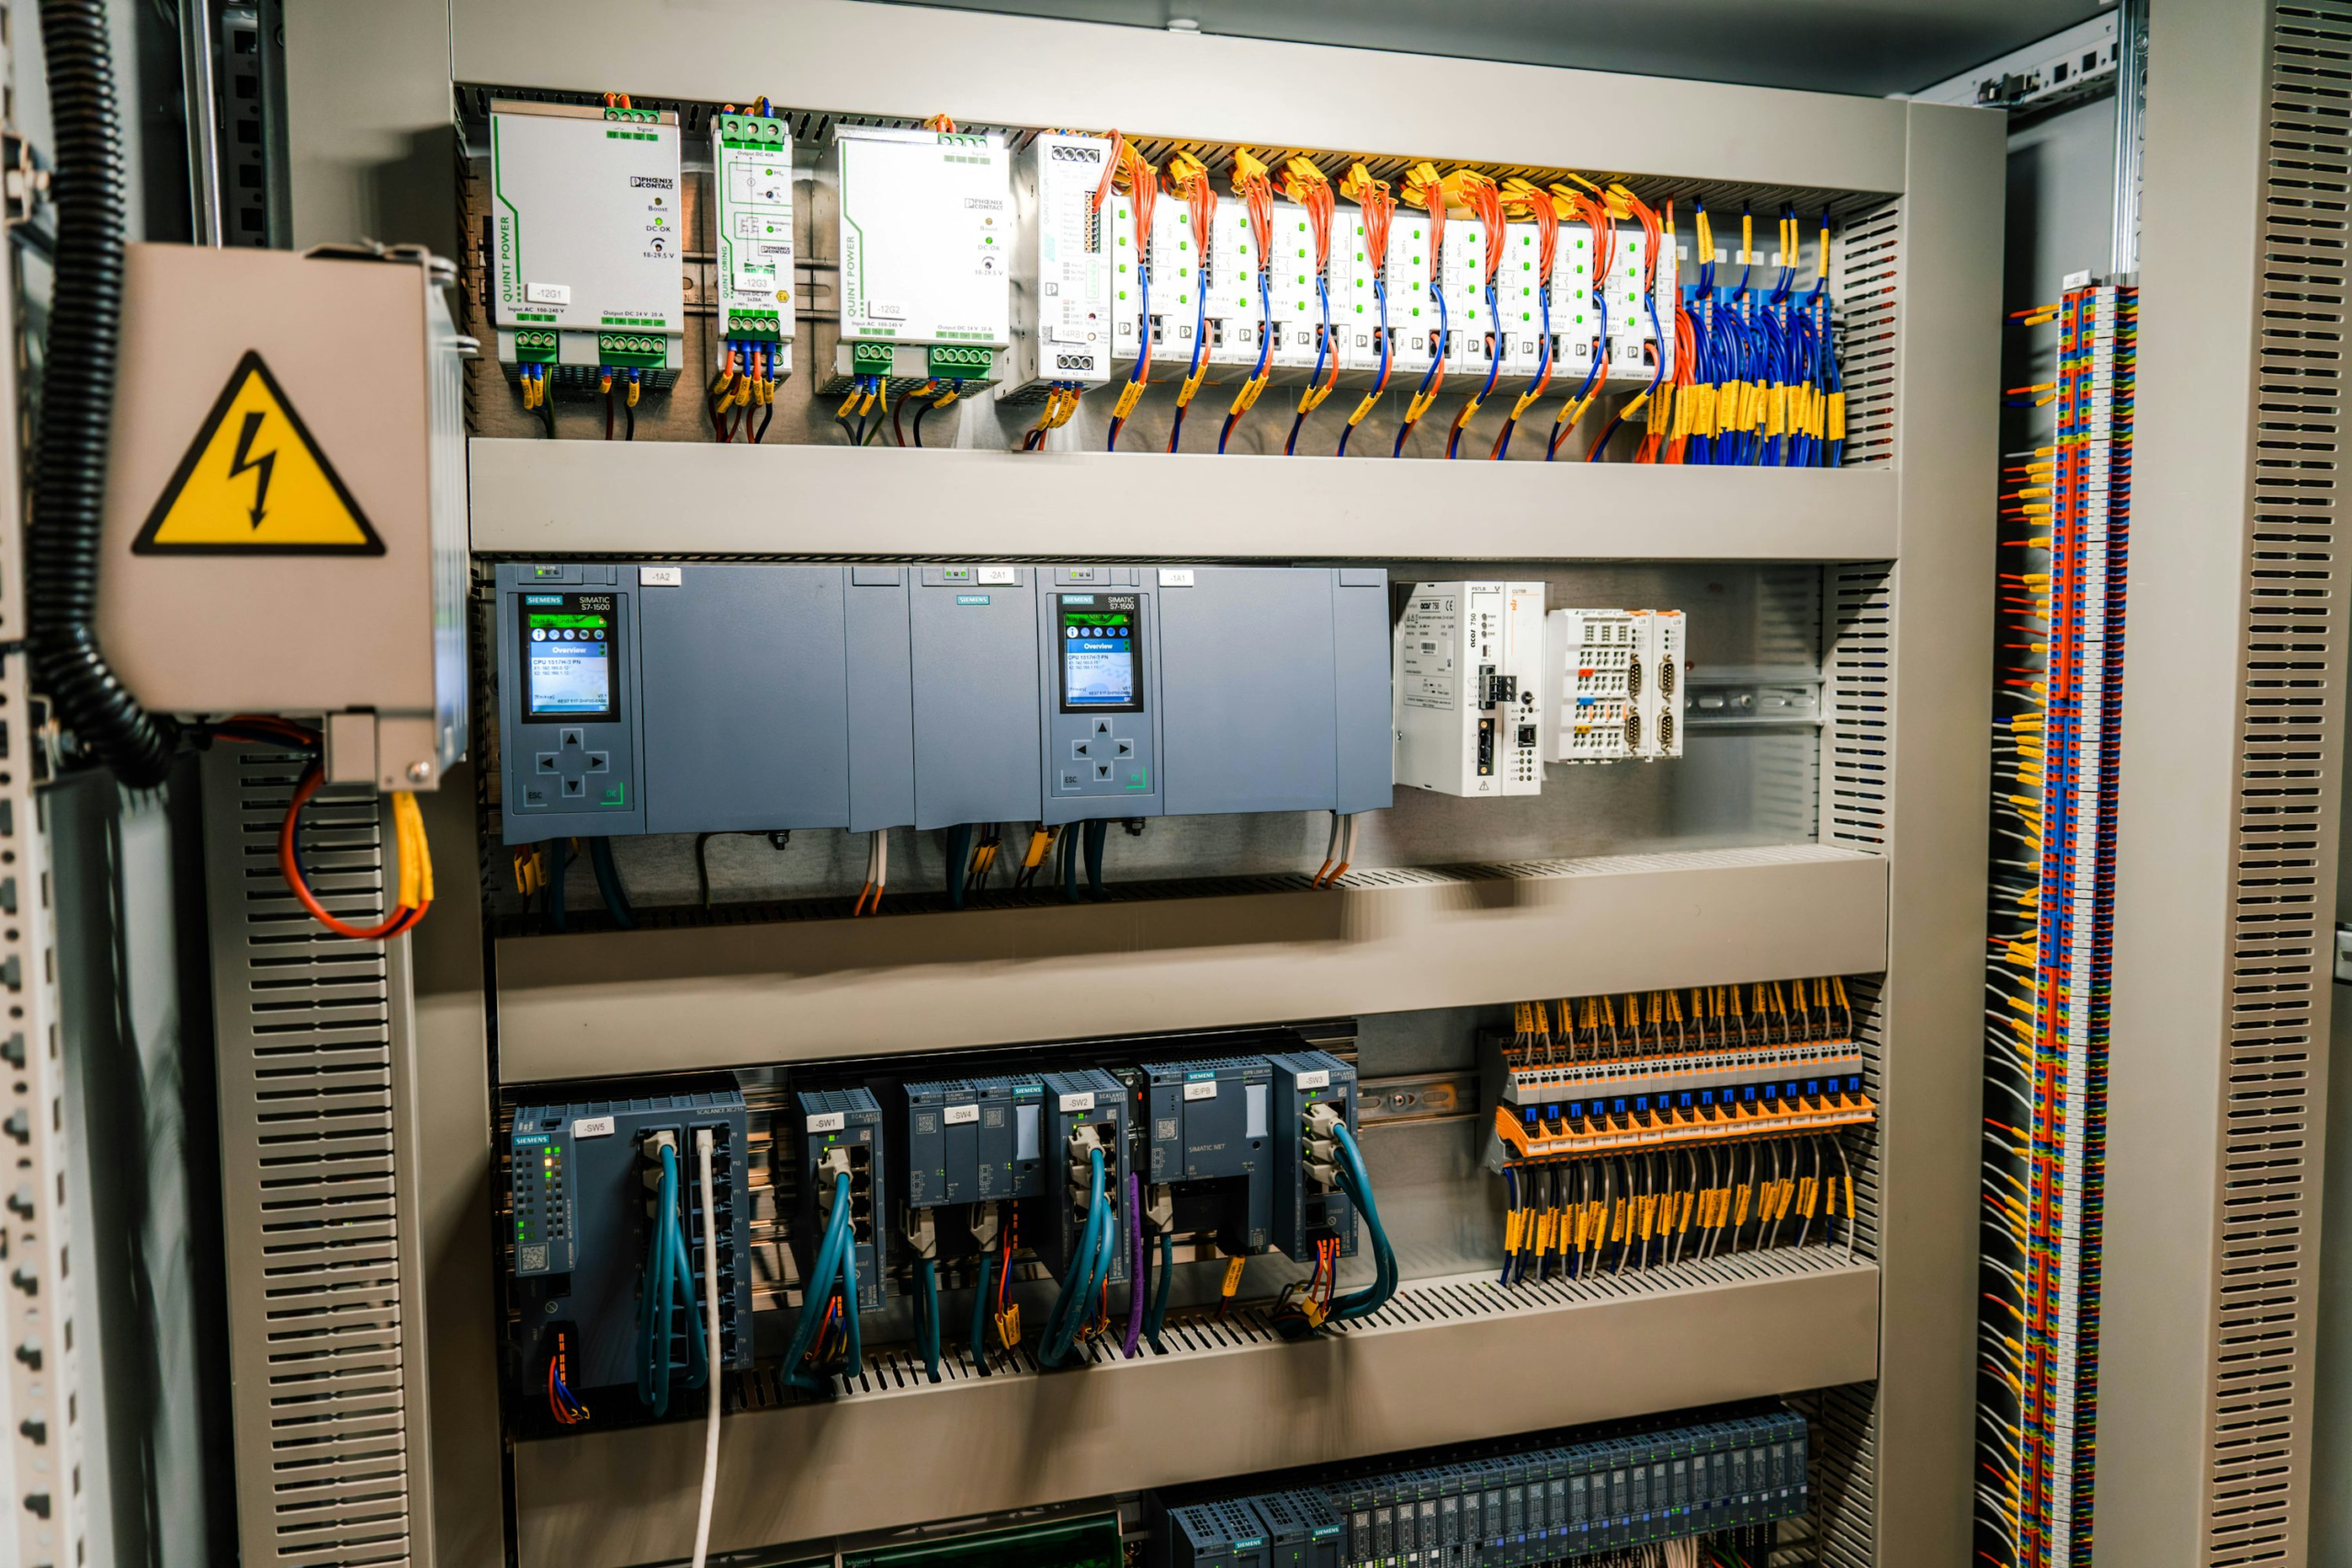
Siemens warns of critical flaws in S7-1500 multifunctional module subsystem
Siemens has disclosed vulnerabilities in the GNU/Linux environment of a SIMATIC S7-1500 multifunctional module, with some fixes still in preparation and compensating controls advised.
-
French regulator closes Google injunction after Gmail and cookie changes
France’s privacy regulator has closed a specific enforcement injunction against Google after account-creation disclosures and Gmail advertising changes, while reserving judgement on broader compliance.
-
Salt survey finds many enterprises cannot trace or stop unexpected AI-agent actions
Nearly half of respondents to a Salt Security study reported confirmed or suspected unauthorised AI-agent actions, while only a minority said they could trace complete agent activity or contain problems automatically.
-
LiteLLM gateway flaws exposed administrators, server files and AI provider keys
Check Point Research has detailed two patched LiteLLM weaknesses that could permit administrative takeover, code execution or theft of provider API credentials through an enterprise AI gateway.
-

Anthropic tests whether small AI models could replicate across connected devices
Anthropic researchers found that small models can perform elements of autonomous replication using constrained hardware, but they did not demonstrate a self-sustaining uncontrolled AI worm.