
Identity & access
-
WSO2 API flaw faces active exploitation
A critical WSO2 authentication-bypass vulnerability patched in May is now being actively targeted with forged administrator tokens against exposed API-management systems.
-

NIST tightens identity token guidance
NIST has finalised guidance for protecting identity tokens and assertions used in cloud, federation, API, single sign-on, and workload-access environments.
-
GOV.UK passkeys reach 23 million users
GOV.UK One Login is extending passkeys to more than 23 million users, moving a major government identity service away from password-dependent authentication.
-
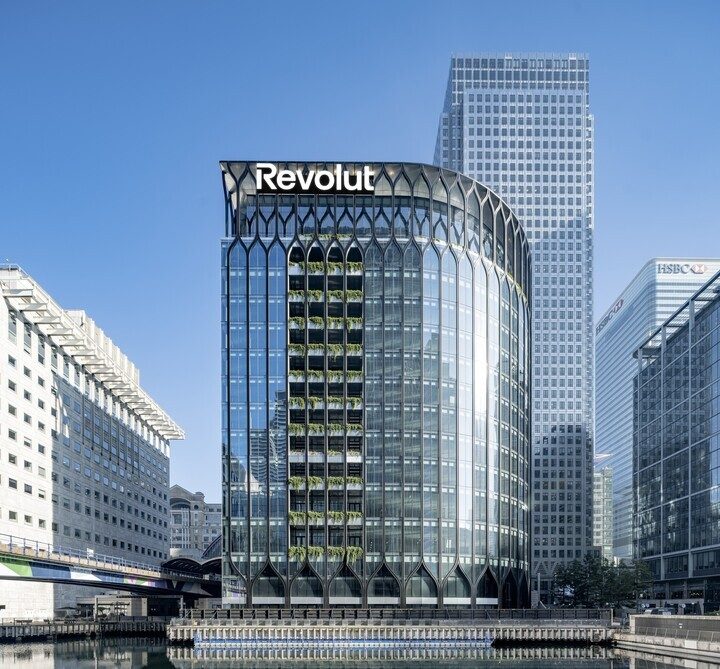
Revolut data exposed through fake requests
Revolut disclosed sensitive customer information after receiving fraudulent requests through an email domain associated with a legitimate government agency, exposing risk inside trusted disclosure workflows.
-
Phishing study challenges click-rate metrics
A 12-month dataset covering more than 123,000 users suggests falling phishing click rates can conceal credential exposure and weak reporting behaviour when simulation difficulty is ignored.
-

Check Point VPN flaws expose perimeter systems
Check Point has patched two critical VPN flaws that can permit unauthenticated remote code execution, with CERT-EU urging rapid remediation of internet-facing and perimeter appliances.
-

Phishing pages move inside victims’ browsers
Barracuda has analysed a campaign that builds malicious pages inside victims’ browsers using blob URLs after routing users through legitimate Microsoft services.
-

Fake Adobe pages install rogue ScreenConnect
Huntress has found two phishing attacks using fake Adobe Reader pages and browser-in-the-browser deception to install multiple rogue ScreenConnect clients for persistent remote access.
-

Fortinet fixes privileged access weaknesses
Fortinet has patched critical vulnerabilities affecting FortiMonitorOnSight and its Privileged Access Agent Chrome extension, including authentication bypass and browser-traffic proxy risks.
-
Vishing campaign steals Microsoft 365 sessions
A voice-phishing and extortion campaign is using fake IT calls, adversary-in-the-middle authentication, and residential proxies to take over Microsoft 365 and other SaaS accounts.