Summary
- A joint Commission–Europol analysis was published on 16 October.
- The report identifies interoperability, cloud, IoT, vehicle, AI and training challenges in digital forensics.
- Its recommendations describe capability needs, not new legally binding EU obligations.
European law enforcement agencies face persistent gaps in digital forensics tools, expertise, and cooperation as criminal evidence spreads across cloud services, connected devices, and vehicles, according to a new assessment produced by the European Commission with Europol. Published on 16 October, the analysis examines what investigators need to collect and interpret digital material across EU member states.
The study identifies standardisation and interoperability of forensic tools, challenges involving cloud and Internet of Things data, vehicle forensics, and the increasing relevance of artificial intelligence. It also addresses the skills required by first responders, specialist investigators, and legal professionals. The document offers recommendations to improve capabilities and cooperation; it does not itself introduce new investigative powers or binding requirements.
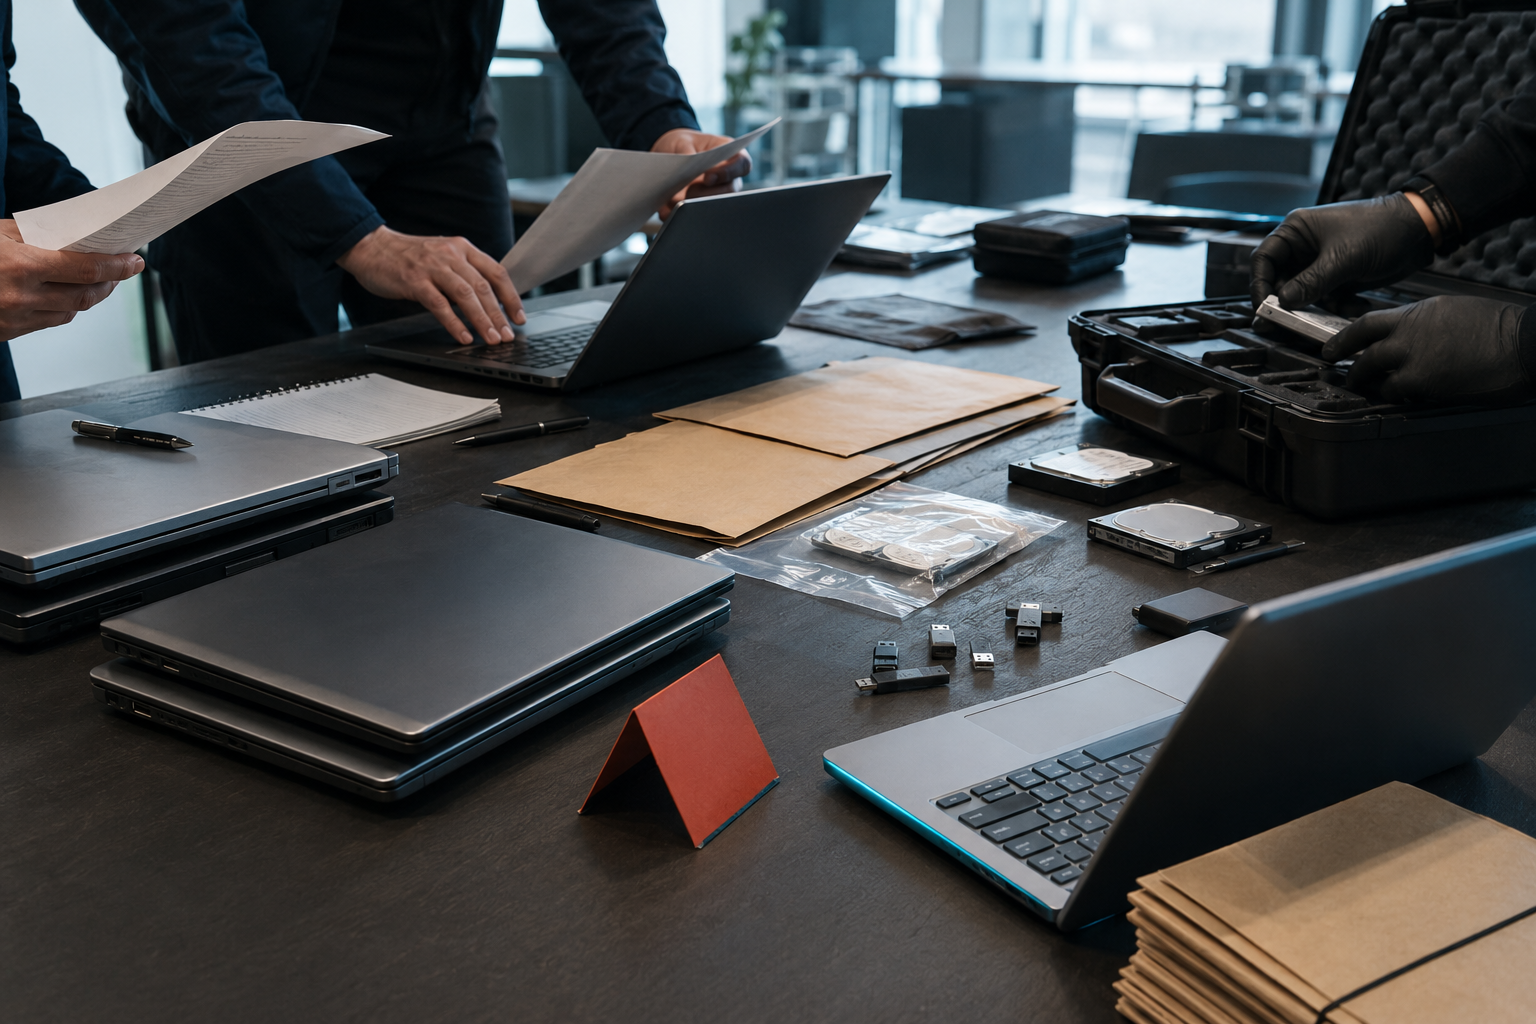
Digital evidence increasingly sits outside the device seized at a crime scene. A handset may contain tokens or references to records maintained by a cloud provider, while a vehicle can generate data across embedded systems, paired phones, and remote services. Obtaining reliable evidence therefore involves technical extraction, preservation, and interpretation, but also questions of lawful access, disclosure, and admissibility in court.
Fragmentation can arise even where investigators have competent teams. Tools may produce results in different formats, handle metadata inconsistently, or be unable to parse an emerging device category. Evidence acquired by one authority must be usable by another during cross-border investigations without losing provenance. Reproducibility and a documented chain of custody become especially important when specialist software performs automated processing that may be challenged in criminal proceedings.
Specialist work extends beyond the laboratory
The report highlights training needs among first responders as well as forensic experts. Decisions made before a specialist begins analysis can affect whether evidence survives: a device may be remotely wiped, connected accounts may expire, or logs may fall out of retention. At the same time, preserving data without over-collecting it can be necessary to comply with applicable legal limits and protect unrelated individuals’ rights.
Cloud evidence presents another challenge because investigators may depend on external providers, contractual arrangements, and technical interfaces that vary by service. Even when a court or competent authority can authorise access, the requested information may no longer exist or be held in a usable form. International operations add jurisdictional and language constraints. A shared process can reduce avoidable delay, but cannot remove the need for legal authority.
The Commission and Europol also consider artificial intelligence as an emerging influence on forensic work. Automated sorting and analysis may help deal with large datasets, although the accuracy, transparency, and defensibility of results require scrutiny. A model that finds patterns or assigns confidence scores is not a replacement for validation of the underlying evidence. In contested proceedings, methods may need to be explained and reproduced independently.
Consistent forensic output also depends on common data models, quality processes, and training, not solely on the purchase of the same tool. Data models, training, quality management, procurement practices, and mechanisms for testing new device types are also relevant. Smaller agencies may depend on shared facilities or cooperation with national specialists, while larger organisations may be able to maintain dedicated teams. The report frames such differences as capacity issues across the EU, rather than providing a single technical fix.
Digital forensics also affects incident response outside criminal prosecutions. Evidence preserved by a private organisation after ransomware or fraud may later form part of a police investigation, yet business logging systems and legal evidentiary procedures often have different objectives. Investigators need enough context to understand how records were generated, while organisations may need to preserve the original material and document handling. Cross-border cases become particularly difficult if each party assumes another organisation has retained logs or knows how a proprietary device formats its data.
The 16 October gap analysis documents both a capacity problem and an evidence-handling problem for cross-border investigations. Law enforcement may know that a digital system was abused yet struggle to obtain material that supports prosecution. The Commission and Europol’s recommendations set out where capability development should be directed; future funding, national adoption, and operational results will determine what changes in practice.