Summary
- ENTSO-E has proposed seven measures covering risk assessment, asset protection, crisis roles, cross-border recovery, and funding for electricity-grid security.
- E.DSO says incidents increasingly span operational technology, IT, communications, distributed energy resources, and market platforms.
- Both bodies are pushing resilience towards cross-organisational governance and system-wide recovery rather than isolated technical controls.
European electricity operators are pushing cyber, physical, and operational resilience towards a more integrated model as increasingly digital and interconnected power networks make it harder to treat major incidents as isolated technical failures.
ENTSO-E, which represents European electricity transmission system operators, set out seven recommendations for strengthening critical electricity infrastructure at the end of August, while distribution-system association E.DSO followed in early September with work on incident management spanning physical assets, operational systems, IT, communications, and cyber security.
The two publications address different parts of the electricity system but converge on a common problem: digitalisation, decentralisation, and interconnection are producing dependencies that do not fit neatly within traditional organisational or technical boundaries.
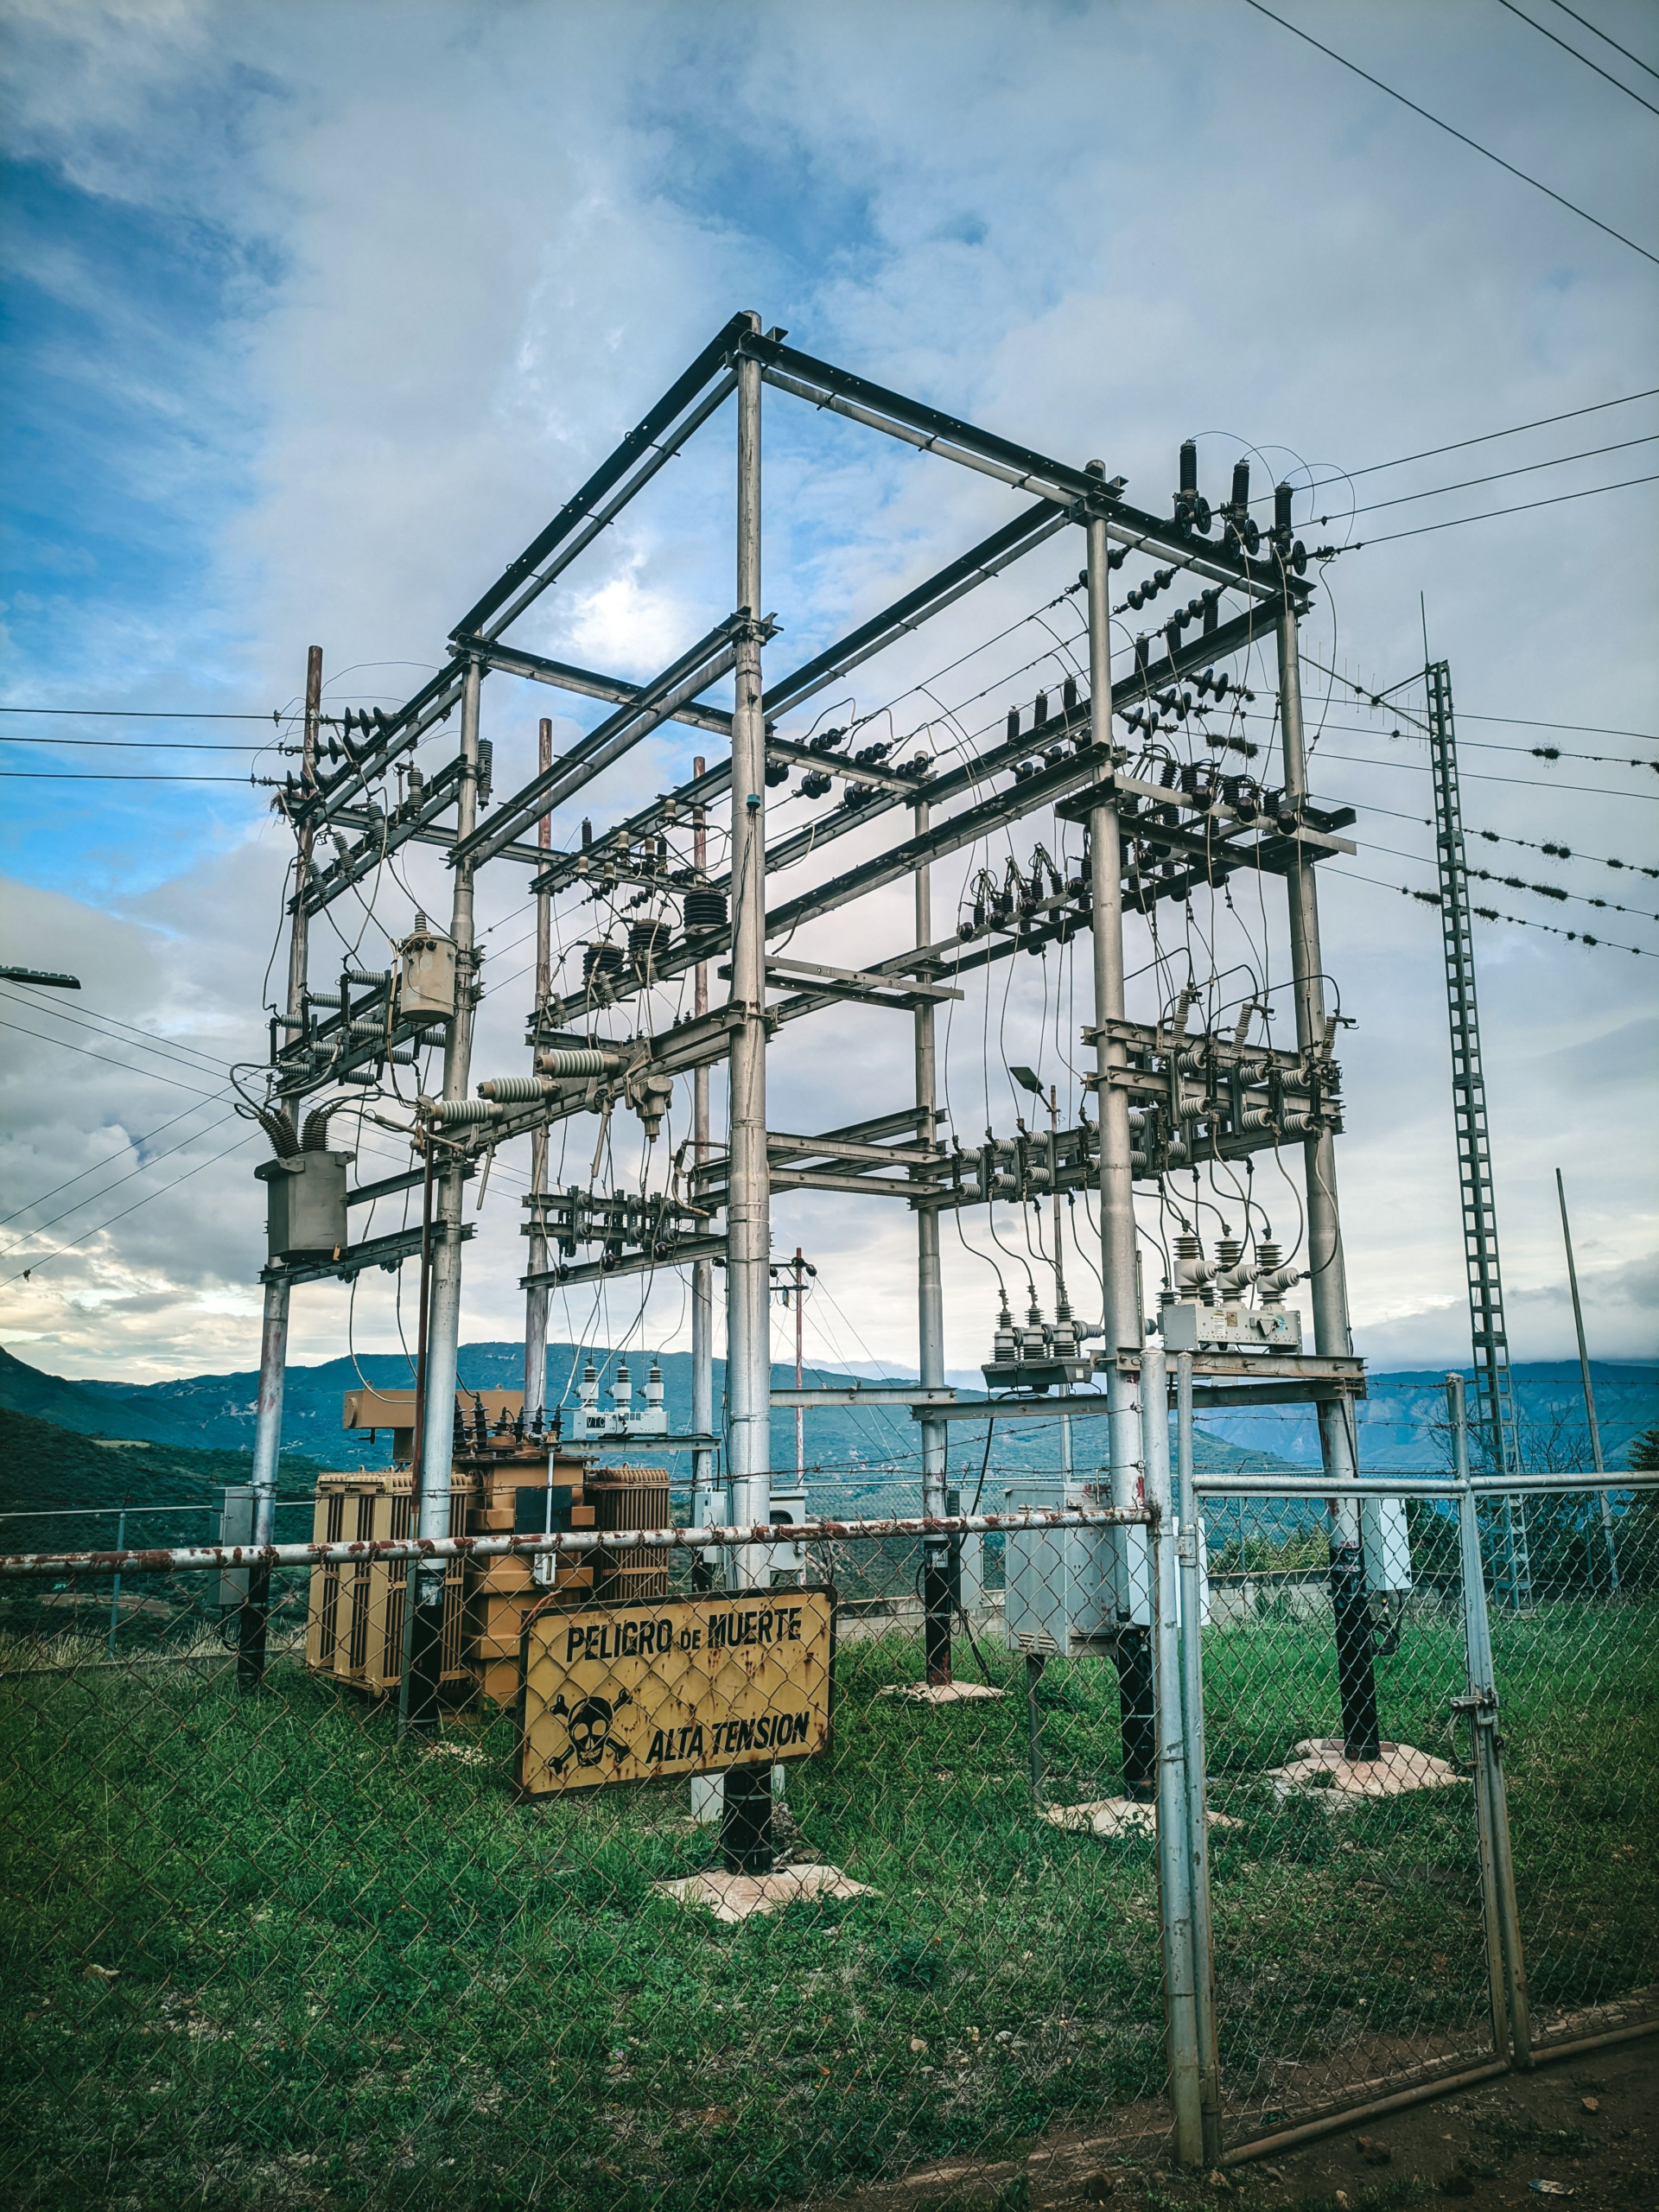
ENTSO-E’s position paper calls for harmonised risk assessments across the energy sector, minimum standards for protecting critical grid assets, clearer responsibilities between transmission operators and public authorities during crises, and stronger regional cooperation for protecting and recovering offshore infrastructure.
It also recommends faster cross-border deployment of specialised equipment and resources during emergencies, changes to transparency rules where publication of sensitive infrastructure information could create security risk, and dedicated funding for electricity-grid security investment.
The organisation frames energy security around three connected dimensions — security of supply, physical security, and cybersecurity — rather than treating cyber defence as a separate discipline. That distinction becomes more significant as electricity systems combine conventional grid equipment with remote management, communications links, distributed generation, software-based control, and digital market infrastructure.
E.DSO’s report reaches a similar conclusion from the distribution side. Drawing on a member survey and operational experience shared by Fluvius, Enedis, and Stedin, it says incident response increasingly requires multidisciplinary expertise and coordination across technical, operational, IT, and cyber functions.
The organisation says incidents may now span physical grid assets, operational technologies, communications systems, distributed energy resources, and market platforms. Its report emphasises anticipation and preparedness alongside response, as well as governance, knowledge sharing, and learning from incidents.
That governance problem is increasingly important because significant electricity incidents can cross corporate and national boundaries while authority remains divided among network operators, regulators, governments, service providers, infrastructure owners, and technology suppliers.
A technical response can therefore be complicated by questions over escalation, information sharing, recovery priorities, or responsibility even where individual organisations have mature internal procedures.
Europe’s power system is also becoming more dependent on organisations outside the traditional utility perimeter. Distributed energy resources, smart devices, communications providers, software platforms, contractors, and equipment suppliers can all affect the availability or behaviour of grid services.
The emerging approach does not erase the distinction between a cyberattack, physical sabotage, equipment failure, or capacity problem. Instead, it reflects the fact that different causes can produce overlapping operational consequences and require many of the same recovery relationships and resources.
Neither publication creates a new binding requirement. ENTSO-E’s paper was published on 31 August and E.DSO’s on 3 September, making this a synthesis of current European resilience work rather than a single new policy announcement. Together, however, they show electricity-sector bodies placing greater emphasis on the governance and coordination needed to keep an increasingly digital power system operating through disruption.