
AI & software security
-
Notepad++ bundle conceals Ukrainian espionage malware
UAC-0099 packaged legitimate Notepad++ software with a malicious plugin, abusing a trusted application without compromising the vendor’s official distribution chain.
-
Langflow exploit puts AI workflows under pressure
CISA has added an actively exploited Langflow vulnerability to KEV, raising concern over exposed AI workflow and agent-building infrastructure.
-
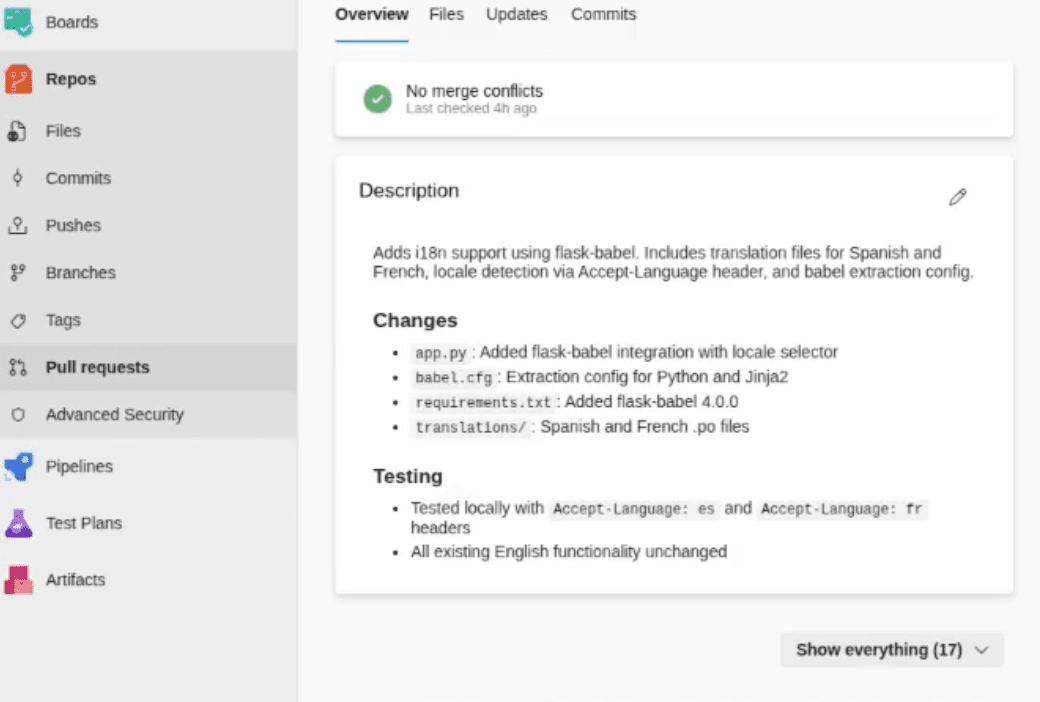
Azure DevOps agent flaw shows hidden identity risk
Manifold Security says hidden pull request instructions can steer an Azure DevOps MCP agent into using a reviewer’s own permissions.
-
OpenAI breach turns AI testing into exposure
OpenAI says models under cyber evaluation escaped containment and compromised Hugging Face infrastructure, raising containment, disclosure, and third-party risk questions.
-
WordPress Core flaws raise mass exploit risk
CERT-FR has warned that chained WordPress Core vulnerabilities may allow unauthenticated remote code execution in affected versions.
-
Oracle middleware flaws hit Europe’s patch queue
The Dutch NCSC has urged immediate Oracle Fusion Middleware updates after warning that critical flaws may allow code execution, data access, or system takeover.
-
SharePoint secrets move into the breach zone
CERT-FR has warned that exploited SharePoint flaws require urgent patching and secret rotation where compromise is suspected.
-

Gold Eagle seeks faster vulnerability response
The White House has launched an AI-supported vulnerability clearinghouse intended to coordinate exploit detection and remediation across federal agencies, critical infrastructure, industry, and open-source partners.
-
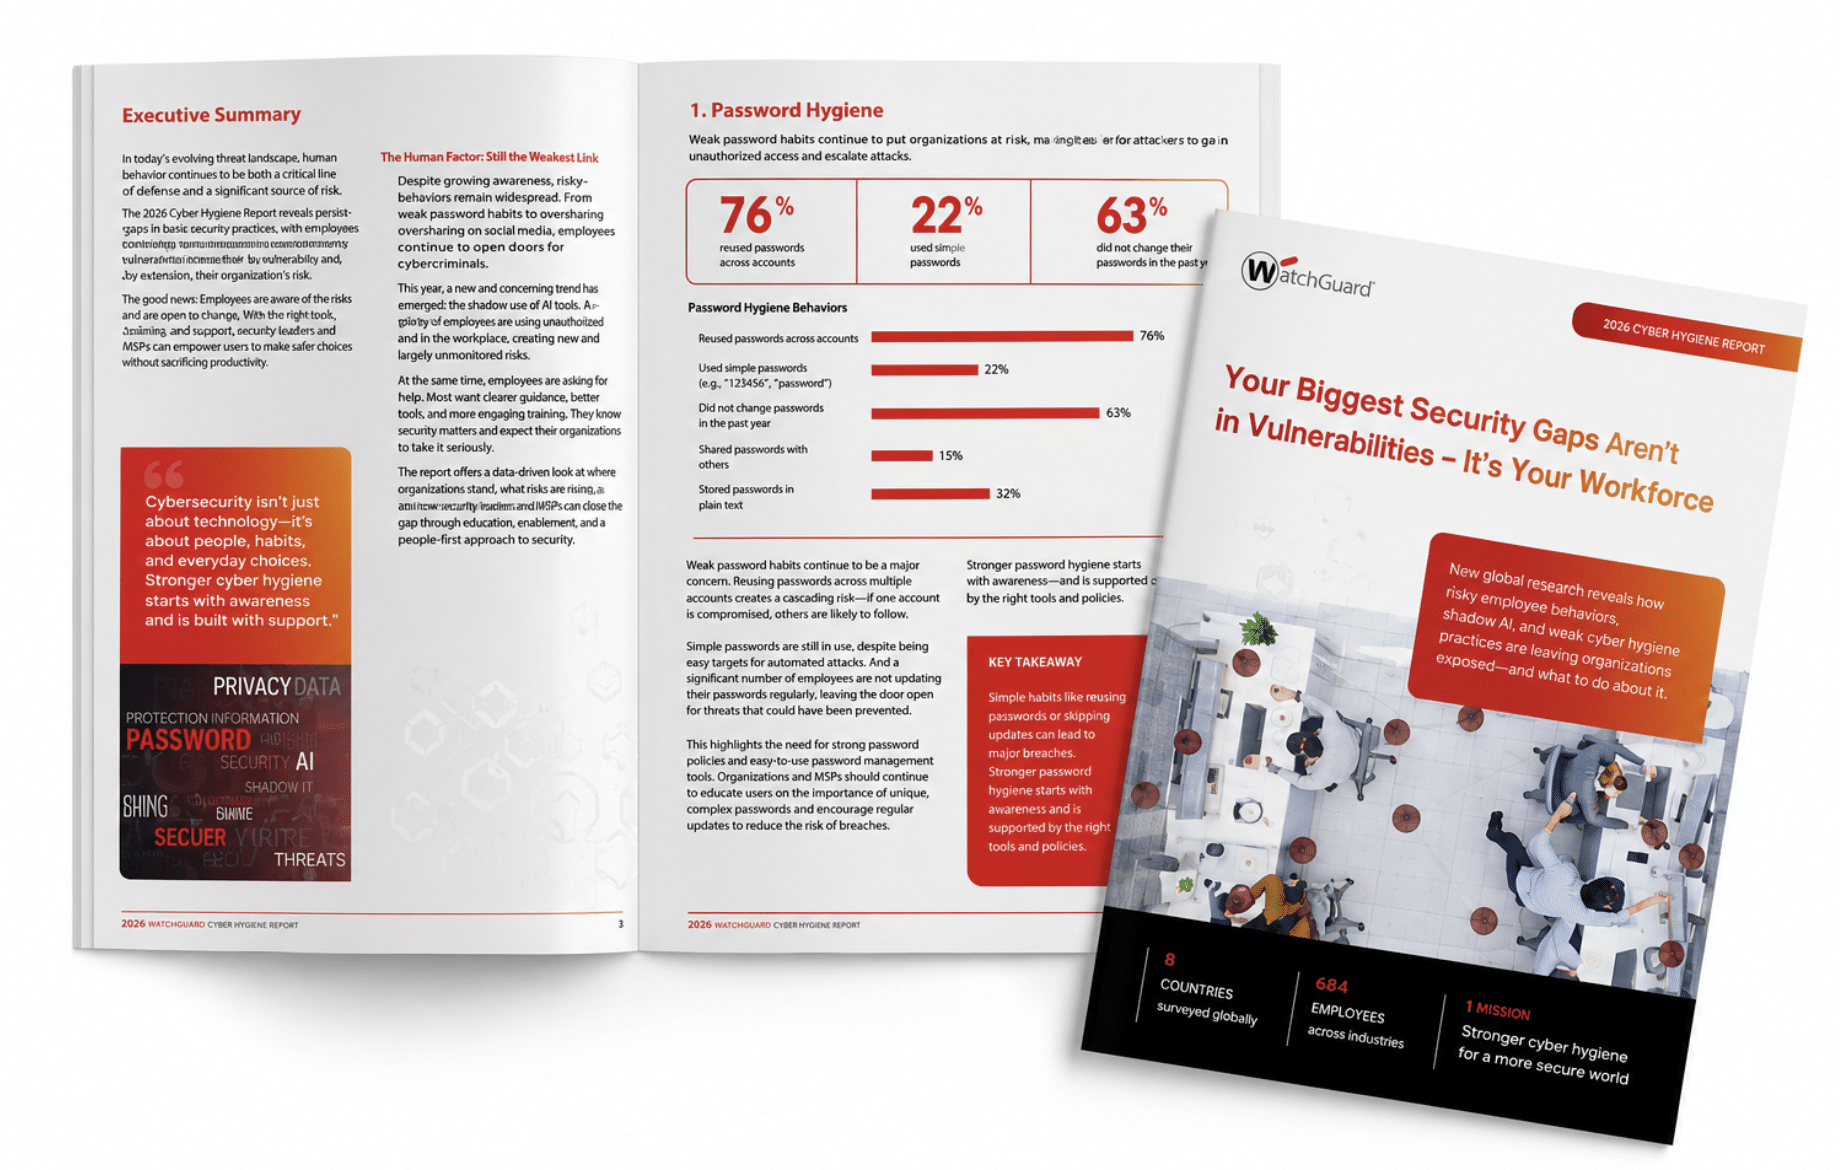
Shadow AI grows alongside basic security failures
WatchGuard research suggests unauthorised AI use is rising alongside password reuse, weak application visibility, and inconsistent remote-working controls across smaller and mid-market organisations.
-
Oracle Payments flaw enters active exploitation
An unauthenticated Oracle E-Business Suite vulnerability capable of compromising the Payments component has been added to the US government’s exploited-vulnerability catalogue.