
AI & software security
-

Windows zero-day hits European defence targets
Microsoft has patched a Windows privilege-escalation zero-day that Check Point says was exploited in a Lazarus-linked campaign targeting defence, aerospace, and aviation organisations, including victims in Europe.
-

SAP patches critical Commerce Cloud flaw
SAP’s August security release fixes a maximum-severity authorisation flaw in Commerce Cloud alongside critical vulnerabilities affecting manufacturing and core enterprise platforms.
-
GitHub broadens Dependabot malware alerts
GitHub has expanded Dependabot’s malicious-package coverage beyond npm, allowing dependencies across most supported ecosystems to be matched against a wider pool of known malware advisories.
-
Poisoned logs can redirect privileged AI agents
DEF CON research shows how attacker-controlled information inside trusted operational systems can influence AI agents that have permission to change cloud and security environments.
-
OpenAI widens controlled cyber-model access
OpenAI has launched GPT‑5.6‑Cyber through an expanded Daybreak programme, giving approved researchers access to a model deliberately trained to answer substantially more advanced dual-use cyber requests.
-
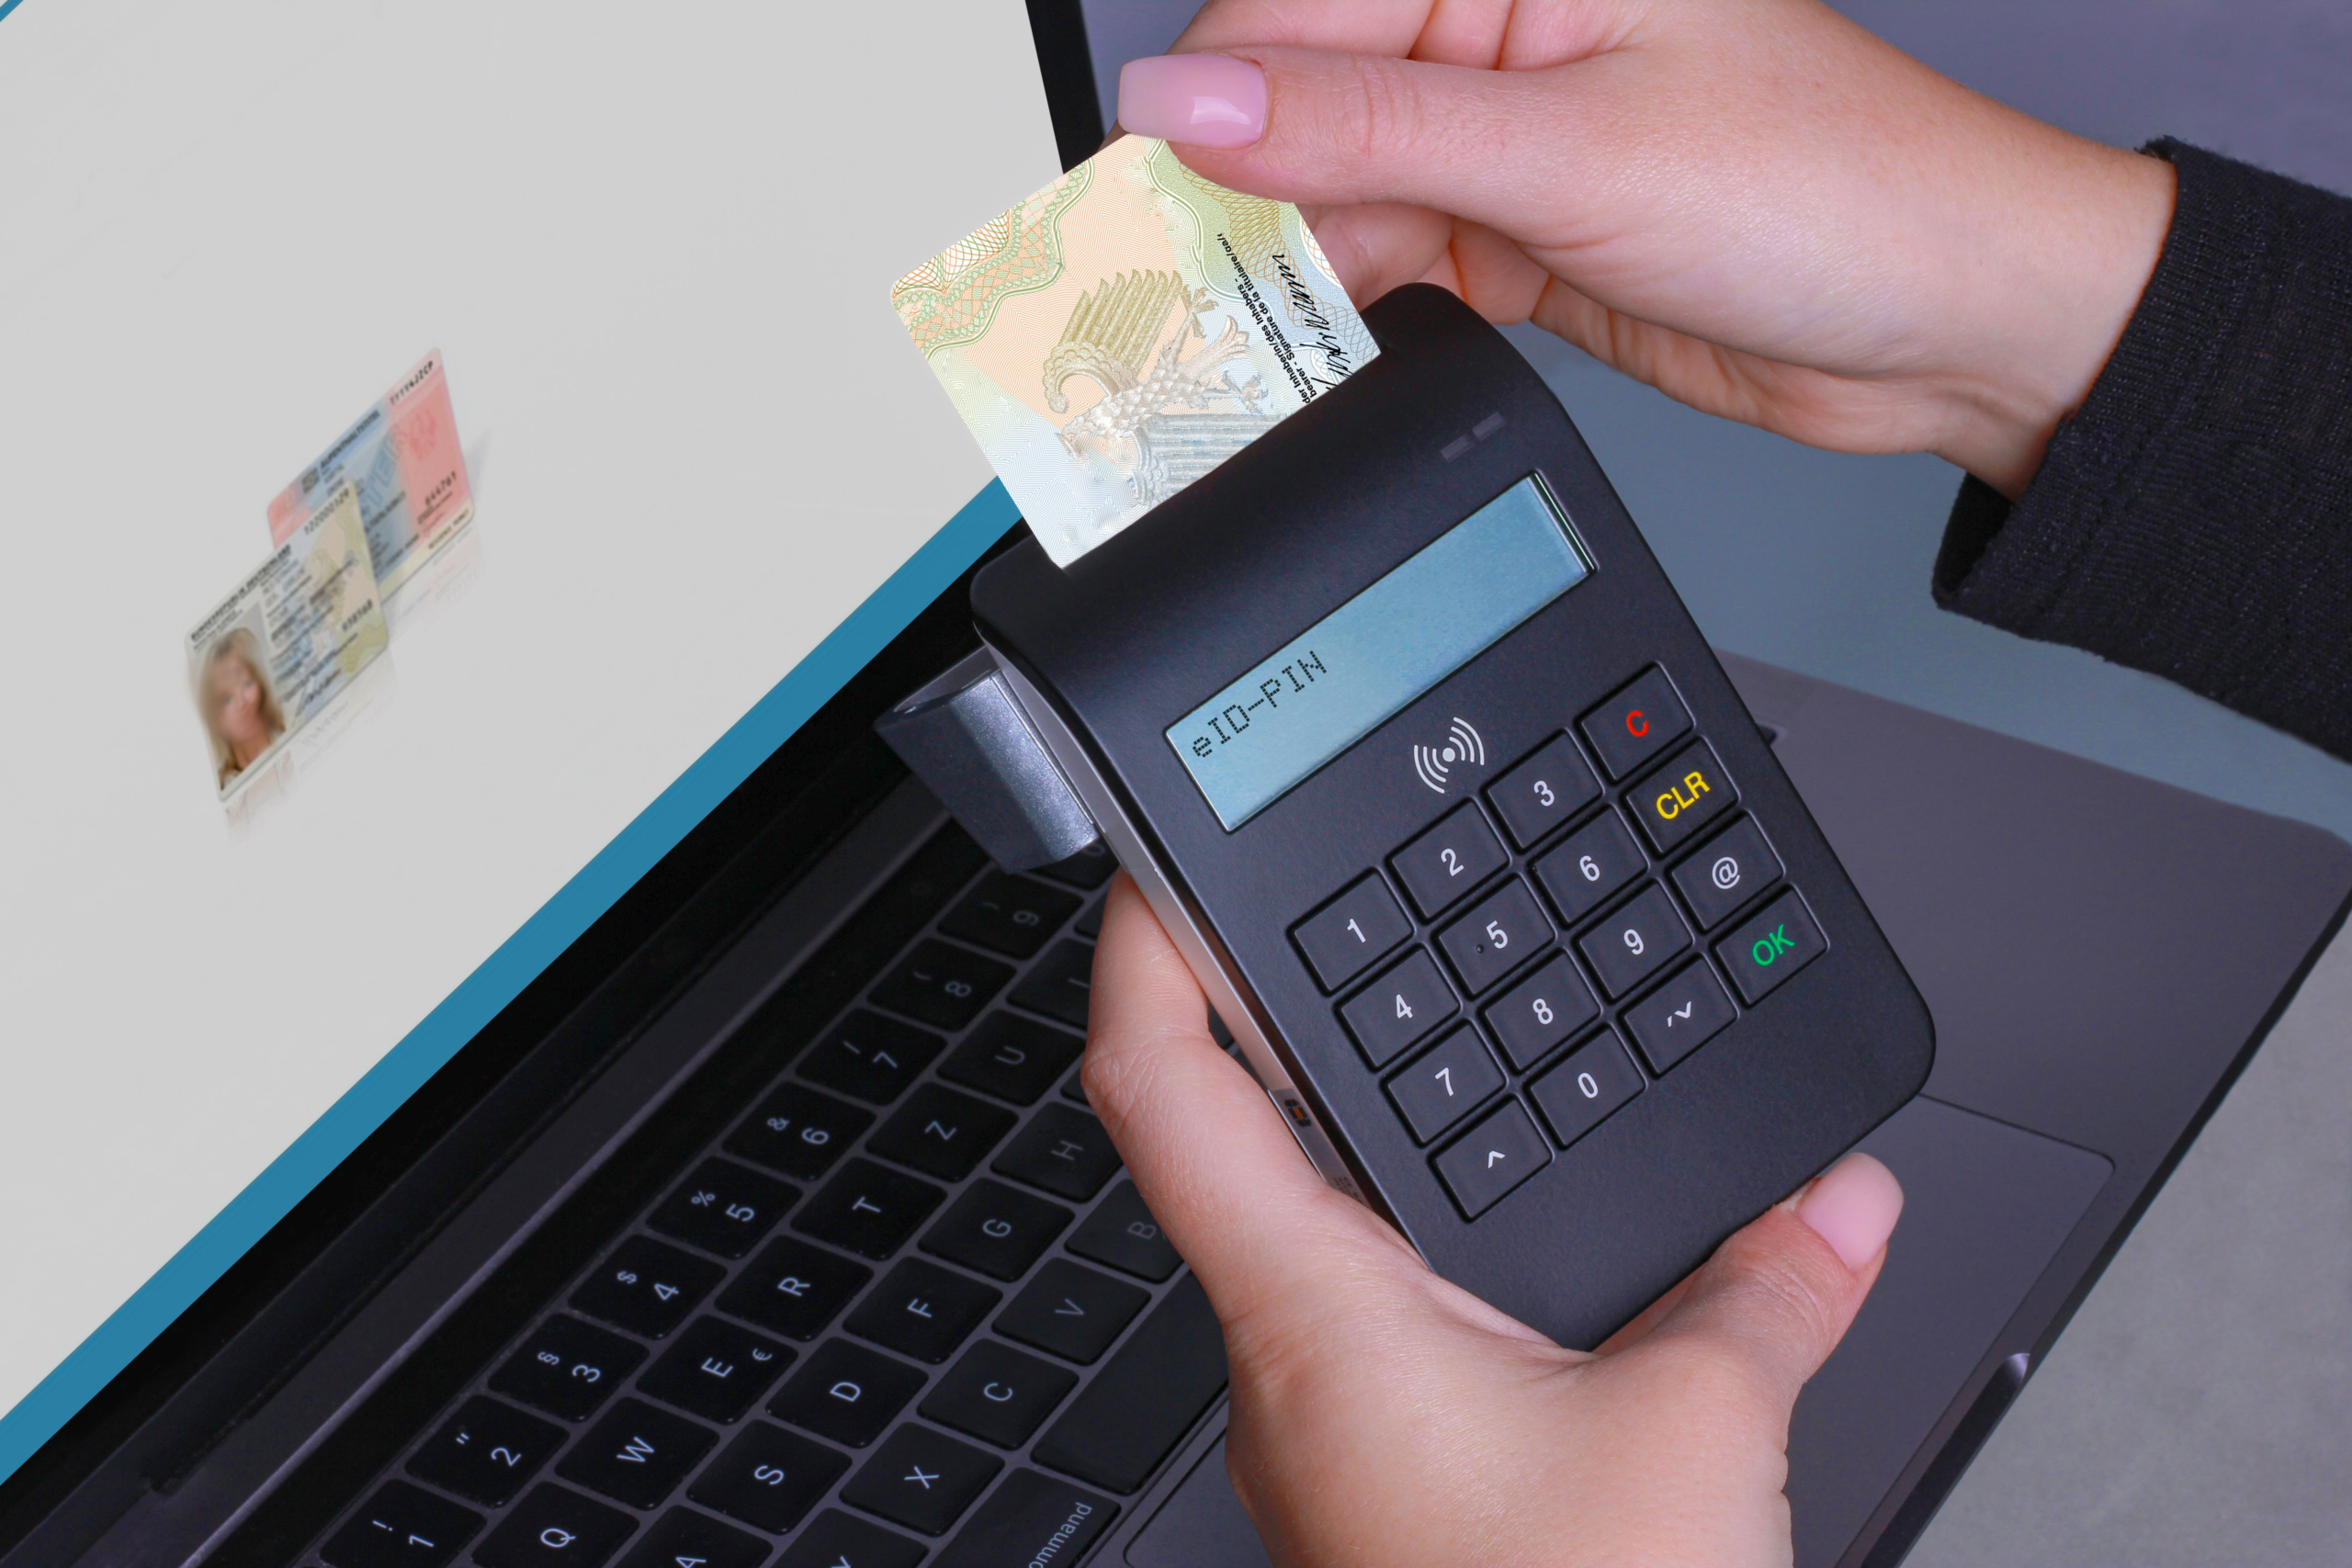
Belgian eID flaws exposed trust-chain weaknesses
Flaws in software connecting Belgian electronic identity cards to web services exposed card data, PIN handling, signing functions, and local code execution across a widely deployed digital-trust system.
-
Belgian eID flaws exposed trust-chain weaknesses
Flaws in software connecting Belgian electronic identity cards to web services exposed card data, PIN handling, signing functions, and local code execution across a widely deployed digital-trust system.
-
CSS research crosses email and AI boundaries
PortSwigger research shows how weaknesses in webmail HTML and CSS handling can escape message boundaries, manipulate trusted interfaces, expose information, and influence AI browsers consuming email content.
-
RovoBlast exposes AI agent permission risks
A fixed flaw in Atlassian Rovo showed how a crafted link could place attacker instructions inside a trusted AI session and use the agent’s legitimate access across connected enterprise services.
-
OpenAI tightens Astra controls over cyber risk
OpenAI has paused Astra-related internal work that does not meet stronger security requirements after preliminary evaluations left it unable to rule out its highest cybersecurity capability threshold.